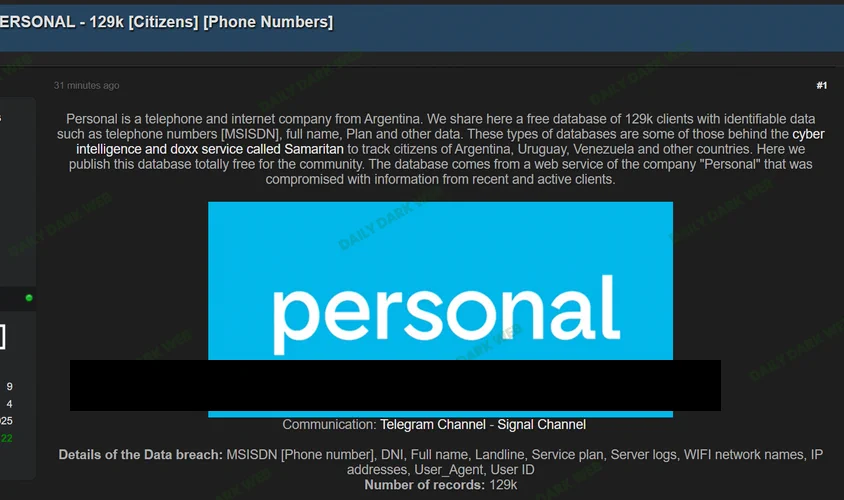
Dark Web Intelligence on X: "🇦🇷 ARGENTINA PERSONAL TELECOM DATABASE FREE DUMP CLAIM (~129,000)
The underground listing alleges fields including:
* Server logs, Wi‑Fi network names, IPs, User-Agents, and user IDs
We assess this as an unverified threat-actor claim involving alleged Personal (Argentina) customer data, NOT confirmation of a compromise of Personal systems.
If authentic and non-public, DNI + phone + plan data could support SIM-swap fraud, phishing, and doxxing-style abuse.
#DDW #DarkWeb #Argentina #Personal #Telecom #DataBreach #PII #ThreatIntelligence #CyberSecurity"
🇦🇷 ARGENTINA PERSONAL TELECOM DATABASE FREE DUMP CLAIM (~129,000)
The underground listing alleges fields including:
* Server logs, Wi‑Fi network names, IPs, User-Agents, and user IDs
We assess this as an unverified threat-actor claim involving alleged Personal (Argentina) customer data, NOT confirmation of a compromise of Personal systems.
If authentic and non-public, DNI + phone + plan data could support SIM-swap fraud, phishing, and doxxing-style abuse.
The full story
This article is one source in a clustered incident — the cluster page carries the summary, timeline and every other outlet covering it.
