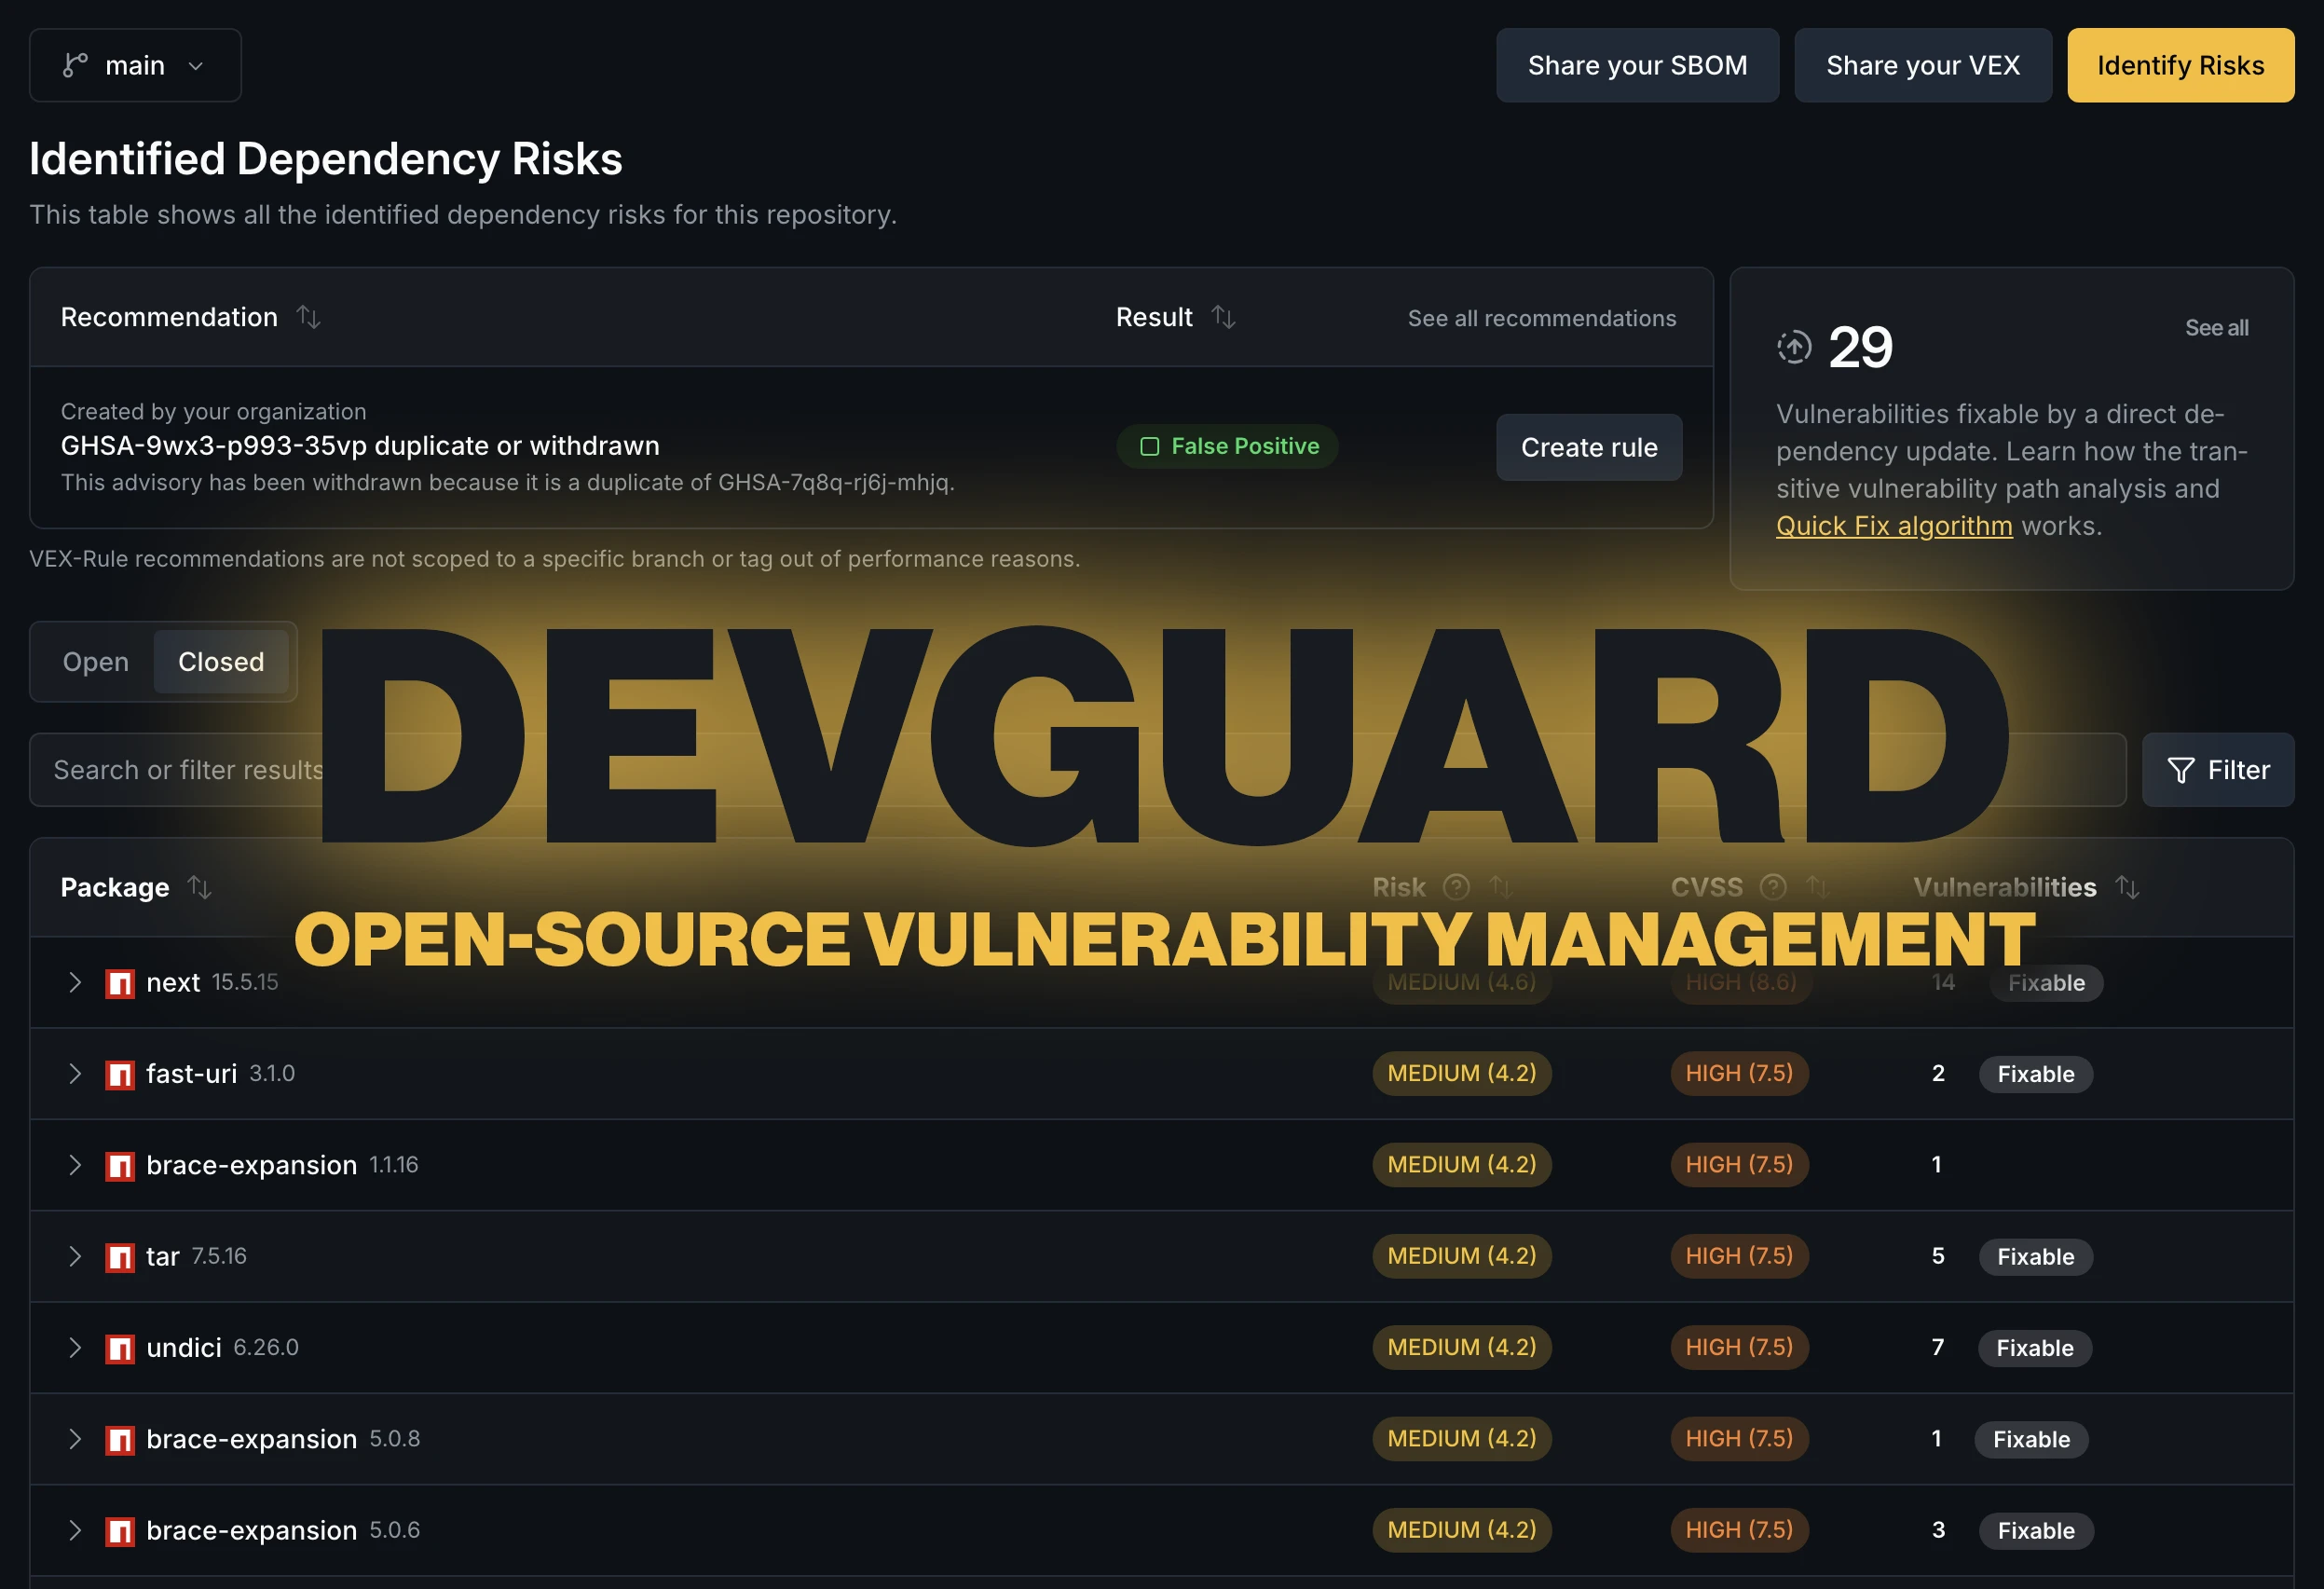
DevGuard is a free, open source vulnerability management platform that collects a software project’s security findings in one place, ranks them by risk, and tracks them. It’s an OWASP Incubating Project, and anyone can self-host it.
One command line, six scans
DevGuard runs secret scanning, static code analysis, dependency checks against known CVEs, infrastructure-as-code checks, container scanning, and license checks through one CLI that wraps existing open source tools. Teams already using Trivy, Grype, or Semgrep can skip the built-in scanners and upload CycloneDX SBOMs (machine-readable lists of the components in a build) or SARIF results. Findings sync both ways with GitHub Issues, GitLab Issues, and Jira, where developers triage them with slash commands.
Blocking packages before they arrive
The Dependency Firewall proxies the npm, Go, and Python registries and blocks known-malicious and vulnerable packages before download. DevGuard also handles VEX, short for Vulnerability Exploitability eXchange, a statement of whether a product is actually affected by a given CVE. Reusable VEX rules let a team dismiss a recurring false positive once across projects.
DevGuard publishes SBOM and VEX data at live links that update when new CVEs appear, and it generates evidence for ISO 27001, the EU Cyber Resilience Act, BSI IT-Grundschutz, and SLSA.
DevGuard is available for free on GitHub .
20 open-source cybersecurity tools to keep your team ready for anything
GitHub CISO on security strategy and collaborating with the open-source community
The full story
This article is one source in a clustered incident — the cluster page carries the summary, timeline and every other outlet covering it.
