 Back Cybersecurityconnect.Au
Hacked! AI recruitment platform Bullhorn responding to cyber incident
Online recruitment firm Bullhorn is continuing to respond to a cyber security incident that saw the platform taken offline over the weekend.
The company began reporting syncing issues on its CRM platform on October 16 via its status portal .
“We’re currently experiencing a system-wide outage affecting the Bullhorn platform. Users may be unable to access Bullhorn or may experience errors and degraded performance,” the company said.
“Our teams are actively working to restore service as quickly as possible. We’ll post updates here at status.bullhorn.com as soon as we have more information.”
The company continued to experience issues over the following hours. Bullhorn advised several times that it was “continuing to investigate the issue”; however, by 15.28 the same day the company was able to confirm it was responding to a cyber attack.
“We have detected a cyber incident on the Bullhorn Platform. We have temporarily disabled access to our systems to contain the activity while we investigate further,” the company said.
“We are working with cyber security specialists from CrowdStrike and will resume access when the activity is safely resolved.
“We understand how disruptive systems interruptions are to your business and the criticality of data security. We ask for your patience as we work to resolve this issue as quickly as possible.”
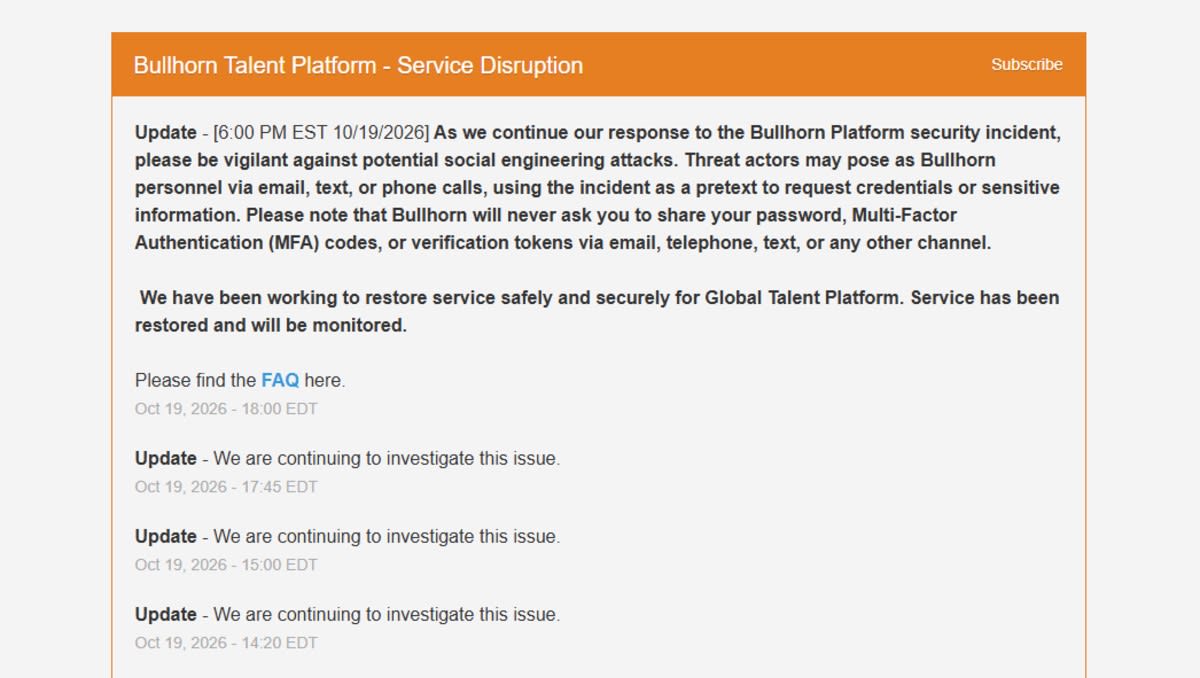
The disruption to Bullhorn’s platform continued throughout October 18 and 19. Services were restored just before 17.00 on the 19th.
“We have been working to restore service safely. AUS, EMEA/UK and US are all now online. We have recently implemented fixes for customers using SSO. Customers who were experiencing challenges previously are asked to test again and log a ticket via support if their SSO login issues persist,” Bullhorn said.
“Additionally, as the data centres are coming back online, some users may find they get into a loop as they attempt to update their passwords.”
The company has also warned customers to beware of any further malicious activity.
“As we continue our response to the Bullhorn Platform security incident, please be vigilant against potential social engineering attacks,” Bullhorn said
“Threat actors may pose as Bullhorn personnel via email, text, or phone calls, using the incident as a pretext to request credentials or sensitive information.”
As late as early this morning, some customers were expressing concern regarding the incident.
“Our Bullhorn system was offline all weekend and didn't come back on until 9 AM this morning (an hour after our workday started). Everything relating to the admin of the system, all API's for third-party integrations and large parts of the system still remain offline and unusable,” said one customer on .
“Absolute s*** show in any regard. They have advised they had to take the system down and pretty much flatten some of their infrastructure to stop the attack and bring system components back up ‘safely’. Screams Ransomware to me, but will wait on the official post-mortem, as that's just me speculating at this stage.”
No threat actor has yet claimed responsibility for the incident.
Bullhorn has now published an FAQ explaining the incident, its impact, and the company’s response so far.
“Our forensic investigation is ongoing, and we have not yet determined whether customer data was exfiltrated. If we determine that your data was affected, we will you as soon as possible,” Bullhorn said.
“We are committed to being transparent and will findings as they become available, and we will comply with applicable notification obligations.”
David Hollingworth has been writing technology for over 20 years, and has worked for a range of print and online titles in his career. He is enjoying getting to grips with cyber security, especially when it lets him talk Lego.
The full story
This article is one source in a clustered incident — the cluster page carries the summary, timeline and every other outlet covering it.
