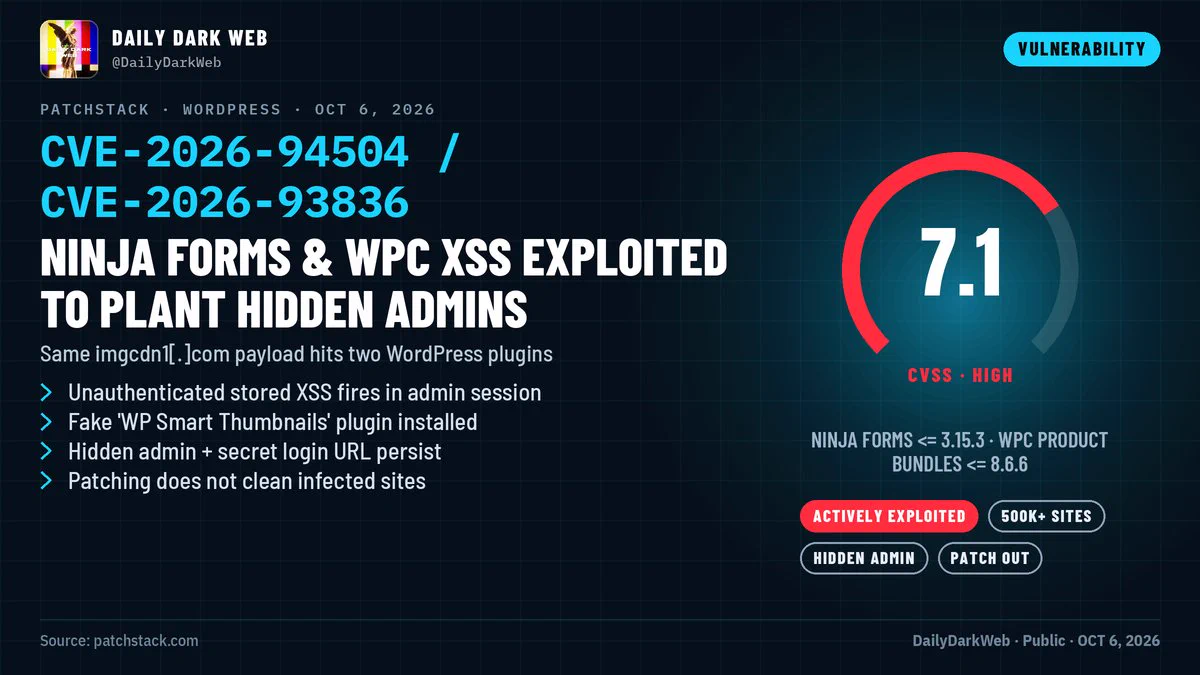
Dark Web Intelligence on X: "🚨 HACKERS EXPLOIT NINJA FORMS AND WPC PRODUCT BUNDLES XSS FLAWS TO PLANT HIDDEN WORDPRESS ADMINS
Patchstack reports an active campaign abusing two stored XSS bugs in unrelated WordPress plugins, both delivering the same JavaScript payload from imgcdn1[.]com.
• CVE-2026-94504: Ninja Forms ≤ 3.15.3 (500K+ installs), fixed in 3.15.4
• CVE-2026-93836: WPC Product Bundles for WooCommerce ≤ 8.6.6 (30K+ installs), fixed in 8.6.7
• Both rated CVSS 7.1; the payload is injected without login and fires when an admin views the poisoned submission or order
• It installs a fake "WP Smart Thumbnails" plugin, creates a visible admin plus one hidden from the Users screen, adds a secret login URL and an unauthenticated file manager
• First seen Oct 4 (WPC) and Oct 5 (Ninja Forms)
Patchstack says exploitation is limited so far, and neither CVE is in CISA KEV at handoff. Updating stops new infections but does not remove an existing one: check for unknown admins, must-use plugins and the fake thumbnail plugin.
#DDW #DarkWeb #CyberSecurity #WordPress #CVE #PatchNow"
🚨 HACKERS EXPLOIT NINJA FORMS AND WPC PRODUCT BUNDLES XSS FLAWS TO PLANT HIDDEN WORDPRESS ADMINS
Patchstack reports an active campaign abusing two stored XSS bugs in unrelated WordPress plugins, both delivering the same JavaScript payload from imgcdn1[.]com.
• CVE-2026-94504: Ninja Forms ≤ 3.15.3 (500K+ installs), fixed in 3.15.4
• CVE-2026-93836: WPC Product Bundles for WooCommerce ≤ 8.6.6 (30K+ installs), fixed in 8.6.7
• Both rated CVSS 7.1; the payload is injected without login and fires when an admin views the poisoned submission or order
• It installs a fake "WP Smart Thumbnails" plugin, creates a visible admin plus one hidden from the Users screen, adds a secret login URL and an unauthenticated file manager
• First seen Oct 4 (WPC) and Oct 5 (Ninja Forms)
Patchstack says exploitation is limited so far, and neither CVE is in CISA KEV at handoff. Updating stops new infections but does not remove an existing one: check for unknown admins, must-use plugins and the fake thumbnail plugin.
Worth adding for anyone running WPC Product Bundles: after updating, check Users for admin accounts you don't recognise. The patch closes the hole but doesn't remove an admin that was already created.
The full story
This article is one source in a clustered incident — the cluster page carries the summary, timeline and every other outlet covering it.
