 Back Infostealers
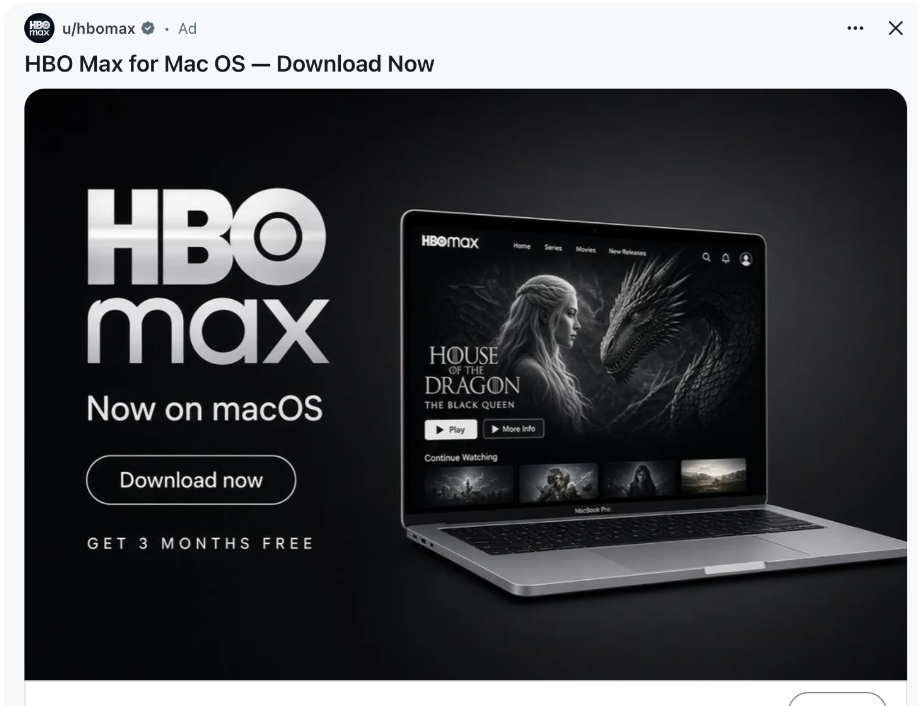
HBO Max ads on a compromised Reddit account exposed a massive PasteSwitch ClickFix operation
Through joint research conducted by Hudson Rock and Kirk from ADAMnetworks (with additional thanks to Tuxxin from Whack.sh and Emiliano from The Matrix Project), we can confirm this incident is part of a massive, cross-platform delivery operation we are dubbing PasteSwitch . This operation spans macOS stealers, Windows loaders, deceptive TLS tactics, and contract-controlled cryptocurrency clippers.
The Lure: Exploiting Trust and ClickFix Mechanics
Once the victim engaged with the download button, the site deployed the PasteSwitch ClickFix overlay. This tactic relies entirely on tricking the user into executing code themselves via the terminal or run dialog, successfully bypassing many standard browser-based download protections.
A Broader 48-Hour Malvertising Blitz
Further investigation utilizing OSINT tools revealed that the u/hbomax hijacking was not an isolated test run, but a massive 48-hour malvertising blitz. The threat actors squeezed as much value as possible out of the verified account’s status, pivoting quickly when domains were burned.
In total, the attackers pushed 108 distinct ads spanning multiple software lures. Beyond HBO Max, they targeted developers and power users seeking AI tools and disk cleaners.
Unveiling PasteSwitch: Cross-Platform Delivery
The HBO Max ads provided one entry into a larger delivery system. Recovered pages and payloads showed separate services for lures, visitor qualification, staging, telemetry, payload delivery, C2, and exfiltration. The name PasteSwitch describes the stable action at the center of each route: the victim pastes an attacker-supplied command, and the delivery system dynamically switches among platform, campaign, payload, and monetization branches based on visitor qualification checks.
The macOS Branch: MacSync, AMOS, and Fake Wallets
On macOS, PasteSwitch relies heavily on curl | zsh commands. The payloads included:
MacSync: Used transaction tokens ( /dynamic?txd= ) and chunked uploads to exfiltrate browser credentials, Gecko profiles, Telegram data, Apple Notes, and macOS passwords via a /tmp/osalogging.zip stage. The same execution pattern appeared in campaigns previously documented by Zscaler , Microsoft , and RST Cloud .
AMOS Helper: An execution chain utilizing xattr -c and chmod +x to run native helpers that persist under .com.apple.accountsd . The helper enrolls the victim into continuing tasking via endpoints like /api/join/ and /api/tasks/ . Similar persistence designs were independently documented by Field Effect .
Fake Wallet Applications: Deployed via routes like loop-lumen[.]com/zxc/ , these included Swift-based fake Ledger, Trezor Suite, and Exodus applications designed to directly steal 12 and 24 word BIP39 recovery phrases.
Filequanticore Reuse: Attackers also reused the copied command model across domains like filequanticore[.]com , serving a visible page advertising a DMG file while underlying JavaScript loaded the malicious copied command from a text file, successfully bypassing simple scans.
The Windows Branch: InstallFix and Amatera
If the PasteSwitch gate detected a Windows user, it dynamically delivered a different payload path utilizing mshta and PowerShell. Examples included:
InstallFix via mshta: Victims were prompted to run commands downloading an MP3/HTA polyglot. The HTA created a scheduled task, launched 32-bit PowerShell, disabled AMSI, and calculated a victim-specific subdomain based on the computer name and username.
In-Memory Loading: The subsequent stages used arithmetic fog, opaque predicates, and shellcode to inject the Amatera Stealer PE directly into memory without touching the disk.
Deceptive TLS SNI Spoofing: Once running, Amatera connected directly to an attacker IP ( 77.91.65.13:443 ) but presented .com through TLS SNI and HTTP authority. By configuring Schannel for manual credential validation ( SCH_CRED_MANUAL_CRED_VALIDATION ), the malware bypasses certificate chain checks. Basic network telemetry mistakenly logs a connection to rather than the malicious C2, completely evading standard SNI-based filtering.
The Cryptocurrency Clipper Branch: Smart Contract C2 Rotation
For persistent clipboard replacement (swapping crypto addresses when victims try to copy or paste), PasteSwitch delivered AnimateClipper and ZigClipper.
These clippers utilized Binance Smart Chain (BSC) contracts as mutable C2 dead drops. The malware queries specific smart contracts (e.g., calling getData() or balanceOf(address) ) to fetch the current active Command and Control domain (like lb.propertyfind.cc ).
Between March and July 2026, researchers observed 36 mainnet changes executed by the same attacker controller address. Because the C2 domain is hosted directly on the blockchain, the infrastructure demonstrates dynamic resilience, allowing the threat actors to easily rotate burned domains.
Read the Full Technical Breakdown
For an exhaustive deep dive into the malware staging, network infrastructure, and a complete technical teardown of the PasteSwitch operation, please read the companion report by Kirk from ADAMnetworks: HBO Max Ads Exposed: The PasteSwitch ClickFix Operation .
’s Intervention
Following community reports and an escalating volume of malicious ads, administrators successfully intervened. They paused the affected ads and launched an internal investigation alongside their Security and Safety teams to secure the verified account.
The HBO Max account provided PasteSwitch with a trusted advertising identity for 48 hours. The copied command exposed a delivery system that had already operated across software brands, operating systems, malware families, and infrastructure generations.
PasteSwitch kept its visible lures disposable while preserving operational structure. The same route grammar, API keys, helper identifiers, telemetry endpoints, staging conventions, task protocol, persistence paths, and registration patterns appeared after individual domains changed. On Windows, the operation combined InstallFix with layered in-memory loading and an Amatera client that presented .com over a direct socket to 77.91.65.13 . In the clipper branch, one controller synchronized C2 changes across testnet and mainnet contracts while two related binaries retained the same 21-address fallback configuration.
Those recurring controls provide the durable detection surface. Process ancestry exposes copied-command execution. Route tokens and API keys connect rotating macOS hosts. Destination, SNI, certificate, and DNS correlation expose deceptive TLS identity. Contract setter monitoring reveals new clipper C2 domains as they are published. Brand names and lure domains change; the systems behind them retain the signals needed to follow PasteSwitch.
Indicators of Compromise (IOCs)
The inventory below covers the directly observed routes, recovered artifacts, infrastructure, and contract state described in this article. Published MacSync and gated-ClickFix domain sets remain available through the inline Microsoft, Zscaler, RST Cloud, Cato, and lostsh references.
Additional recovered hashes
Contract-resolved C2 history
The following domains were decoded from successful setData(string) transactions against the Animate and Zig contracts. Repeated values are deduplicated.
Animate and Zig replacement addresses
Wuess replacement addresses
Proactive Defense with Hudson Rock’s Threat Feeds
With PasteSwitch and related ClickFix lures becoming increasingly sophisticated, it is vital to understand the exact mechanisms threat actors are using to deceive employees. Hudson Rock’s new ClickFix module in Cavalier provides critical visibility into malicious websites that use fake verification pages, CAPTCHA prompts, and clipboard injection techniques to trick users into executing malicious commands.
Inside Cavalier, security teams can seamlessly review detected ClickFix sites, clipboard injection and CAPTCHA indicators, injected command payloads, before and after interaction screenshots, and domain records.
Perhaps the most powerful capability of the ClickFix monitor is its integration with Infostealer credential telemetry linked to the hosting platform. By combining insights from our C2 monitoring, which now includes all data surfaced from this cross-platform PasteSwitch campaign, Cavalier pinpoints compromised employee or user credentials that enabled attackers to gain initial access to servers, explaining how legitimate domains become hosts for malware.
Crucially, all of the C2 data surfaced in this research has been added to Hudson Rock’s C2 monitoring where we track C2 data from infostealers, clickfix, and PhaaS (phishing as a service).
Protect Your Organization from Imminent Intrusions
With our new Threat Feeds, cybersecurity teams can monitor live C2 infrastructure from infostealer campaigns, ClickFix networks, and PhaaS operations to proactively block malicious communications before they cause damage.
We also provide access to various free cybercrime intelligence tools that you can find here .
Thanks for reading, Rock Hudson Rock!
Introducing Cavalier’s New Threat Feeds: Deep Dive into ClickFix Monitoring
Introducing Cavalier's New Threat Feeds: Deep Dive into ClickFix Monitoring We are thrilled to introduce three new Threat Feed modules in Cavalier: C2 Data, ClickFix, and…
ClickFix tactic: The Phantom Meet (Infostealers)
This blog post provides a chronological overview of the observed ClickFix campaigns. We further technical details a ClickFix cluster that uses fake Google Meet…
The full story
This article is one source in a clustered incident — the cluster page carries the summary, timeline and every other outlet covering it.
