 Back Redsecuretech
ILIAS Unauthenticated PHP Object Injection Leads to RCE
Here's a fun one. ILIAS has two endpoints that don't require authentication. One of them writes to your session. The other one reads your session back and...
Here's a fun one. ILIAS has two endpoints that don't require authentication. One of them writes to your session. The other one reads your session back and unserializes it without checking what it's reading. Chain them together and you get remote code execution.
That's CVE-2026-80428. DigiProSec found it and published a working exploit.
The whole thing runs as the web server user. No login required. Just two POST requests.
ILIAS versions before 9.22, 10.0 through 10.9, and 11.0 through 11.2. Fixed in 9.22, 10.10, and 11.3.
Here's a weird quirk. v11.x ships a broken shib_logout.php variant with a null $DIC, so it doesn't reach the vulnerable code as packaged. v9 and v10 are the exploitable ones in practice. But patch all three lines anyway.
First piece: ltiauth.php
This is an LTI entry point. Auth-exempt. Anyone can hit it.
When you send a request, it stores the entire request parameter array into the session table. The key is lti13_login_data. Normal enough.
But here's the catch. ILIAS has a custom session parser. If you put a \w+| marker inside a parameter value, it breaks the parser. Your raw serialized object gets handed to unserialize() as if it were a session value. That's the injection.
Second piece: shib_logout.php
This is a Shibboleth back-channel logout endpoint. Also auth-exempt.
A POST with any non-empty body starts a SoapServer. The LogoutNotification() handler then unserializes EVERY live session row in the database. No class allowlist. No type checking. Just unserialize() on whatever is there.
Since we just planted our serialized object in a session row via ltiauth.php, this handler picks it up and deserializes it.
Third piece: the gadget
The exploit uses GuzzleHttp\Cookie\FileCookieJar. That class is bundled in ILIAS's vendor tree. It has a __destruct() method that calls save($this->filename). And save() calls file_put_contents($filename, json_encode($cookies)).
So the attacker controls two things. The filename. And the content. The content is JSON that embeds PHP code. When the object gets destroyed at the end of the request, it writes the file.
DigiProSec published a Python script. It does four things:
Seeds the session via ltiauth.php with a crafted serialized object
Triggers unserialize via shib_logout.php with a SOAP envelope
Checks if the webshell is live
Runs commands through it
Usage looks like this:
You can also drop into an interactive loop with --shell.
Two things you need to know. The docroot disk path is required for the file write. It defaults to /var/www/ilias/public. And if ILIAS is configured with a fixed HTTP path, you need to send the right Host header with --host-header.
Unauthenticated RCE is as bad as it gets. The webshell runs as the web server user. Apache or PHP-FPM, depending on your setup. That's usually enough to read config files, hit the database, and move laterally.
The chain also shows how two endpoints that are individually "fine" can become dangerous when chained. ltiauth.php was just storing session data. shib_logout.php was just deserializing sessions. Together they're a weapon.
Patch. Update to 9.22, 10.10, or 11.3. Check which line you're on.
Check for webshells. Look for unexpected .php files in your web root. The exploit writes files with names like util_xxxxxx.php.
Check your logs. Pay special attention to any POSTs to /ltiauth.php and /shib_logout.php that seem suspicious.
Restrict auth-exempt endpoints. Unless you are using LTI or Shibboleth, it may be a good idea to restrict these endpoints completely.
Assume compromise if you see suspicious files. Rotate credentials. Check for persistence. Consider rebuilding.
CVE-2026-80428 is an unauthenticated RCE in ILIAS. Two auth-exempt endpoints. One unserialize with no allowlist. One Guzzle gadget. That's all it takes.
Patch to 9.22, 10.10, or 11.3.
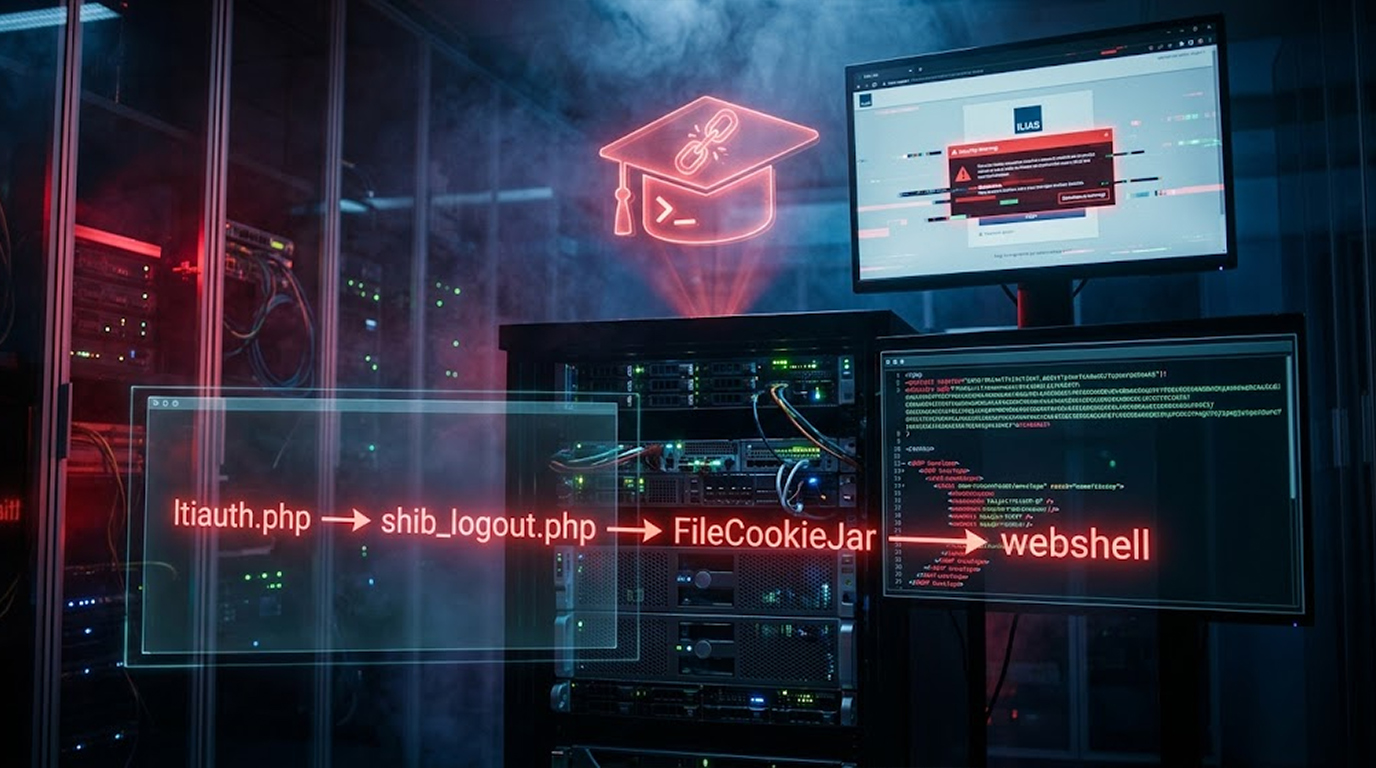
Unauthenticated PHP object injection → RCE
< 9.22, 10.0 to 10.9, 11.0 to 11.2
ltiauth.php → shib_logout.php → FileCookieJar
Webshell as web server user
What is CVE-2026-80428?
An unauthenticated PHP object injection in ILIAS. Two auth-exempt endpoints let an attacker plant a serialized object and trigger unserialize on it. The gadget drops a webshell.
How does the chain work?
ltiauth.php stores attacker-controlled session data. shib_logout.php unserializes it without an allowlist. The FileCookieJar gadget writes a PHP file to disk.
Which versions are affected?
ILIAS before 9.22, 10.0 through 10.9, and 11.0 through 11.2.
Not as packaged. v11.x ships a broken shib_logout.php with a null $DIC. v9 and v10 are exploitable.
Patch to 9.22, 10.10, or 11.3. Check for webshells. Review logs. Lock down auth-exempt endpoints if you don't use them.
The full story
This article is one source in a clustered incident — the cluster page carries the summary, timeline and every other outlet covering it.
