 Back Therecord.Media
Iranian cyber spies used fake MRI scan results to hack 'enemy of regime'
British, American and Dutch security agencies issued a warning on Tuesday exposing a spyware tool being used by Iranian state- hackers to target individuals perceived as posing a threat to the regime.
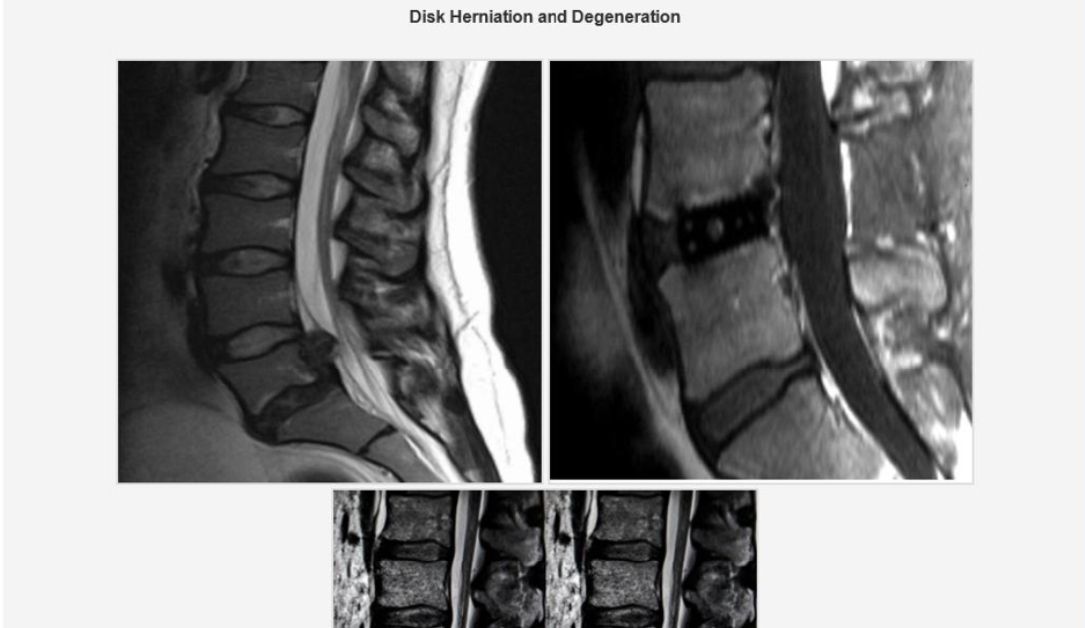
The malware, named CHOSEN BRICK by British intelligence, has been delivered using a range of lures — including a fake MRI scan of a disk herniation — sent to victims after extensive social engineering campaigns to earn their trust.
According to the United Kingdom’s National Cyber Security Centre (NCSC), Iran has used this and similar cyber activity to “support the repression of individuals who are seen as a threat to the regime, such as dissidents, activists and journalists.”
The agency warned that in some cases the Iranian intelligence services have plotted to kidnap and assassinate individuals, including internationally, who are perceived as enemies of the regime.
CHOSEN BRICK enables the attackers to harvest a wide range of material from targeted devices, including contacts, email inboxes and social media messages. It also allows the hackers to capture screen content and to switch on the device’s microphone.
The agencies warn this provides data that can be used to create a pattern of life — a map of the victim's location, contacts and daily routine that increases the physical risk to those affected. The advisory says personal details stolen this way have surfaced on pro-Iranian leak sites to further harass the victims.
The alert was issued jointly by the NCSC, the FBI in the United States, and the Netherlands’ General Intelligence and Security Service (AIVD). It covers victims in all three countries dating back to at least 2025.
The operators behind the campaign have been observed tailoring their approach to each individual target, the agencies said, resulting in a wide variation in how the compromise begins.
However, the alert said there was a core pattern to the attack chain, with the operators making initial over messaging platforms such as WhatsApp and Telegram — often posing as a known or as technical support — and building rapport before delivering a malicious file.
These files are disguised to match the pretext. Alongside the MRI scan, the attackers have impersonated legitimate products including Pictory, RunwayML, Norton Antivirus, Telegram, Adobe Flash Player and KeePass.
The CHOSEN BRICK malware itself only works on Windows systems and is designed to survive devices being rebooted by relaunching at login. It also adds exclusions to Microsoft Defender to reduce the chance of it being detected.
Once installed, the malware uses Telegram for its command and control. Each victim is assigned a separate Telegram bot, limiting the risk that one compromised device exposes others. Stolen files are also sent through Telegram alongside other commercial cloud-storage services. The alert said the most recent versions of the spyware uses proxies to conceal its traffic.
The NCSC also warned that attackers may try to move targets onto personal devices to bypass workplace security. It urged organizations with at-risk staff to the warning and help employees check their own phones and computers.
Although the NCSC did not identify a specific Iranian government entity behind the campaign, the tradecraft closely matches activity the FBI attributed in a flash warning circulated in March, which blamed actors operating "on behalf of the Government of Iran Ministry of Intelligence and Security" (MOIS).
The FBI said similar Telegram-based malware had targeted Iranian dissidents and journalists since fall 2023. It linked a July 2025 hack-and-leak operation to “Handala Hack,” an online persona the bureau assesses is operated by MOIS and connected to another group, “Homeland Justice.”
Also in March, the U.S. State Department reissued a $10 million reward for information on hackers connected to Iranian cyber actors following the compromise of a personal email account belonging to FBI director Kash Patel. The same month, the FBI seized a number of leak sites tied to the MOIS used to host information stolen from various victims.
Although primarily a cybersecurity warning, the threat posed by Iranian surveillance extends to real-world physical attacks.
In October 2025, MI5 Director-General Ken McCallum said British security services had tracked more than 20 potentially lethal Iran-backed plots during the year, including threats against journalists and opponents of the Iranian government.
The full story
This article is one source in a clustered incident — the cluster page carries the summary, timeline and every other outlet covering it.
