 Back Finance.Biggo
North Korea Deploys Third-Country IT Workers to Breach US Firms, NBC Reports
North Korea has shifted its infiltration strategy to leverage remote IT workers based in third countries such as Iran and Lebanon, using them as a bridge to place operatives inside American companies and funnel money toward weapons development, according to an NBC News investigation published Friday.
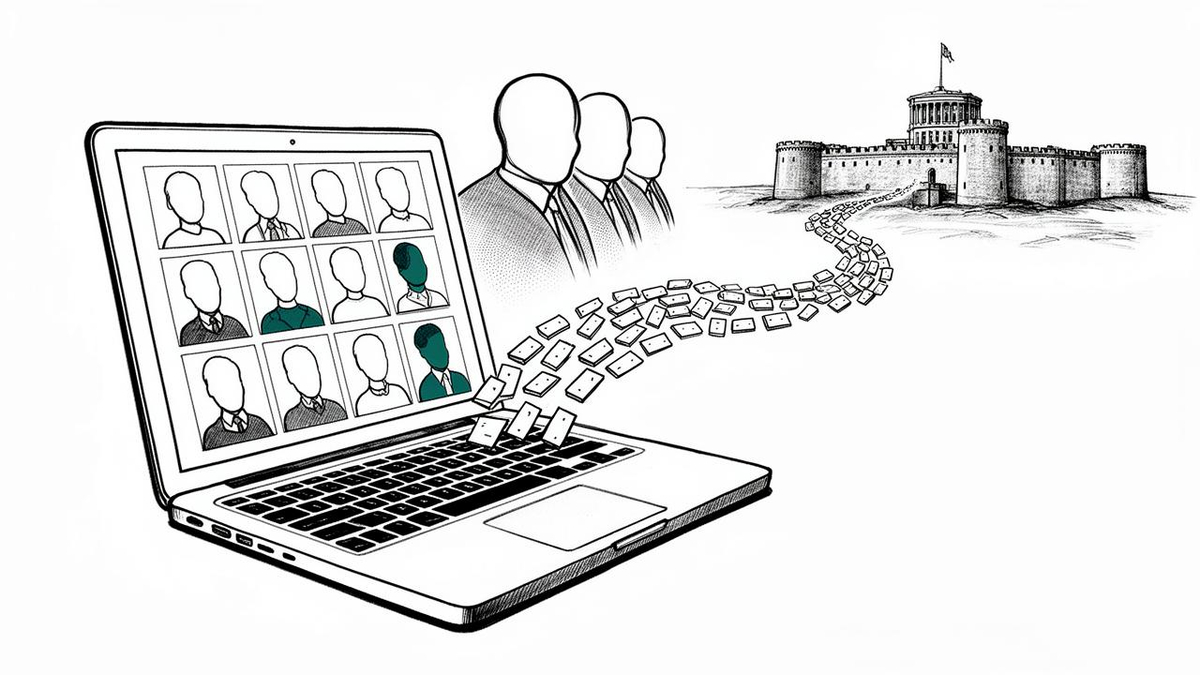
The scheme represents an evolution in Pyongyang's long-running campaign to exploit the global tech labor market. Rather than having North Korean nationals apply directly for remote jobs, the regime now recruits foreign freelancers to pass hiring processes and secure contracts, then hands those credentials and system access to DPRK operatives once the roles are established.
The tactic, outlined in a July advisory from the US government and allied agencies, frames North Korean IT workers as contract-seekers who intend to remit salaries to state agencies while simultaneously posing insider threats through data exfiltration, cryptocurrency theft, and theft of sensitive information.
How the recruitment pipeline works
The workflow described by NBC is deceptively simple. Third-country IT professionals are scouted through mainstream platforms, including , and hired to serve as "interview associates" — individuals who can convincingly navigate technical interviews and onboarding processes. Some were reportedly offered $500 per month in cryptocurrency for part-time involvement.
Once a contract is secured and the worker has established legitimate access to company systems, the position is "usually" taken over by North Korean operatives, the report said. The handover gives Pyongyang-linked actors a foothold that appears normal from an outside hiring perspective, complete with valid credentials and internal knowledge.
The use of cryptocurrency in the recruitment workflow serves a dual purpose. It allows payments to blend into existing freelance structures while remaining harder to trace than conventional payroll, and it aligns with the broader financial ecosystem that North Korean actors have exploited for years.
A pattern of escalating cyber operations
The labor infiltration angle fits into a larger picture of DPRK-linked cyber activity that has intensified despite international sanctions. In May, Cointelegraph reported — citing cybersecurity firm CrowdStrike — that North Korean state-affiliated hackers were responsible for more than $2 billion in cryptocurrency losses in 2025, a 51% year-on-year increase.
That figure reflects the breadth of theft operations, but the throughline is consistent: cryptocurrency functions as both a tool for recruitment and an outcome for DPRK-linked financial diversion. The operational model may be bearing fruit, as the scale of losses suggests sophisticated coordination across multiple vectors.
Earlier this year, blockchain development firm Consensys disclosed that it had unknowingly outsourced developer work to a North Korean operative, underscoring how difficult these schemes are to detect even for technically sophisticated organizations.
The Bank of Korea estimated that North Korea's GDP grew 3.5% in 2025 despite global restrictions, a reminder that alternative channels — including cybercrime and illicit financial routing — can sustain the regime's operations without trade normalization.
What this means for corporate defenses
For companies processing remote hires, the implications extend beyond traditional perimeter security. Organizations that rely on remote onboarding, contractor access, or permissive internal tooling could be inadvertently enabling a pathway for identity compromise, unauthorized code handling, and lateral movement once a handover occurs.
Security teams should assume that "legitimate" employment pathways can conceal hostile intent, the report concluded. The core concern is that hiring risk is now inseparable from security risk, and that purely technical defenses may be bypassed by schemes that begin at the recruitment stage.
As governments and companies tighten controls around known malware and exchange-related abuse, recruitment-based infiltration may become more attractive precisely because it exploits the human layer of corporate defense.
What to watch is whether enforcement agencies and advisories provide granular indicators — such as specific behaviors during remote hiring, payment patterns, or contract-approval structures — that organizations can use for earlier screening. In the meantime, the message is clear: the threat model includes both access and monetization, and the entry point may be a seemingly qualified contractor who never actually does the work.
Once added, BigGo Finance appears first in Google Top Stories, so you get the broadest, most up-to-the-minute, and most comprehensive global financial news first.
The full story
This article is one source in a clustered incident — the cluster page carries the summary, timeline and every other outlet covering it.
