 Back Internazionale.It
Ransomware group says it stole Berlin data, offers it for auction
BERLIN, Aug 28 (Reuters) - A ransomware group said on Friday it was putting up for auction a trove of data it stole from Berlin state agencies, and city officials refused to pay.
The Rhysida group, which researchers say operates from Russia or Eastern Europe, said on its website it took 5.79 terabytes of data including 46,500 contracts as well as emails, phone numbers, passwords and classified information.
The group said it was auctioning the data at a starting price of 30 bitcoin ($77,622) in just under seven days, showing a countdown timer on its website.
The cyberattack on Berlin’s network comes less than a month before the city-state holds elections on September 20.
‘BERLIN WILL NOT SUBMIT TO EXTORTION’
Broadcaster RBB reported on Thursday evening that Berlin had received ransom demands for an unspecified amount following the attack.
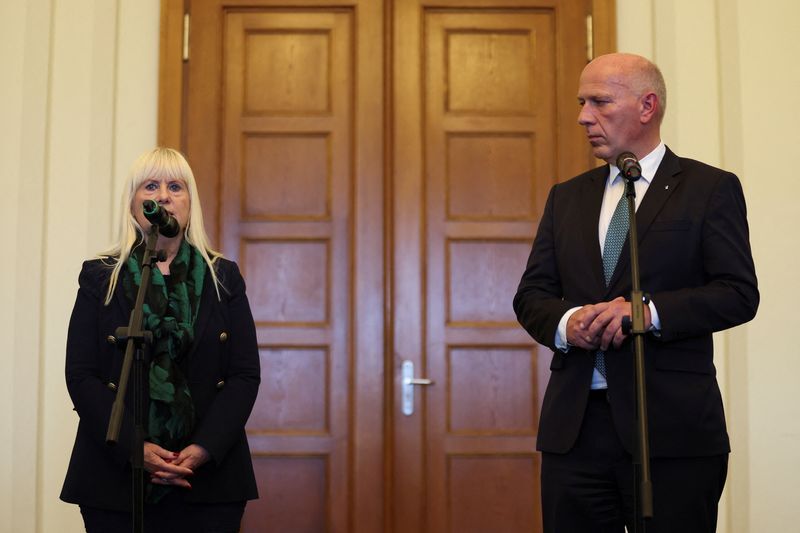
“The state of Berlin will not submit to extortion,” Berlin Mayor Kai Wegner and Berlin’s interior senator, Iris Spranger, said in a joint statement on Friday, before the ransomware group claimed the attack on their website.
Officials could not provide details on the content or scope of the affected data because the extent of the breach was still being examined, Wegner said at a press conference.
Spranger said the city’s election infrastructure had not been affected and that, according to security officials, no data related to the election had been compromised.
RANSOMWARE GROUP TARGETS GOVERNMENTS
Rhysida has claimed nearly 280 attacks since it emerged in June 2023, according to cybercrime research platform eCrime.ch.
Roughly half of its victims have been in the U.S., followed by the U.K., Canada and Italy, as well as other nations, according to Ransom-DB, a ransomware analysis and tracking service.
The group has repeatedly targeted government institutions, such as the October 2023 hack of the British Library. The group has also claimed attacks on the Chilean army, schools, healthcare facilities and businesses of all sizes.
(Reporting by Cian Muenster, Miranda Murray, Maria Martinez;Editing by Friederike Heine and Cynthia Osterman)
Di Maria Martinez e AJ Vicens
BERLINO, 28 agosto (Reuters) - Un gruppo di hacker specializzato in ransomware ha dichiarato venerdì di aver messo all’asta una grande quantità di dati sottratti alle agenzie statali di Berlino, mentre i funzionari della città si sono rifiutati di pagare.
Il gruppo Rhysida, che secondo i ricercatori opera dalla Russia o dall’Europa orientale, ha dichiarato sul proprio sito web di aver sottratto 5,79 terabyte di dati, tra cui 46.500 contratti, oltre a e-mail, numeri di telefono, password e informazioni riservate.
Il gruppo ha dichiarato che metterà all’asta i dati a un prezzo di partenza di 30 bitcoin (77.622 dollari) tra poco meno di sette giorni, mostrando un conto alla rovescia sul proprio sito web.
L’attacco informatico alla rete di Berlino arriva a meno di un mese dalle elezioni che si terranno nella città-Stato il 20 settembre.
«BERLINO NON SI SOTMETTERÀ AL RICATTO»
L’emittente RBB ha riferito giovedì sera che Berlino aveva ricevuto richieste di riscatto per un importo non specificato a seguito dell’attacco.
«Lo Stato di Berlino non cederà alle estorsioni», hanno dichiarato venerdì in un comunicato congiunto il sindaco di Berlino Kai Wegner e la senatrice agli Interni Iris Spranger, prima che il gruppo di ransomware rivendicasse l’attacco sul proprio sito web.
I funzionari non hanno potuto fornire dettagli sul contenuto o sulla portata dei dati interessati poiché l’entità della violazione era ancora oggetto di analisi, ha dichiarato Wegner in una conferenza stampa.
Spranger ha affermato che l’infrastruttura elettorale della città non è stata compromessa e che, secondo i funzionari della sicurezza, nessun dato relativo alle elezioni è stato compromesso.
GRUPPO DI RANSOMWARE PRENDE DI MIRA I GOVERNI
Rhysida ha rivendicato quasi 280 attacchi da quando è emerso nel giugno 2023, secondo la piattaforma di ricerca sul crimine informatico eCrime.ch.
Circa la metà delle sue vittime si trova negli Stati Uniti, seguiti da Regno Unito, Canada e Italia, oltre ad altre nazioni, secondo Ransom-DB, un servizio di analisi e monitoraggio del ransomware.
Il gruppo ha ripetutamente preso di mira istituzioni governative, come nel caso dell’attacco hacker dell’ottobre 2023 alla British Library. Il gruppo ha inoltre rivendicato attacchi contro l’esercito cileno, scuole, strutture sanitarie e aziende di ogni dimensione.
(Reporter Cian Muenster, Miranda Murray, Maria Martinez; editor Friederike Heine e Cynthia Osterman)
Scrivici per correzioni o suggerimenti: [email protected]
The full story
This article is one source in a clustered incident — the cluster page carries the summary, timeline and every other outlet covering it.
