 Back Crypto-Economy
Revolut Discloses Two Customer Data Breaches After Social Engineering Attack
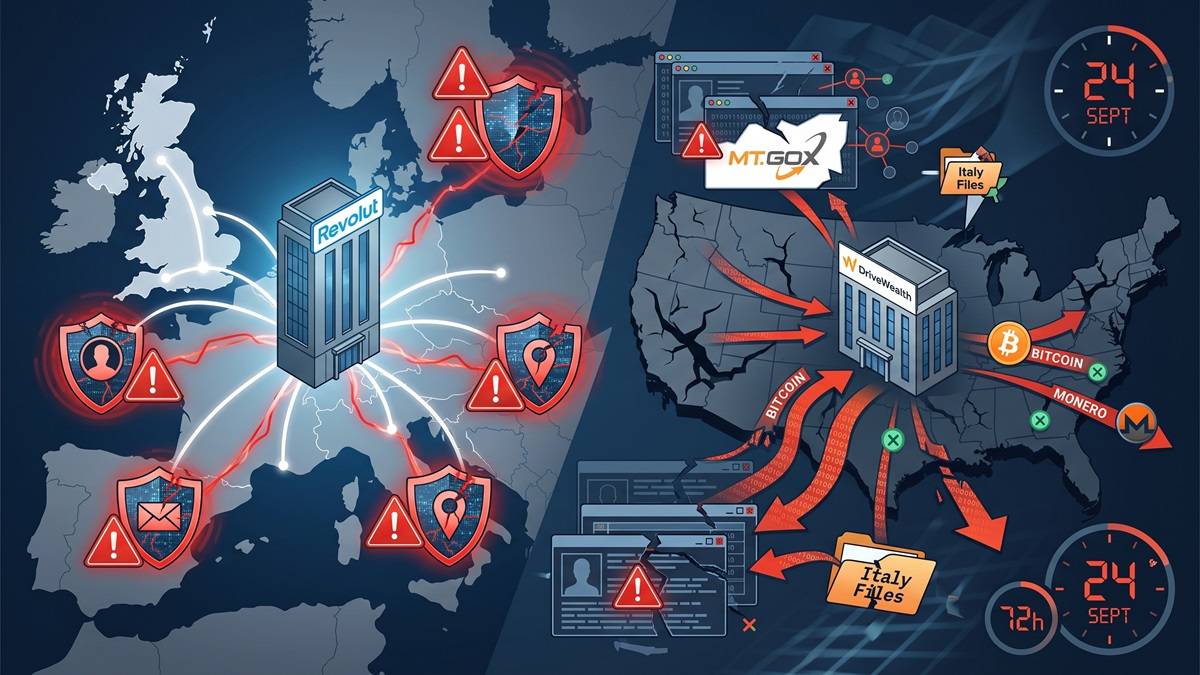
DriveWealth , Revolut’s former US broker, suffered a social engineering attack on September 4–5 that compromised customer profile records.
The attacker initially demanded up to $760 million in Bitcoin before lowering the demand to $3 million in Monero and leaking files linked to 680 crypto investor accounts .
The financial institution confirmed that its funds, accounts, and core infrastructure suffered no operational disruptions during the reported incidents.
British digital bank Revolut and its former US brokerage partner DriveWealth confirmed on Thursday, September 24, two customer data breaches that occurred during the current month.
JUST IN: Revolut is emailing customers another data incident. This one is at DriveWealth, the US broker that used to handle Revolut’s US trading. DriveWealth says unauthorised access hit its systems on 4–5 September. The data taken is older customer-profile… pic.twitter.com/xPO7YbOk57 — Max Karpis (@maxkarpis) September 24, 2026
JUST IN: Revolut is emailing customers another data incident. This one is at DriveWealth, the US broker that used to handle Revolut’s US trading.
DriveWealth says unauthorised access hit its systems on 4–5 September. The data taken is older customer-profile… pic.twitter.com/xPO7YbOk57
— Max Karpis (@maxkarpis) September 24, 2026
The incident in DriveWealth’s systems took place between September 4 and 5 . The attackers gained unauthorized access to information including names, email addresses, ages, gender, nationality, mailing addresses, and employment details.
DriveWealth previously handled US stock trading operations for the British platform’s users. The information stolen in this event comprises historical profiles and does not include records of European Economic Area users after 2023.
Both companies sent formal notifications to affected users throughout the day on September 24 . Neither corporation disclosed the exact number of exposed individuals nor the technical methods used by the attackers in the initial intrusion.
The fintech company emphasized via a statement that its funds , account balances, and internal infrastructure remain intact . The event is categorized as a breach of profile data privacy and not as a financial loss of custodied assets.
Official Email Attack and the “Italy Files” Leak
This represents the second security failure disclosed by the company in recent weeks. In early September, the entity admitted that cybercriminals used a legitimate email account belonging to the Italian government to bypass internal controls and extract confidential information.
The attacker made fluctuating financial demands to halt the exposure of the information. The initial request reached approximately $760 million in Bitcoin , an amount that was later reduced to $3 million in Monero .
After the entity refused to pay the ransom, the attacker leaked a batch of records dubbed the “Italy Files” . The published documentation includes information corresponding to 680 large cryptocurrency holders .
Among the public figures impacted by the disclosure is Mark Karpelès , former CEO of the Mt. Gox exchange. According to a market report, the hacker began offering this data at discounts of up to ten times the original demand, suggesting difficulties with monetization on the black market .
British and European regulatory compliance protocols require notifying data protection supervisory authorities within 72 hours of confirming a breach. The banking entity maintains open personalized assistance channels while submitting corresponding reports to financial agencies and law enforcement bodies leading the investigation.
Financial Times Reports Revolut Hackers Cut Ransom to $3M With 24-Hour Deadline
TL;DR: The amount demanded by the attackers totals 6,000 Monero (XMR) tokens, equivalent to approximately $3 million as of September 16, 2026. The security incident
Italy Launches Inquiry Into Email Hack Allegedly Used to Steal Revolut Data
TL;DR: Italy have opened a criminal investigation after a hack on government email accounts was used to obtain sensitive data from Revolut customers. The Polizia
Revolut Attackers Leak Selfies and IDs as Ransom Demand Escalates
TL;DR: Attackers began publishing Revolut customer selfies and identity documents, threatening daily releases until the fintech pays, while exposed data may also include account statements
Revolut Wins Conditional OCC Approval for U.S. Bank Charter
The U.S. Office of the Comptroller of the Currency (OCC) granted conditional approval to the global neobank Revolut to establish a national bank. The confirmation,
Revolut Begins Rolling Out EURR Stablecoin to Select EU Customers
Revolut said August 26 that it began a phased rollout of EURR, its first euro-backed stablecoin, to selected eligible customers in Denmark, Poland and Portugal.
Zama Debuts Token Trading on Revolut Across the EEA
TL;DR ZAMA is now available on Revolut across the EEA, giving Zama access to more than 70 million customers, including over 15 million crypto traders.
The full story
This article is one source in a clustered incident — the cluster page carries the summary, timeline and every other outlet covering it.
