 Back Infostealers
Revolut Hackers Used Infostealers for Elaborate Social Engineering
BREAKING: The investigations team at Duel has established with the hacker behind the recent Revolut incident, revealing alarming new details the methods used to compromise the financial institution.
The Anatomy of the Attack
According to the information gathered, the attack was a sophisticated blend of technical compromise and social engineering:
Initial Access via Infostealers: The hacker gained access to government employee accounts using an infostealer. After gaining entry to an employee’s email, they would log in, add a recovery email under their control, begin logging activities, and silently monitor communications.
Evading Detection: To avoid raising suspicion, the hacker instantly deleted any outgoing emails they sent that were not intended for the original employee. They monitored the inbox 24/7 for responses. Upon receiving a to their fraudulent emails, they would immediately download it as a .eml file and delete it before the actual account owner noticed.
Targeting the Right Entity: The hacker admitted that while they initially tried forging court orders (a tactic presumably used against other companies), they quickly realized this wouldn’t succeed with Revolut. After conducting research, they determined the optimal target was Revolut’s Lithuania-based subsidiary, Revolut Bank UAB, which is obligated to respond to a European Investigation Order.
The Initial Breach: Using a compromised email account, the hacker sent a single, fraudulent request approximately five months ago. Revolut, believing the communication originated from the Italian government, complied with the fabricated order.
Sustained Control: From the compromised inbox, the hacker managed and terminated email threads that appeared to genuinely originate from multiple Italian government addresses.
A Five-Month Campaign: The hacker continuously sent requests over a five-month period. Astonishingly, Revolut reportedly never questioned the requests or withheld information. In one instance, when the hacker accidentally sent an incorrect document, Revolut’s support team allegedly guided them on how to correct it rather than detecting the fraud.
Correspondence demonstrating the hacker utilizing an Italian government email address to communicate with Revolut’s legal department.
“We remain in with the hacker and we’ve requested exclusivity of information related to the story to be kept with Duel. We believe it is in the public’s best interest for EVERY piece of information related to this to be released, so that the extent of Revolut’s failure can be brought to light, as well as the sheer stupidity of the manner in which the KYC paradigm is currently conducted.”
“The Duel team hopes that Revolut will be held accountable for their lack of due diligence and betraying their customers in such a severe manner, especially given the breadth and depth of the breach. Lives are now at risk. I’m personal friends with one of the victims, and he’ll probably have to move houses due to the continued (credible) kidnap threats.”
– The Duel Investigations Team
Hudson Rock’s Analysis & Intelligence
New Insight from Hudson Rock
While the Revolut hackers claimed they used Infostealers (initially telling researchers they used a ‘RAT’) to actively infect Italian government employees, Hudson Rock’s intelligence suggests a different scenario.
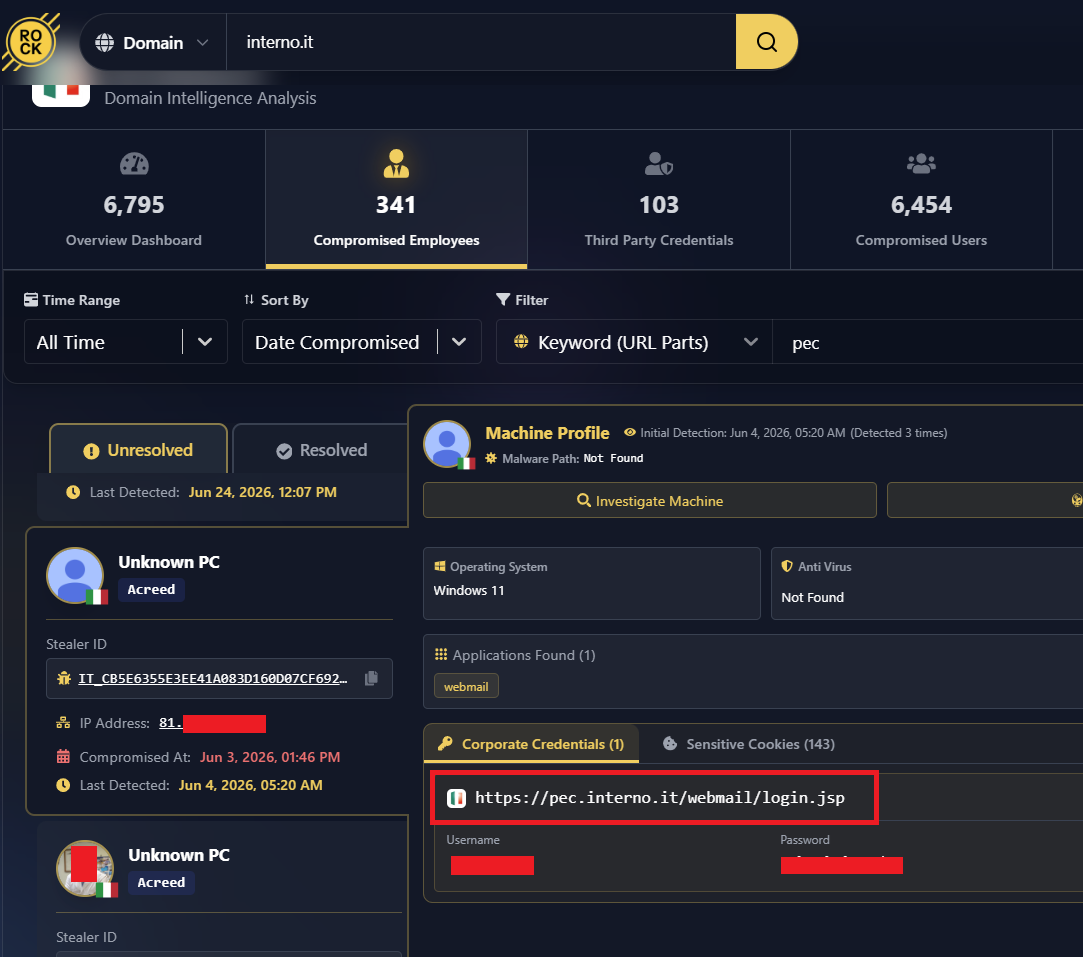
Images from the campaign clearly show correspondence with Revolut was conducted using ‘pec.interno.it’ email addresses, which belong to the Italian Ministry of the Interior.
Hudson Rock’s Cybercrime Intelligence database revealing numerous compromised credentials for the ‘interno.it’ domain, providing an easy avenue for the attackers.
Protect Your Organization
We also provide access to various free cybercrime intelligence tools that you can find here:
Thanks for reading, Rock Hudson Rock!
HBO Max ads on a compromised account exposed a massive PasteSwitch ClickFix operation
HBO Max ads on a compromised account exposed a massive PasteSwitch ClickFix operation HBO Max ads on a compromised account exposed a massive PasteSwitch…
Inside a Syrian Interrogation Room: The Detainee Files an Infostealer Stole From a Military Police Unit
A single malware infection on one senior officer’s computer exposed the active caseload of a Syrian National Army military police unit
Analyzing Stripe Vendors Breach: Confirmed Vendor Exposure and Claims of 20,000 Compromised APIs
Stripe Data Breach: Analysis of Satanic's Release Analyzing Stripe Vendors Breach: Confirmed Vendor Exposure and Claims of 20,000 Compromised APIs On August 18th, 2026, a data…
The full story
This article is one source in a clustered incident — the cluster page carries the summary, timeline and every other outlet covering it.
