Shopify shops with “ HulkApps ”, “ Swym Wishlist Plus “ or “ Selleasy “ installed have could been phishing their own customers
Malicious Javascript Code is being executed on customer’s browsers
The code is not delivered by the apps directly but through the app developer’s APIs
The code redirects users to fake checkout pages, steals credit cards and user data
Origin of the malicious code unclear (HulkApps merchant accounts / employee accounts / HulkApps themselves / ???)
The malicious URLs are still not blocked by Google/Abuse.ch ( please report them! )
checkout-confirm(.)top
Infected Shopify Apps
As of Oct 16th, all affected apps have been fixed or de-listed from the App Store.
[ de-listed ] HulkApps / Hulk Product Options (see below, another source )
[ de-listed ] Swym Wishlist Plus ( source )
[ de-listed ] Selleasy ( source )
[resolved] Hextom (in August, source , source )
[resolved] Qikify (in July, source , source , incident report )
Actions as Shop Owner
Disable as much Shopify Apps as possible (especially the ones mentioned above)
Open an incognito browser window and check if you are getting redirected to the real checkout page (place item in cart → press “checkout”)
Shopify immediately when you spot a fake checkout
Change your Shopify password
Change your Shopify app account’s password (eg. on HulkApps, Swym, Selleasy)
Check which (AI) tools have access to your Shopify account
It looks like this is bigger than it seemed. five six seven merchants now contacted me and stated they suffered from the same hijack. But HulkApps wasn’t installed in all of those shops - which means at minimum 1 other Shopify app is acting malicious. If you have seen this is Hijack in a Shopify shop after Oct 11 please me !
Dan S. on reported that the same attack happens over the Swym Wishlisht Plus App!
Within 16 minutes of Shopify escalating the issue internally, the checkout Hijack on mechanicalkeyboards.com is gone. It looks like they removed the HulkApps integration.
Today I was shopping on mechanicalkeyboards.com and found a keyboard I really liked. But since I was located in Germany I wanted to see the shipping costs to determine if I should look on other websites.
So I have put the keyboard in my cart and pressed “Checkout”.
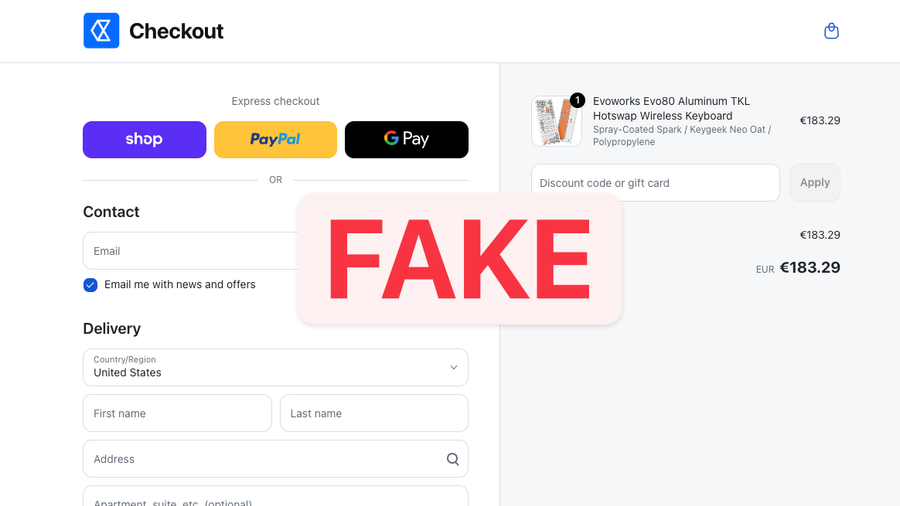
Yep, looks like a Shopify checkout page. At first I was a bit confused the Shop logo but it’s not the first time that those ones don’t match when the shop owner hasn’t configured it correctly. ( After writing the post, I noticed that it looks awfully close to another horrendous company: Polymarket )
When clicking the “First name” field, I was then offered 1Password auto complete - but not for my first name but my Credit Card’s first name which was very suspicious.
This made me look at the actual URL:
That was obviously a phishing attempt. I did some searching around a found a post from 18 days (!!) from a Vaping shop owner that reported the same issue with the same domain and said they contacted Shopify.
Allegedly reported over 2 weeks ago but mechanicalkeyboards.com had the same attack live?
I wanted to find out, where this came from. Since neither any script or the website itself was blocked by multiple layers of AdBlock browser extensions or DNS malware filtering.
So starting at the checkout drawer, i inspected the “Checkout” buttons listeners with the Chrome DevTools - but nothing. Knowing that many scripts just add a listener on the window or document elements, I continued on.
Chrome allows developers to add breakpoints to event listeners such as click so execution stops immediately before an attached event listener is being executed.
Many scripts add event listeners to click s, so skipping through every breakpoint I finally found this gem:
“hijack” doesn’t sound that trustworthy. So where does it come from? No idea. It had no source file attached (named VM142 by Chrome) so it must have been injected at runtime (like writing a with Javascript).
So the new task was to find where the injected script comes from.
Fortunately, Chrome also provides an event listener breakpoint for “ Script First Statement ” - the point where any individual script is being started to execute. Those are a lot . But to my advantage, breakpoints persist page reloads and can also be scripted.
This snippet below overrides the default addEventListener function and looks for the word “hijack” as callback function - which we identified shortly before.
And there we have it:
A hulkcode.js can be traced up the call stack to be the origin of our injected script.
This extension gets delivered right from the Shopify CDN and is apparently authored by Hulkapps .
Looks like a development company tailored all around Shopify apps/extensions.
But I still needed to find out why the malicious script was injected. Maybe Hulkapps itself got compromised or a configuration error allowed for the injected of inline Javascript.
While monitoring XHR requests, hulkcode.js ever only sends one POST request on page load to
This contains the store id and information the currently viewed product as payload. Notably, the response includes a advanced_users.custom_js key with 22.7 Kilobytes of Javascript - oh no no no.
JSON-decoding this script gives us a beautiful un-minified un-obfuscated script.
The full script is available here as Github Gist .
Some Chinese, love to see good code documentation.
And here again is our beloved hijack function.
Note the firstCheckoutDetectedAt : The script only ever activates once per shop and then stores a __ctf_shim_handoff_done_v1 in the session storage on the Shopify shop to indicate that a user has already been redirected to the phishing site and should not be re-attempted.
The other __ctf_checkout_txn_v1 entry is unknown to me. Possibly a session ID to match the selected product.
A redirect function leading us to the phishing site:
At the end of the script, there’s the configuration with a couple of domains
checkout-confirm(.)top
Notably, none of those domains are listed on URLhaus (see here , here and here ) or Google Safe Browsing.
One last thing to try out is to get phished. I started a new private browsing session, went to the checkout and entered my information - which were as real as the checkout page itself.
After submitting, a POST request is sent to with all of my data and I get a lovely response back shortly before being redirected to the correct checkout. (hey, no duplicate, awesome!)
If you’re interested, the phishing site is hosted on AS54801 ( IPinfo ).
HulkApps provides Shopify shops with merchant tools
Shopify shop owners can install those extensions and apparently configure “custom Javascript” in their HulkApps account
This custom Javascript is being sent to every shop on page load and is getting executed
In this case, a hijack script redirected customers on checkout to fake phishing pages
It’s unclear to me, how this malicious script found it’s way in HulkApps infrastructure. Some possible ways:
The HulkApps account of the shop owner got compromised
A HulkApps employee’s account got compromised
HulkApps itself got compromised
Another malicious Shopify app in the background modified the Hulkapps configuration
Also it is unclear how many Shops are compromised. Until right now, I know of two but the script itself is very generic and looks like it adapts to all Shopify shops.
Is your shop compromised?
Using infected apps or extensions, as mentioned at the top?
No: probably not compromised
Try triggering a phishing attempt:
Open a fresh Browser window in incognito
Place any item in the cart
Are you getting redirected to the real checkout page?
I would advice to change your HulkApps password/2FA although it is currently unclear how the malicious script got into the HulkApps configuration.
I am publishing this blog post to alert Shopify merchants that their store may be compromised if they are using HulkApps products.
2026-10-10 12:10 Phishing attempt discovered
2026-10-10 12:24 Contacted Mechanical Keybords via E-Mail
2026-10-10 14:32 Contacted HulkApps via E-Mail
2026-10-10 14:46 Reported domains to URLhaus and Google Safe Browsing
2026-10-10 15:27 with Shopify initiated
2026-10-10 16:18 Incident reported to BSI CERT
2026-10-10 16:21 Shopify has escalated the incident internally
2026-10-10 16:37 Shopify has fixed the Checkout Hijack on mechanicalkeyboards.com. They couldn't give me an answer how many other shops were impacted and if they took action on behalf of other shops
2026-10-10 18:46 mechanicalkeyboards.com confirmed that the app was immediately removed after they were notified of it and are in with Shopify
2026-10-15 09:58 It looks like some of the domains are now listed on Spamhaus.org and should be blocked on several DNS resolvers
The full story
This article is one source in a clustered incident — the cluster page carries the summary, timeline and every other outlet covering it.
