 Back Straitstimes
Singapore refreshes cyber strategy with new national tool to block malware and phishing sites
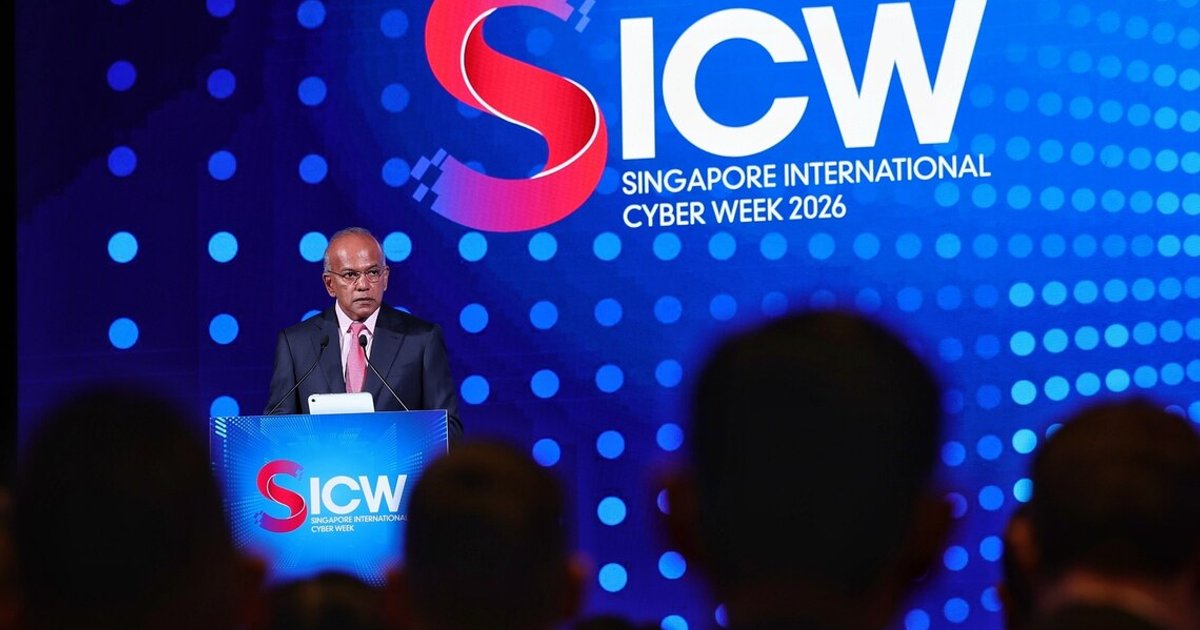
Senior Minister K. Shanmugam, who is also Coordinating Minister for National Security and Affairs Minister, delivering the opening address at the Singapore International Cyber Week 2026 on Oct 13.
Singapore has launched a protective domain name service to block access to known malware and phishing sites as part of a new cybersecurity strategy.
The service, run by CSA under the Online Criminal Harms Act, will use checks and appeals to reduce false blocks and protect users, businesses and critical systems.
Singapore is also boosting cyber defences with AI tools, quantum-safe migration, and stronger international cooperation as malware and attacks rise.
SINGAPORE – A new national service will soon block Singapore users from accessing known phishing and malware sites amid a sharp rise in the number of infected computer systems here .
Called a protective domain name service (PDNS), it was announced on Oct 13 by Senior Minister K. Shanmugam as part of Singapore’s refreshed cybersecurity strategy to counter heightened cyberthreats .
The shift is toward a proactive, AI-driven national defence model as threat actors have become faster and more sophisticated thanks to artificial intelligence.
“Singapore will seek to act earlier, act at national scale and act at the speed of the threat. This shift is an important part of Singapore’s cybersecurity strategy 2026 which we are launching today,” said Shanmugam, Coordinating Minister for National Security and Minister for Affairs.
He was speaking at the opening of the 11th Singapore International Cyber Week at the Marina Bay Sands Expo and Convention Centre.
Shanmugam said Singapore’s updated cybersecurity strategy is broader than how national cyberdefence has been built so far.
“It will cover how we will strengthen our critical infrastructure in the wider cyberspace, build capabilities for AI and quantum, deepen our global partnerships, and invest in our cybersecurity ecosystem and workforce,” he said.
Expected to be rolled out in 2027, the new PDNS will be operated by the Cyber Security Agency of Singapore’s (CSA) National Cybersecurity Command Centre, under the Online Criminal Harms Act.
The Act, which came into force in 2024 , allows the authorities to ask individuals, companies and internet service providers to remove or block access to content that they suspect is being used to commit crimes, such as illegal gambling and money lending, drug-related offences, scams, and malicious cyberactivitie s.
CSA said that the new service will have safeguards to “ensure the responsible exercise” of powers under the Online Criminal Harms Act.
The agency said that a “robust assessment and validation process” will be carried out before malicious websites are blocked, to reduce the risk of false positives and to ensure site blocking decisions can be accounted for.
Individuals or organisations affected by the service’s website blocking can seek recourse through the Act’s existing reconsideration and appeal processes.
Similar malicious-website blocking services have been implemented in Australia, Canada, the European Union, the United Kingdom and the United States.
In 2022, an inter-agency Counter Ransomware Task Force in Singapore recommended the use of PDNS as a form of “upstream defence” to prevent known malicious attackers from reaching internet users here.
This is because such attackers can trick users into downloading malware from malicious sites that can steal users’ company data or lock it up until a ransom is paid.
Navigating cyberspace safely is becoming more difficult. According to CSA’s latest Singapore Cyber Landscape report published in June, the number of malware-infected computer systems detected in Singapore more than doubled to 284,300 in 2025, from 117,300 infected systems detected in 2024.
“Singapore must raise the level of cybersecurity across our entire ecosystem,” said CSA on Oct 13, adding that such upstream protection is one of the key thrusts of the country’s refreshed cybersecurity strategy to counter more frequent and advanced threats.
The other pillars of the national strategy are: defending critical infrastructure; strengthening capabilities for AI and quantum technologies; and improving resilience through global partnerships.
Computer systems of critical infrastructure, or critical information infrastructure like those for power plants and telecommunications, are being increasingly targeted by hackers behind advanced cyberattacks that can stay undetected for long periods of time. These attackers are also called advanced persistent threat actors.
An attack in Singapore by one such group of hackers was revealed in July 2025. The country’s four major telcos were attacked by state- cyberespionage group UNC3886 . The attack could have disrupted telecommunications and internet services had the attackers infiltrated further.
Other new safety measures under Singapore’s updated cybersecurity strategy include exploring cyber insurance pilots, as well as the police setting up a new Cyber Command unit in July to target scammers and cybercriminals before they reach Singaporeans.
“The intensified threat landscape underpins the need for a command centre with enhanced national capabilities to detect cyber risks earlier and accelerate operational responses,” CSA said, referring to its National Cybersecurity Command Centre.
Announced in 2024, the centre detects and neutralises cyber threats before they reach Singapore’s shores .
Besides operating the PDNS, the centre will also allow cyber defenders of critical information infrastructure to combine threat intelligence from various sources to facilitate the coordination of cyber operations at a national level.
Shanmugam said that Singapore must act on a national scale, citing important lessons the country learnt from Operate Cyber Guardian, the nation’s largest coordinated defence which was launched following the UNC3886 attack on the four telcos.
“A sophisticated attacker does not see the Government and telcos as separate,” he said. “They look across the system and look for the weak point. Our national defence has to look across the system too. Government and industry have to work closely together in our response.”
Through CSA’s National Cybersecurity Command Centre, cyber defenders of critical information infrastructure will also be able to detect malicious activities, especially those of advanced persistent threat actors, with new proprietary threat detection systems developed by the Ministry of Defence’s Centre for Strategic Infocomm Technologies.
The ministry’s centre is working with CSA to equip selected infrastructure owners with the systems.
Shanmugam said that with this, the country can act earlier before threat actors cause serious harm.
“Adversaries are continuously looking for vulnerabilities and trying to establish persistent access,” said the senior minister.
“Our defence, therefore, has to be continuous. We need to consistently monitor and hunt for threats, identifying weaknesses before adversaries do so, and correcting them quickly.”
Separate systems will also be deployed that use AI to track ongoing incidents and help cyberdefenders to develop operational assessments and plan their actions. These will allow the National Cybersecurity Command Centre to coordinate faster responses to cyberincidents.
Wider adoption of AI and migration to quantum-safe systems are also part of Singapore’s refreshed strategy to strengthen protection.
Attackers are using AI tools to strike faster and at greater scale, while advancements in quantum computing threaten to undermine methods used today to encrypt data.
Shanmugam said that if AI lets attackers identify vulnerabilities and conduct attacks faster, defenders must use AI, too.
“The Government will progressively deploy AI across our national cyber defence operations,” he said, adding that this includes CSA’s National Cybersecurity Command Centre and the Government Technology Agency of Singapore’s Government Cyber Security Operations Centre.
“We will also work with industry and technology partners to speed up adoption of AI-enabled cyber defence capabilities across our critical sectors.”
AI/artificial intelligence
The full story
This article is one source in a clustered incident — the cluster page carries the summary, timeline and every other outlet covering it.
