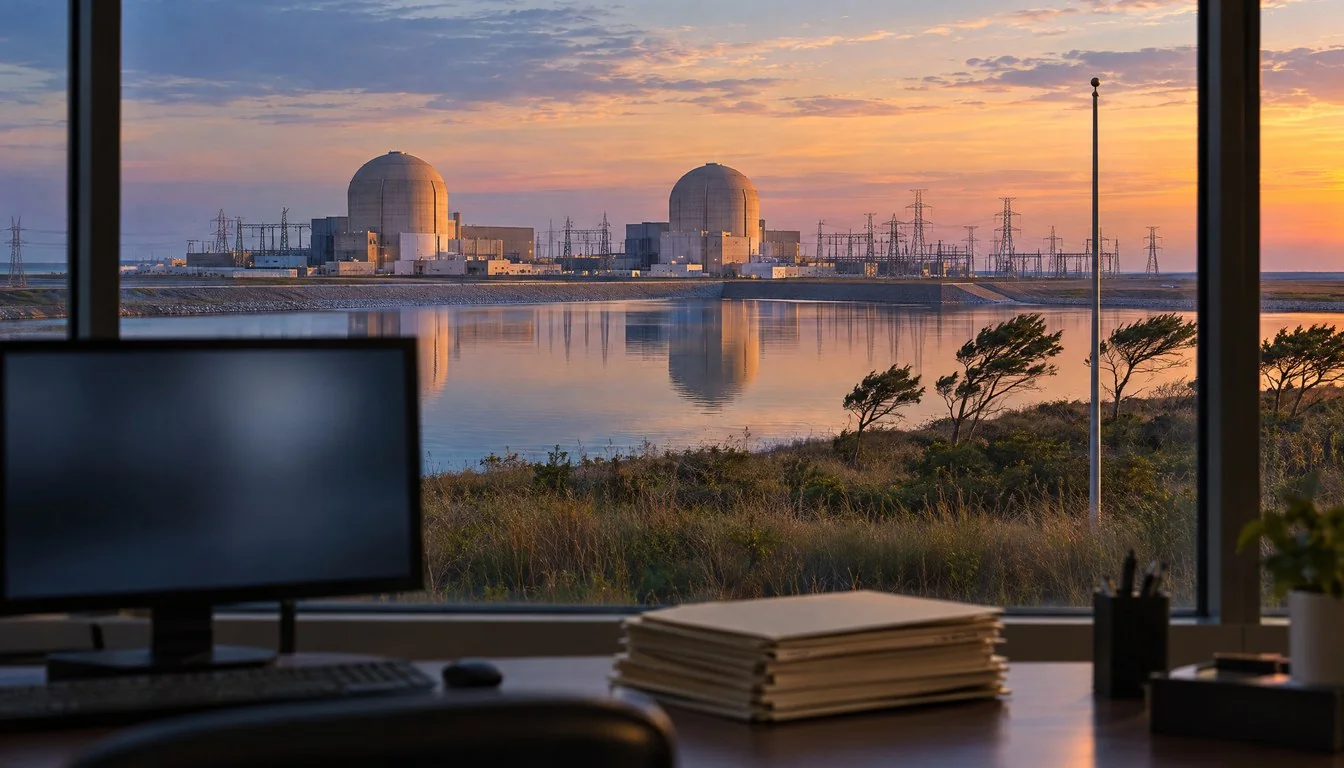
The operator of the South Texas nuclear power plant told Texas regulators this week that a data security incident exposed personal information belonging to 1,173 Texas residents. According to GovTech’s October 30 report, citing San Antonio Express-News reporter Brandon Lingle, STP Nuclear Operating Company filed the notice with the Texas Attorney General on October 28, 2026. The exposed data includes names, Social Security numbers, birthdates and other personal details.
The South Texas nuclear power plant data breach lands in a month already crowded with disclosure filings. Readers who followed our coverage of the Coinbase Amplitude third-party incident will recognize the pattern: a short notice, a headcount, a list of data fields, and very little cause. What sets this one apart is the name on the filing. The company runs two reactors, and any cyber incident at a nuclear operator draws attention that a typical corporate breach never gets.
So far, the public record is thin. The notice did not say whether the incident touched the plant’s operating or safety systems. The Nuclear Regulatory Commission, through a spokeswoman, said it remains satisfied that the plant continues operating safely and securely under agency requirements. This analysis separates what the reporting confirms from what it leaves open, explains why the personal-data angle still matters for a nuclear workforce, and sets out what to watch .
Don't miss new tech stories on Google
Add Shattered once in the Google app and our stories show up in your news suggestions.
What Happened at STP Nuclear Operating Company
STP Nuclear Operating Company, known as STPNOC, operates the South Texas Project Electric Generating Station near Wadsworth, Texas. GovTech describes the operator as a nonprofit and says the plant is partly owned by CPS Energy and Austin Energy, the municipal utilities of San Antonio and Austin. The company disclosed a data security incident to the state, and the filing identified 1,173 affected Texas residents.
ClaimDepot, a site that tracks breach filings for class action firms, dates the filing to October 28 and updated its page on October 29. GovTech published its story on October 30. That sequence matters for readers tracking the timeline. The filing date is the only hard date in the public record. Neither source states when the intrusion happened or when STPNOC discovered it.
Both outlets report that STPNOC notified affected people by email. Email notification is allowed under many state breach laws when a company has valid addresses and meets certain conditions, though it is a lighter touch than the mailed letters most large breaches produce. People who work for or contract with a nuclear operator are likely to have a corporate inbox, which may explain the choice, but no source confirms the reasoning.
The headline number is close to 1,200. GovTech rounds it to nearly 1,200 Texans. The precise figure in the filing is 1,173. That is small to the mass-scale breaches that dominate the news cycle, and it reads like an employee, former employee or contractor population rather than a customer database. Note that this is an inference from the size, not something the operator has said.
What the Texas Attorney General Filing Shows
Texas law requires organizations to report certain breaches to the state attorney general when they affect a set number of residents. The state publishes those notices in a public listing, and that is where the STP filing surfaced. GovTech reports that the listing currently shows 686 notices, 573 of them filed in 2026. The STP report is one entry in a long queue.
That volume says something the baseline. A year with 573 filings by late October averages out to more than one per day reaching the Texas regulator alone. Most of those never reach headlines. The STP notice did, because of who filed it and what the company does for a living. Any breach tied to a nuclear operator pulls in reporters, utility watchers and lawyers at the same time.
The filing counts Texas residents only. ClaimDepot’s page lists disclosure entries in a dozen other states, though it does not detail them. If people outside Texas received notices, the true total could exceed 1,173. Nothing in the sources confirms a larger number, so the conservative reading is the one to use: at least 1,173 people in Texas, possibly more elsewhere.
The attorney general listing also tends to be the first place plaintiffs’ firms look. ClaimDepot already runs a lawsuit investigation page for the South Texas Project incident, which tells us the claims-aggregation machinery has started. An investigation page is not a lawsuit. It is a marketing and intake effort, and no source reviewed for this story reports a filed complaint.
What Data Was Exposed in the South Texas Nuclear Power Plant Data Breach
GovTech lists four categories: names, Social Security numbers, birthdates and other personal information. That combination is the core kit for identity fraud. A name plus a Social Security number plus a birthdate lets a criminal open credit, file false tax returns or pass many knowledge-based verification checks. Unlike a password, none of it can be reset.
Confirmed versus aggregator-listed fields
ClaimDepot’s page adds addresses, government IDs, medical information and financial information to the list. Treat that wider list with caution. Aggregators often publish a generic of possible categories, and the page itself points readers to the email notice for specifics. GovTech’s shorter list is the better-supported one. Until STPNOC or a regulator publishes the notice text, the extra categories remain unconfirmed.
The gap between the two columns is the story’s first open question. If medical or financial data were involved, the risk profile for the 1,173 people changes, and so might the federal rules that apply. Neither outlet offers evidence either way.
The list of gaps is longer than the list of facts. The public record does not say how attackers got in, whether this was ransomware, theft by an outsider, a vendor compromise or an internal error. It does not say who is responsible. It does not say how long the data sat exposed. It does not say whether credit monitoring was offered, though ClaimDepot tells readers to check their email notice for any such services.
Silence on cause is common in early filings. Companies often complete a forensic review before they describe the mechanism, and attorney general notices typically ask for the number of residents rather than a root cause. Still, the absence of any attacker attribution means this story should not be read as a ransomware event or a state- operation. Neither claim has support in the sources.
Another unknown is who the 1,173 people are. Employees are the obvious guess, but contractors, job applicants, retirees and dependents all appear in breach populations at large employers. A nuclear operator also carries a heavy compliance burden around background checks and access authorizations, which means its records on individuals can run deeper than at a typical firm. The sources do not say what population was hit, so readers should hold that question open.
Plant Operations and the NRC Response
The most important sentence in the coverage comes from the federal regulator. An NRC spokeswoman told reporters that the agency remains satisfied the South Texas Project continues to operate safely and securely in line with agency requirements. That statement addresses plant safety. It does not describe the breach, and it does not say regulators reviewed the affected systems.
GovTech adds a careful caveat: the notice did not indicate whether the incident affected operating or safety systems. Put the two together and you get a narrow but meaningful reading. The regulator sees no safety concern today, and the operator has not claimed that plant systems were touched. Absence of a reported impact is not proof of absence, but it is the best available signal.
The distinction between corporate IT and plant control systems drives most expert thinking on nuclear cyber risk. The NRC’s cyber security rule, found in 10 CFR 73.54, focuses on digital assets tied to safety, security and emergency preparedness functions. Human resources databases and email systems generally sit outside that boundary, though how a given operator draws the line is a site-specific matter. A breach of personnel data can therefore be serious for the people involved without being a nuclear safety event.
That framing is analysis rather than reporting. No outlet has said the exposed data came from an HR system. But the data types, the roughly 1,200 headcount and the email notification all fit that profile better than they fit a breach of plant networks. A breach of plant networks would have triggered very different public statements from the NRC.
Who Owns and Runs the South Texas Project
Ownership shapes who answers questions. GovTech says the 35-year-old facility has two reactors producing 2.7 gigawatts and names CPS Energy, Austin Energy and Constellation South Texas LLC as owners. Wikipedia lists a nameplate capacity of 2,560 megawatts, 1,280 per unit, so the two sources differ slightly. We use the lower figure in the table below, and either way the plant is among the largest generators in Texas.
Two of the three owners are city-owned utilities, which adds a public-accountability layer. City councils, ratepayers and local reporters can ask CPS Energy and Austin Energy what they knew and when. That pressure is already building in Texas around utility costs, a theme we explored in our look at power bills and the midterms . A cyber incident at a shared plant adds one more item to the ledger of questions local officials will field.
Why Personnel Data Matters at a Nuclear Operator
A critic could ask why a roughly 1,200-person exposure deserves a long read. The answer has three parts. First, the people affected hold or have held jobs in a sensitive industry. Criminals and hostile intelligence services both value lists of individuals tied to critical infrastructure, because they make social engineering and spear phishing easier to aim.
Second, Social Security numbers are permanent. A leaked number can fuel fraud for decades. The financial harm lands on individuals, who often learn misuse long after the notice arrives. Credit freezes and monitoring reduce the risk, but they do not erase it.
Third, the breach is a reminder that critical infrastructure operators carry two separate attack surfaces. One is the operational network that runs equipment, which regulators police closely. The other is the ordinary corporate estate of email, file shares, HR platforms and vendors. Attackers frequently pick the second because it is softer. We saw the same logic in the DHS staff directory leak , where a list of names became a targeting tool without a single system being shut down.
None of this suggests that the STP incident was targeted at critical-infrastructure staff. The sources give no motive. The point is exposure: even a modest breach at a nuclear operator carries a higher downstream risk than the same headcount at a retail chain.
Texas Reporting Rules and Cyber Command
GovTech notes that operators of critical infrastructure in Texas must report incidents to the Texas Cyber Command. That requirement creates a second paper trail beyond the attorney general listing. The sources do not say whether STPNOC filed such a report, and state agencies rarely publish those submissions, so the public may never see them.
The attorney general notice covers consumer harm. The Cyber Command channel covers operational risk to the state. Together they give Texas two angles on the same event, and a company that handles both well can close the matter quickly. A company that handles one badly invites follow-up. For STPNOC, the NRC’s public reassurance has bought time, but state reporting duties will still apply.
For security teams outside Texas, the lesson is practical. Map every regulator that expects a filing before an incident, not after. Different agencies run different clocks, and a team that discovers the list mid-crisis loses days. Our guide to vulnerability management in Python covers the prevention side, and the notification side belongs in the same runbook.
Historical Context: The October 2025 Unusual Event
This is not the first time the plant has made security headlines recently. The Victoria Advocate reported that on October 13, 2025, STPNOC issued a Notification of Unusual Event, and the FBI took over the investigation. The company said the threat had not been sustained. Matagorda County Sheriff Jason Scates told the paper there was no danger to the public and described an unusual event as the lowest of four emergency classifications.
The Advocate’s report did not disclose the nature of that event, and it did not say the event involved a cyber incident. Nothing in the available sources links the 2025 event to this week’s breach. We mention it for context only. A year apart, two security-flavored items involving the same operator will make readers ask whether they connect. On the evidence so far, the honest answer is that no one has said they do.
The wider history is easier to state. Nuclear operators have spent the last decade hardening plant networks under NRC rules, while corporate systems have followed the same patchy path as every other large employer. Breach filings from energy companies have become routine, and the sector’s third-party exposure, from payroll vendors to benefits administrators, has grown with outsourcing. Without a cause from STPNOC, we cannot tell which path this incident took.
How This Breach Compares With Recent Incidents
Scale and data type separate one disclosure from the . The table below places the STP filing beside three incidents we have covered. All figures come from those earlier reports or from the STP sources above, and several remain unconfirmed.
Against those, STP is the smallest by headcount and the most sensitive by data type, since Social Security numbers carry more long-term risk than details. Our reporting on the BCD Travel breach claim shows how quickly plaintiff-firm announcements can run ahead of confirmed facts. The STP case has the opposite problem: the confirmed facts are few, and the speculation has not yet arrived in volume.
Market and Utility Impact
No source reviewed for this story reports a market reaction. STPNOC is a nonprofit, so it has no stock price to move. Constellation, one of the owners per GovTech, is publicly traded, but we found no reporting that ties its shares to this filing, and we will not guess at one. Readers should treat any claim of a market effect as unsupported.
The more realistic impact is on costs and governance. Breach response runs through forensics firms, legal counsel, notification vendors and, often, credit monitoring contracts. For a nonprofit operator owned by municipal utilities and a private generator, those costs flow back to the owners. Public owners also face open-records requests, which can pull internal incident documents into view.
Insurance is the other variable. Cyber insurers have tightened terms for energy and critical-infrastructure clients over recent years, and a filing like this one can colour renewal talks. No source says STPNOC carries cyber coverage or has made a claim. We flag the issue because owners and ratepayers will eventually ask who pays, and the honest answer is not yet available.
What Affected People Should Do Now
If you received the email from STPNOC, read it in full before acting. ClaimDepot advises recipients to check the notice for details on any credit monitoring or identity theft protection offered. If the email includes an enrollment code, use it promptly, since many such offers carry a deadline. Confirm that the message is genuine by finding the company’s details independently rather than clicking links, because breach notices attract imitation phishing.
Freeze your credit. A freeze at the three major bureaus is free and blocks most new-account fraud tied to a stolen Social Security number.
Pull your credit reports. Check for accounts you did not open and inquiries you did not authorize.
Get an IRS identity protection PIN. This blocks false tax returns
Watch for tailored phishing. Expect messages that cite your employer or the breach itself.
Keep the notice. Save the email and any reference numbers in case a claim process opens later.
Security teams can use the incident as a drill. Ask whether your own HR and payroll systems limit who can export Social Security numbers, whether vendors hold copies, and whether you could produce a count of affected residents by state within days. The answers decide how long a disclosure takes. For a related checklist on identity-driven risk, see our piece on zero trust after login .
Five Predictions for the STP Breach
These are our expectations, not reported facts. They rest on how similar filings have developed and could prove wrong as new details emerge.
More detail on cause within weeks. Local reporters in San Antonio and Austin will press CPS Energy and Austin Energy, and the public owners are more likely than a private firm to answer.
The headcount will stay small or grow only modestly. A larger number would require filings in other states to add up, and nothing so far suggests a big jump.
Plaintiff firms will keep investigating. The ClaimDepot investigation page is the first sign, and a complaint becomes more likely if the data types prove broader than reported.
The NRC will not change its safety stance without new evidence. The agency has said what it needs to say unless the incident turns out to touch plant systems.
Operators of critical infrastructure will review corporate data stores. Expect peer utilities to audit who can access Social Security numbers, since this filing shows that even a small leak makes national news.
The wildcard is attribution. If a ransomware group or other actor claims the breach, the story will shift quickly from a records disclosure to a threat-actor narrative. A claim would not prove anything on its own, and as we saw with the BCD Travel case, unverified claims deserve skepticism until a company or regulator confirms them. For wider context on current threats, see our security coverage and the roundup of October KEV advisories tied to edge devices .
Four markers will show where this goes. First, a copy of the notice text, which would settle what data was exposed. Second, any statement from CPS Energy or Austin Energy to their boards or councils. Third, additional state filings that would reveal a larger affected population. Fourth, any NRC inspection note or event report that mentions the incident, which would indicate regulators see a link to plant systems.
Absent those, the working picture is modest in scale and serious in kind. A nonprofit operator of a major Texas nuclear plant exposed sensitive identity data for 1,173 Texans. The federal regulator sees no safety problem. The cause is unknown. That is the full verified record as of October 31, 2026, and we will update this analysis if STPNOC, the state or the owners publish more.
FAQ: South Texas Nuclear Power Plant Data Breach
Who was hit by the South Texas nuclear power plant data breach?
STP Nuclear Operating Company, the nonprofit that operates the South Texas Project near Wadsworth, Texas, reported a data security incident. Its filing with the Texas Attorney General on October 28, 2026 identified 1,173 affected Texas residents, per GovTech and ClaimDepot.
What information was exposed?
GovTech reports names, Social Security numbers, birthdates and other personal information. ClaimDepot lists additional categories such as addresses, government IDs, medical and financial information, but those extras are unconfirmed.
Is the nuclear plant safe?
An NRC spokeswoman said the agency remains satisfied that the plant continues to operate safely and securely under agency requirements. The notice did not say whether operating or safety systems were affected.
How were people notified?
Who is responsible for the breach?
No one has been named. The sources do not disclose the cause, the method of access or any attacker, so claims of ransomware or state involvement have no support yet.
Who owns the South Texas Project?
GovTech names CPS Energy, Austin Energy and Constellation South Texas LLC as owners. Wikipedia lists the shares as 44% Constellation, 40% CPS Energy and 16% Austin Energy.
Can affected people sue?
Law firms have started investigating, and ClaimDepot runs an investigation page for the incident. No source we reviewed reports a filed lawsuit. This is general information and not legal advice, so affected people should consult a lawyer their options.
What should affected people do first?
Read the notification email for any credit monitoring offer, freeze credit at the three major bureaus, review credit reports, and consider an IRS identity protection PIN. Watch for phishing that references the breach or your employer.
The full story
This article is one source in a clustered incident — the cluster page carries the summary, timeline and every other outlet covering it.
