 Back Infosecurity-Magazine
US and Canadian Court Records Breached Following Thomson Reuters Incident
Thomson Reuters has disclosed a cybersecurity incident impacting its court management software, which has resulted in a breach of sensitive case data across Canada and the US.
The company detected activity affecting information held in its C-Track product, a digital case management system, on June 30.
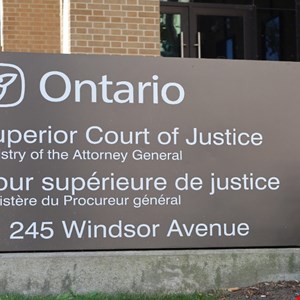
A subsequent investigation discovered that an unauthorized party obtained certain C-Track Canada files associated with three Ontario courts - the Court of Appeal for Ontario, the Ontario Superior Court of Justice and the Ontario Court of Justice.
“Based on the investigation, a subset of court records were affected, some of which could potentially contain individuals’ names and personal information. Certain confidential, redacted or sealed information may have been impacted for certain affected courts,” Thomson Reuters wrote in a statement released on September 2.
The data breach was also confirmed in a public statement by Ontario's three Chief Justices, who warned it is possible that personal information relating to individuals involved in court proceedings or mentioned in court documents may have been exposed.
Alongside the Ontario courts, the C-Track incident has also impacted appellate courts in 11 US states and the US Virgin Islands, West Publishing Corporation, a US-based provider of court management solutions owned by Thomson Reuters, revealed in a separate statement.
These states are South Carolina , Nevada, New Hampshire, North Dakota, Ohio, Kentucky, Pennsylvania, Alabama, Montana, Tennessee and North Dakota.
West Publishing said the affected court records potentially contain individuals’ personal records, including names, Social Security numbers, driver’s license numbers, medical information, dates of birth and health insurance information.
Like with the Ontario courts, certain confidential, redacted or sealed information may have been impacted for certain affected courts.
The investigation is ongoing to establish the specific content and types of information breached at each affected court, as well as the number of individuals whose information may have been impacted.
Thomson Reuters said there is no evidence that systems used to process financial transactions were impacted by the incident.
No details have been provided on how the C-Track records were accessed. However, Thomson Reuters emphasized that the incident was not caused by the courts' networks, systems or data security.
There’s no evidence that the affected data has been misused for fraud or other purposes to date.
Court Records in High Demand
Court documents are known to be a target for a range of threat actors, including nation-state groups for espionage purposes, malicious actors attempting to disrupt or influence individual cases, and financially motivated cybercriminals using sensitive court data to extort individuals and organizations.
In August 2025, the US federal judiciary announced stronger cybersecurity protections for sensitive court documents following “recent escalated cyber-attacks” on its case management system.
The statement followed reports that the federal case filing system was breached by threat actors, exposing sensitive court documents in multiple US states.
Toyota Reveals Data Leak of 300,000 Customers News 11 October 2022
Toyota Reveals Data Leak of 300,000 Customers
Personal Information of Nearly Two Million Texans Exposed News 18 May 2022
Personal Information of Nearly Two Million Texans Exposed
Marriott Agrees $52m Settlement for Massive Data Breach News 10 October 2024
Marriott Agrees $52m Settlement for Massive Data Breach
Overcoming the AI Privacy Predicament Opinion 8 March 2024
Overcoming the AI Privacy Predicament
Discord.io Halts All Operations After Massive Data Breach News 15 August 2023
Discord.io Halts All Operations After Massive Data Breach
What’s Hot on Infosecurity Magazine?
65% of Enterprises Have Seen AI Agents Act Out of Scope
FulcrumSec Claims Responsibility for Manchester Airport Group Breach
Healthcare Giant McKesson Investigates Data Breach Incident
Manchester Airports Group Hit by Cyber Incident
Attackers Steal METR API Key and Burn $600,000 in AI Credits
Google Cloud's New CISO Chris Betz on Integrating AI in Cyber Defenses
Manchester Airports Group Hit by Cyber Incident
DDoS Attack Hits Norwegian Government Services
Fake Voicemail SVG Attachments Fuel Large-Scale Phishing Campaign
Linux Foundation Introduces TRACE Standard for AI Runtime Evidence
Threat Actors Abuse Cursor Agent AI to Assist Ransomware Operations
Attackers Steal METR API Key and Burn $600,000 in AI Credits
Same Front Door, New Visitors: Securing Humans and AI Agents at the Browser
How To Enhance Security Operations with AI-Powered Defenses
Human Risk in Cybersecurity: Protecting Your Organization Beyond Technology
Dispelling the Myths of Defense-Grade Cybersecurity
Financial Services Cyber Resilience: Stress Testing Third Parties Before Attackers Do
Revisiting CIA: Developing Your Security Strategy in the SaaS Shared Reality
How Faster Cyber-Attacks Are Reshaping Enterprise Cybersecurity Strategies
Researchers Claim First Fully Agentic Ransomware: JadePuffer
AI is Already Powering Cyber-Attacks. Can it Power Cyber Defense?
Google Cloud's New CISO Chris Betz on Integrating AI in Cyber Defenses
How World Cup Password Trends Can Increase Active Directory Risk
New CISA Guide Helps Agencies Adopt SASE For Zero Trust
The full story
This article is one source in a clustered incident — the cluster page carries the summary, timeline and every other outlet covering it.
