 News.Tuoitre.Vn
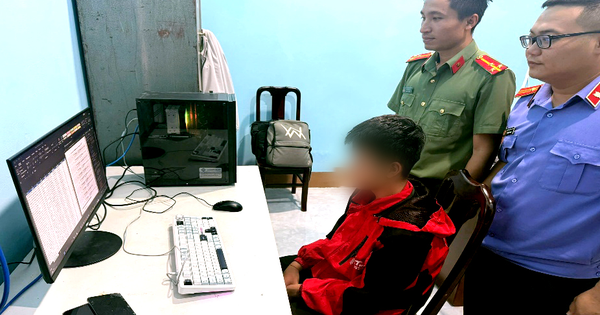
10th Grader Hacks National Vaccination System, Sells 20 Million Personal Records
Article Content

- •A 10th-grade student hacked the National Immunization Information System.
- •Nearly 20 million personal records were stolen and sold for over 100 million VND.
- •Authorities are urging improved cybersecurity measures to prevent future breaches.
On June 5, 2026, a 10th-grade student from Nghe An Province was prosecuted for illegally accessing the National Immunization Information System. The student, N.H.A., exploited security vulnerabilities to collect and sell nearly 20 million personal records, earning over 100 million VND. The investigation revealed that he self-taught programming and used online resources to develop algorithms for the hack. Authorities emphasized the serious threat this poses to privacy rights and warned of potential fraud risks. The police have initiated measures to strengthen cybersecurity and prevent similar incidents. Legal consequences for such actions include fines and imprisonment under Articles 288 and 289 of Vietnam's Penal Code. The case highlights the need for better education on cybersecurity and legal implications among youth.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Love and Ministry Of Health in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…