 iczelia.net
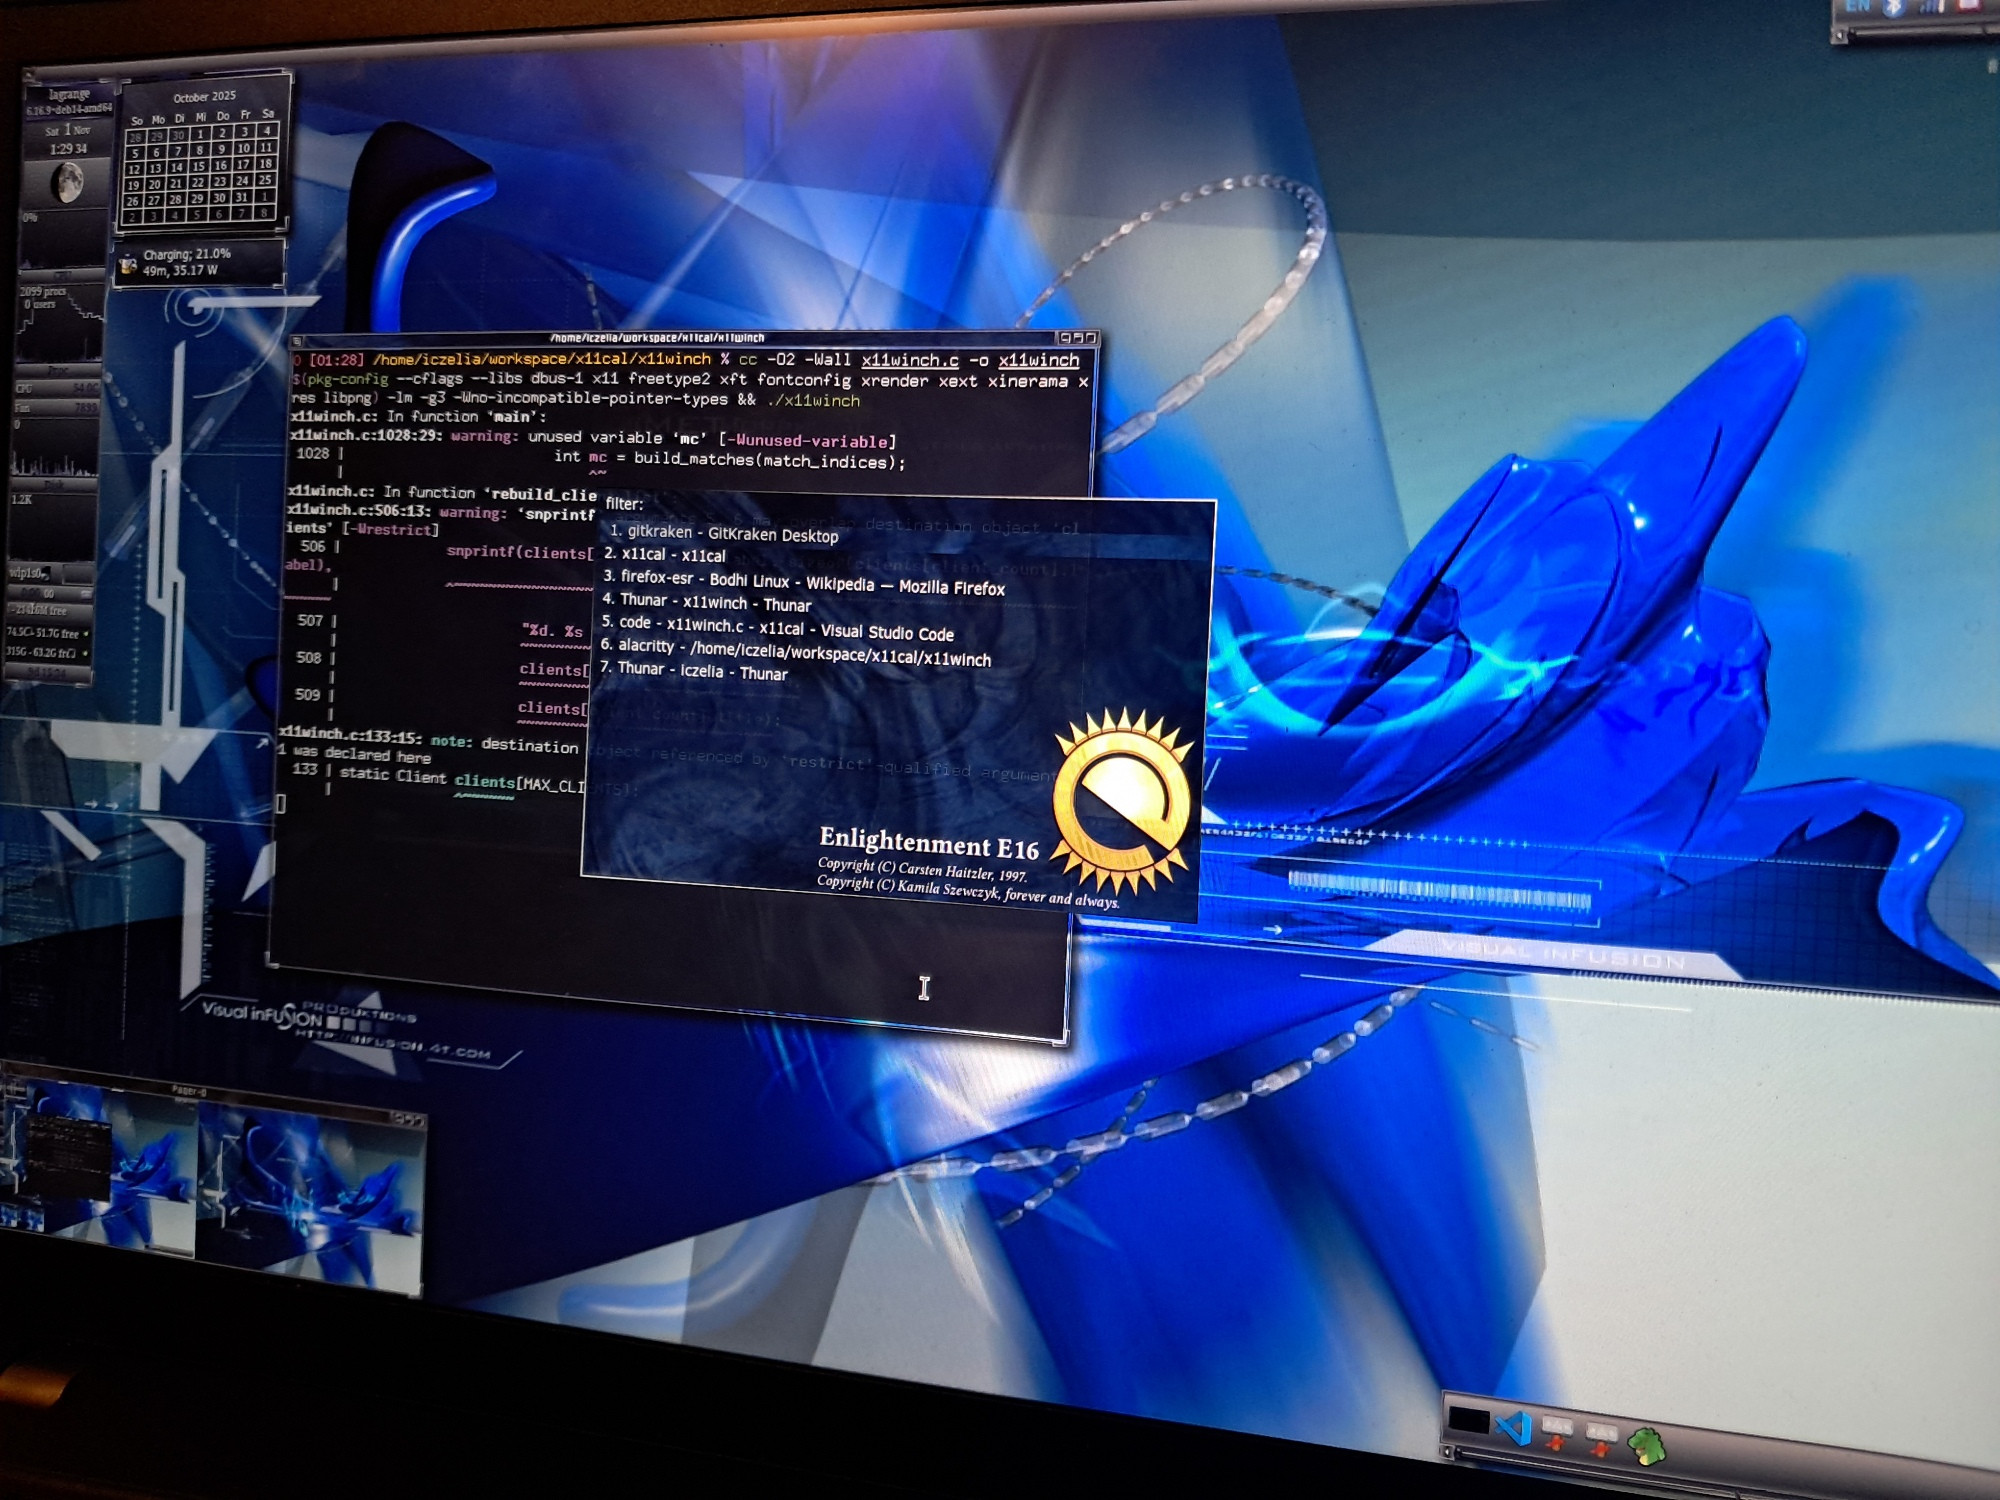
20-Year-Old Bug in Enlightenment E16 Window Manager Fixed
Article Content

- •A 20-year-old bug in E16 caused desktop freezes when opening specific PDFs.
- •The bug was fixed by a developer who prefers the older window manager over modern alternatives.
- •The fix includes capping iterations to prevent infinite loops in the truncation algorithm.
A 20-year-old bug in the Enlightenment E16 window manager was fixed by Kamila Szewczyk, a 21-year-old developer. The bug caused the desktop to freeze when opening certain PDFs due to an infinite loop in the window-title truncation algorithm. Szewczyk discovered the issue while preparing lecture slides at Saarland University. The bug was traced to the lack of an iteration limit in the truncation algorithm, which could lead to a denial-of-service scenario. The fix, released as a patch against E16 1.0.30, includes capping iterations at 32 and preventing negative corrections. Szewczyk criticized modern software development practices, arguing they lead to instability. The E16 window manager, first released in 1997, is still maintained by a small community of enthusiasts despite the existence of newer versions. This incident highlights the potential for similar bugs in modern software systems.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…