 Thecooldown
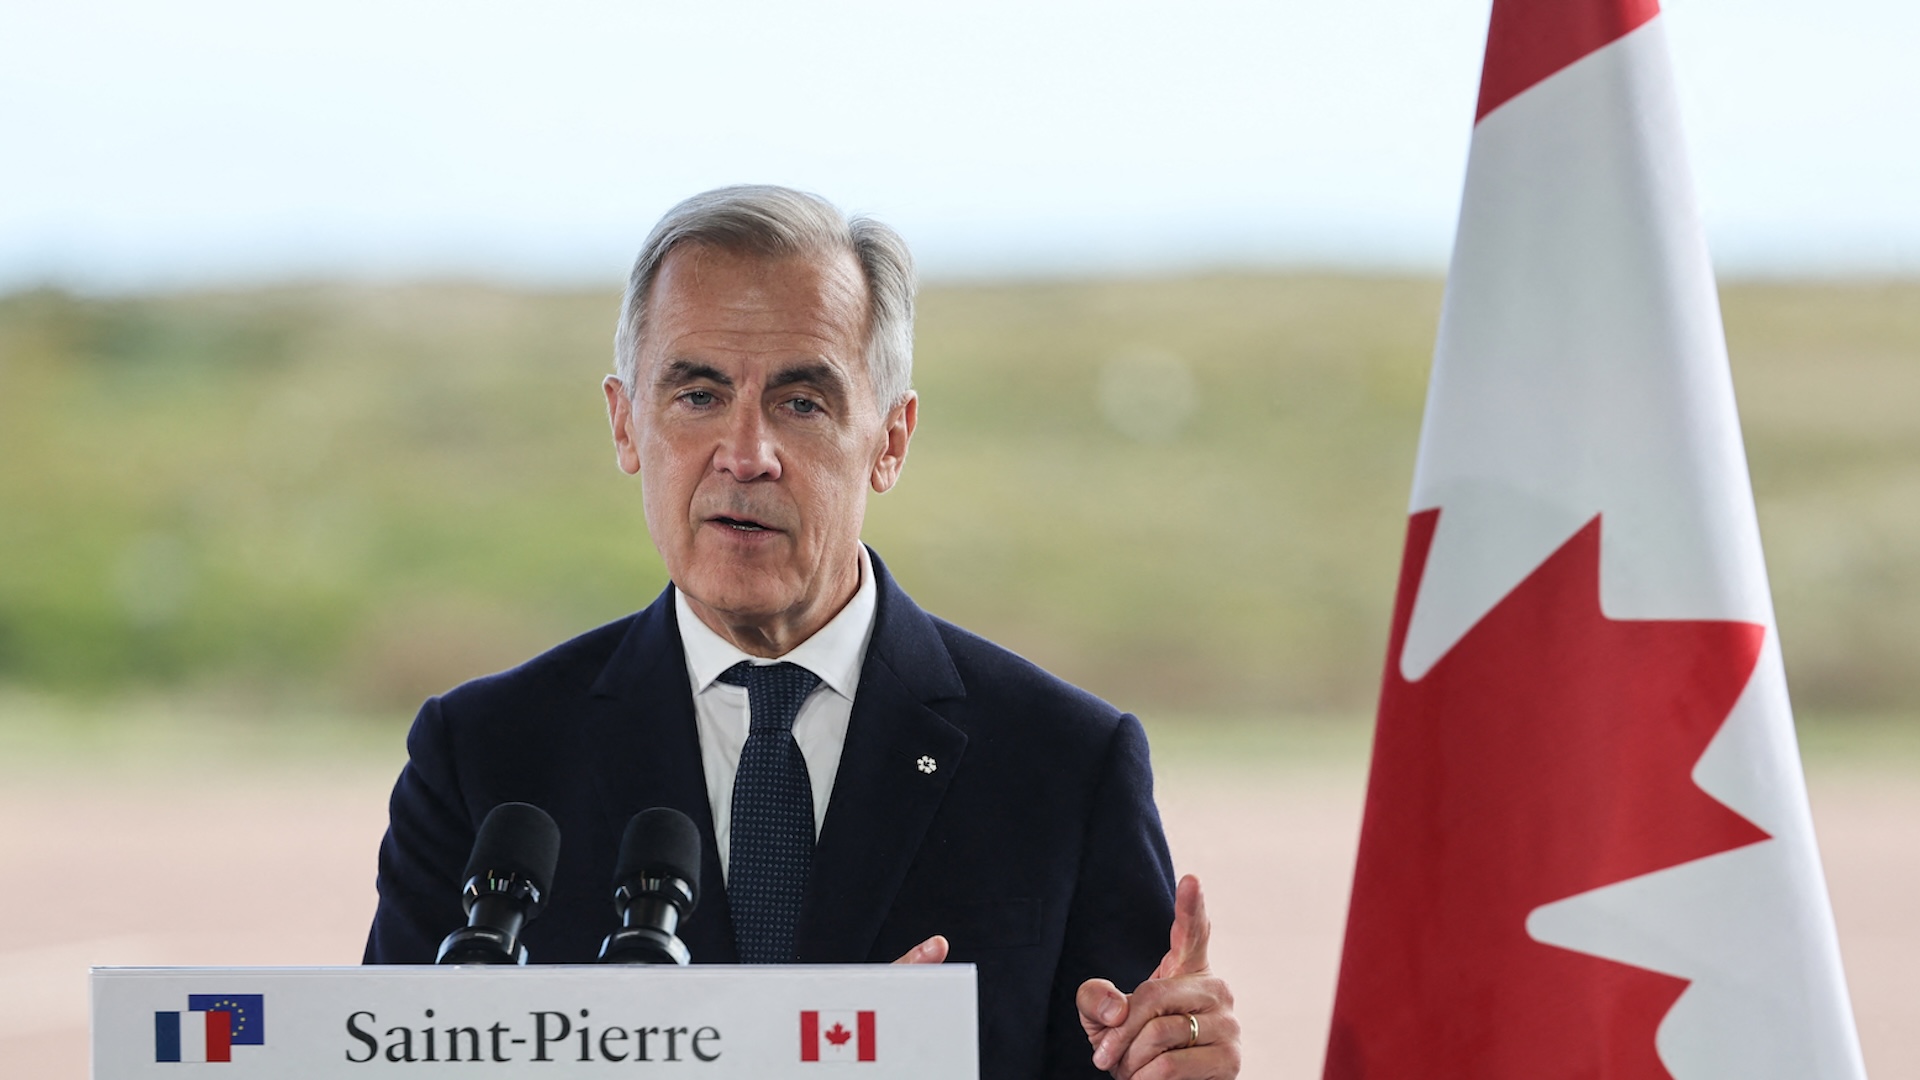
88-Year-Old Loses $450,000 to Deepfake Investment Scam Involving Prime Minister's Video
Article Content

- •An 88-year-old man lost $450,000 to a deepfake investment scam.
- •TD Bank failed to prevent fraudulent transactions despite recognizing suspicious activity.
- •Canadian banks are criticized for inadequate consumer protection against fraud.
An 88-year-old man from British Columbia lost $450,000 to an online investment scam that utilized a deepfake video of Prime Minister Mark Carney. Ralph Moore began sending money in May 2025 after being misled by the fraudulent promotion. Despite the bank, TD Bank, recognizing suspicious activity and temporarily restricting his account, they did not freeze it or prevent further transactions. Moore's daughter criticized the bank for not acting sooner, especially since they had a long history with her father. The Canadian Anti-Fraud Centre reported over $700 million in fraud losses in 2025, with only 5% of victims reporting incidents. Consumer advocates argue that Canadian banks should be held more accountable for fraud losses, similar to regulations in the UK. Moore's case highlights the need for better consumer protection and bank protocols against fraud.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track BMO in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What should victims do if they fall for a scam?
How can banks improve fraud detection?
What legal protections exist for fraud victims in Canada?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 Critical BeyondTrust 9.3 Vulnerability Actively Exploited by Threat Actor A critical vulnerability (CVE-2026-102764) in BeyondTrust Remote Support has been discovered and is actively being exploited by the threat group ARMORY CASTLE, reportedly linked to China. The vulnerability, which has a CVSS score of 9.3, allows unauthenticated attackers to upload files and potentially compromise host…