 Guardian.Ng
Adekunle Gold Wins Landmark Cyberbullying Conviction Against Social Media User
Article Content

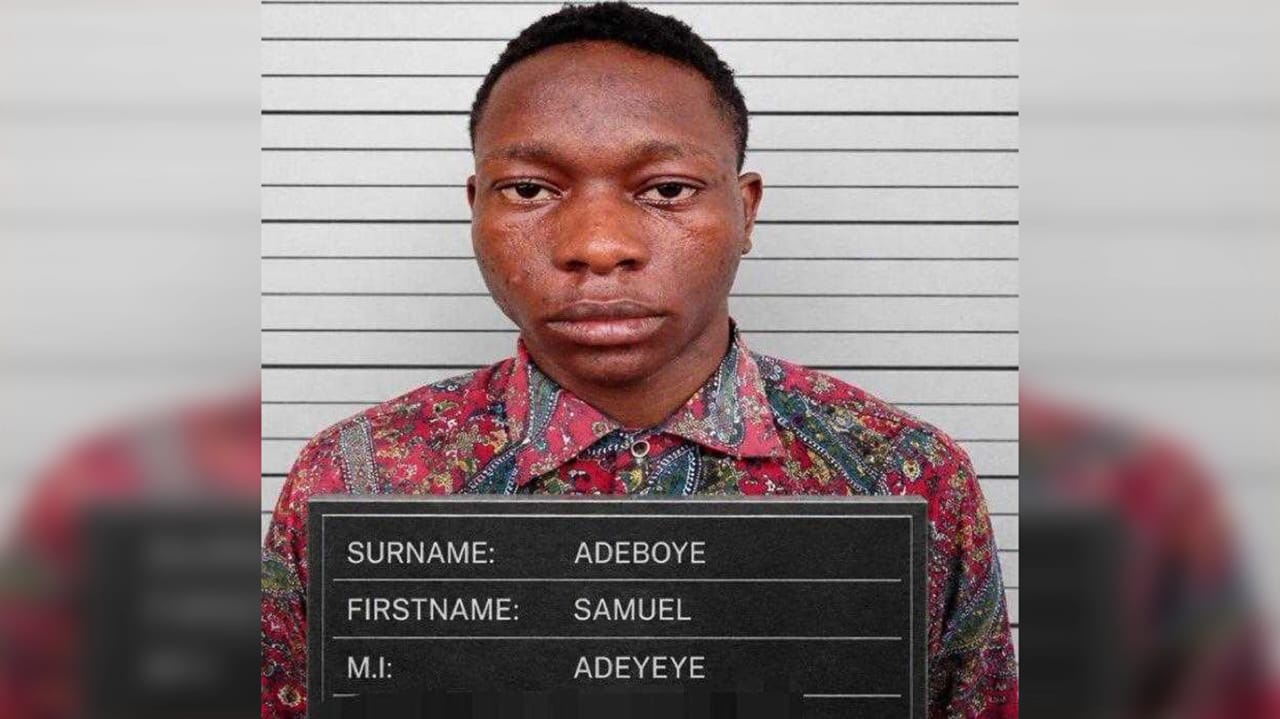
- •Adeboye Samuel Adeyeye was convicted for cyberbullying Adekunle Gold and his family.
- •The court sentenced Adeyeye to two years for cyberbullying and threats, with sentences running concurrently.
- •Adekunle Gold's legal team is investigating additional accounts involved in defamatory campaigns.
Nigerian singer Adekunle Gold is pursuing legal action against additional social media users for defamation following the conviction of Adeboye Samuel Adeyeye, known as @Swanky001, for cyberbullying, threats, and harassment. The Federal High Court in Lagos sentenced Adeyeye to two years in prison for cyberbullying and threats, and one year for harassment, with sentences running concurrently. The case stemmed from false claims made by Adeyeye about Gold's daughter, which he amplified despite public outcry. The ruling is seen as a significant step in addressing online harassment and misinformation in Nigeria. Adekunle Gold's legal team is investigating other accounts linked to similar defamatory actions. The case has sparked discussions about accountability for online behavior and the responsibilities of social media users.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Following this threat?
Track X in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…