 Theguardian
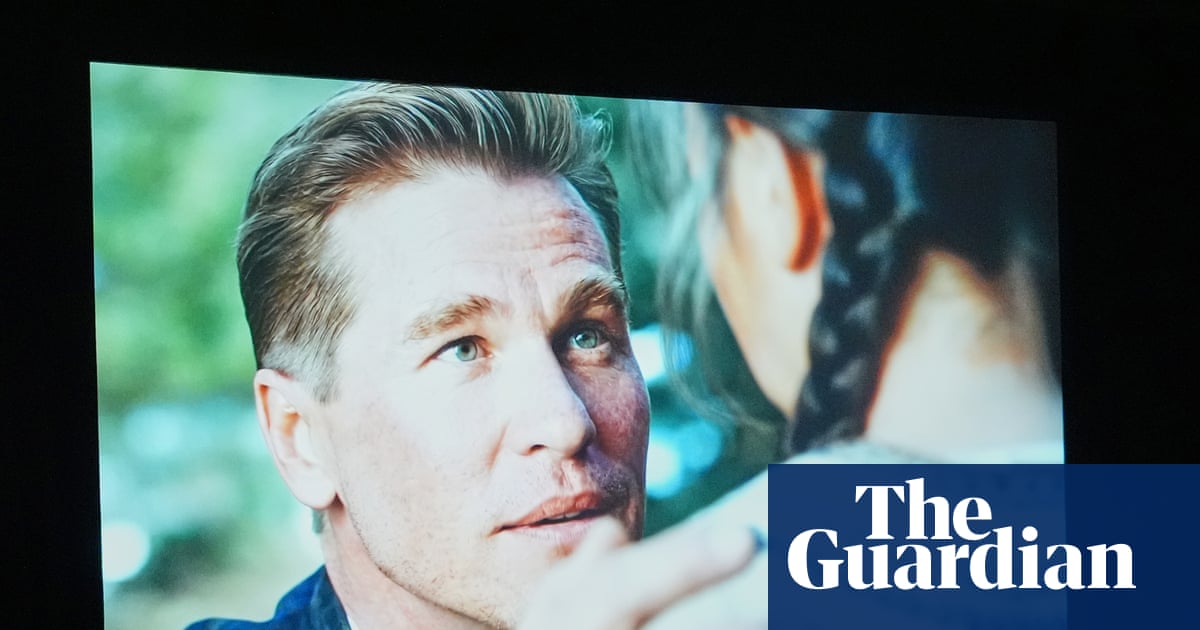
AI Deepfake of Val Kilmer in Film Sparks Controversy and Outrage
Article Content

- •The first trailer for 'As Deep As the Grave' featuring an AI version of Val Kilmer has sparked outrage.
- •Critics argue that using AI to recreate deceased actors is disrespectful and sets a dangerous precedent.
- •The film's production was influenced by budget constraints and received approval from Kilmer's family.
The trailer for the film 'As Deep As the Grave' featuring an AI-generated version of Val Kilmer has been released, leading to significant backlash online. Kilmer, who passed away in April 2025, was digitally recreated for a substantial role in the film despite not having filmed any scenes due to production delays. The creative team collaborated with Kilmer's estate and used technology from Sonantic to generate his voice and likeness. Critics argue that this use of generative AI raises ethical concerns about the portrayal of deceased actors and sets a troubling precedent for the film industry. While some support the project, many online commenters have labeled it disrespectful. Writer-director Coerte Voorhees stated that the decision to use AI was influenced by budget constraints and the blessing of Kilmer's children. The film's narrative revolves around married archaeologists in the 1920s, with Kilmer's character serving as a spiritual guide. The controversy highlights ongoing debates about the implications of AI in entertainment and the treatment of digital likenesses of deceased individuals.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…