 Devops
AI-Driven Development Increases Vulnerability Risks Despite Faster Remediation
Article Content

- •Vulnerability remediation has improved, with critical vulnerabilities resolved faster than before.
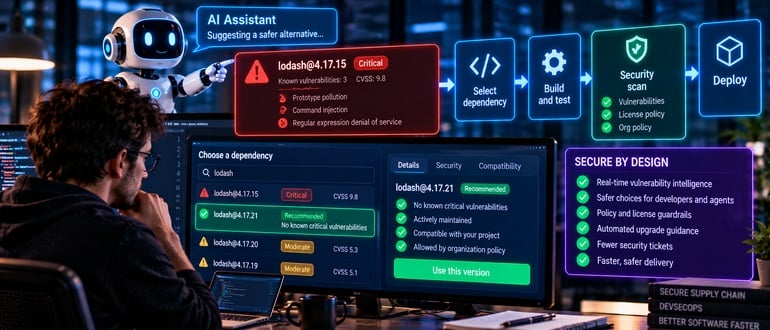
- •AI-assisted development accelerates dependency decisions, increasing the risk of selecting vulnerable components.
- •Security teams need to integrate security context earlier in the development process to mitigate risks.
In 2026, vulnerability remediation has improved significantly, with the median age of unresolved critical vulnerabilities dropping by 59% since January 2024. However, the rise of AI-assisted development is leading to faster and more numerous dependency decisions, which can result in the selection of vulnerable components. Security controls that only scan after dependencies are chosen create avoidable rework and larger backlogs. As a result, applications continue to accumulate risk even as remediation speeds up. Teams are urged to provide security context earlier in the development process to help developers and AI agents make safer choices. The 2026 Verizon Data Breach Investigations Report highlights that vulnerability exploitation is a leading breach vector, accounting for approximately 31% of breaches. The current status indicates a need for improved integration of security measures during the selection of dependencies.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Azure in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
How fast are vulnerabilities being fixed?
What risks does AI introduce?
What should teams do to mitigate risks?
Continue Reading
 Critical Authentication Bypass in Cisco Catalyst SD-WAN Manager Exploited On September 30, 2026, Cisco disclosed a critical vulnerability (CVE-2026-76504) in the Catalyst SD-WAN Manager that allows unauthenticated remote attackers to bypass authentication and gain admin-level access to the system. This flaw stems from improper handling of URI encoding in HTTP requests, enabling attackers to…
 Critical Citrix NetScaler Vulnerabilities Actively Exploited in Finland The National Cyber Security Centre Finland (NCSC-FI) issued an alert regarding critical vulnerabilities in Citrix NetScaler ADC and Gateway products, specifically CVE-2026-88771 and CVE-2026-88772, which are being actively exploited in Finland. These vulnerabilities allow attackers to execute remote code without…