 Smh.Au
AI-Generated Memes Target Albanese Amid Tax Reform Controversy
Article Content

- •Meme campaign distorts Albanese's tax reform proposal, misleading the public.
- •Frank Greeff initiated the campaign using AI-generated images for viral impact.
- •The controversy highlights challenges in communicating tax policy amidst misinformation.
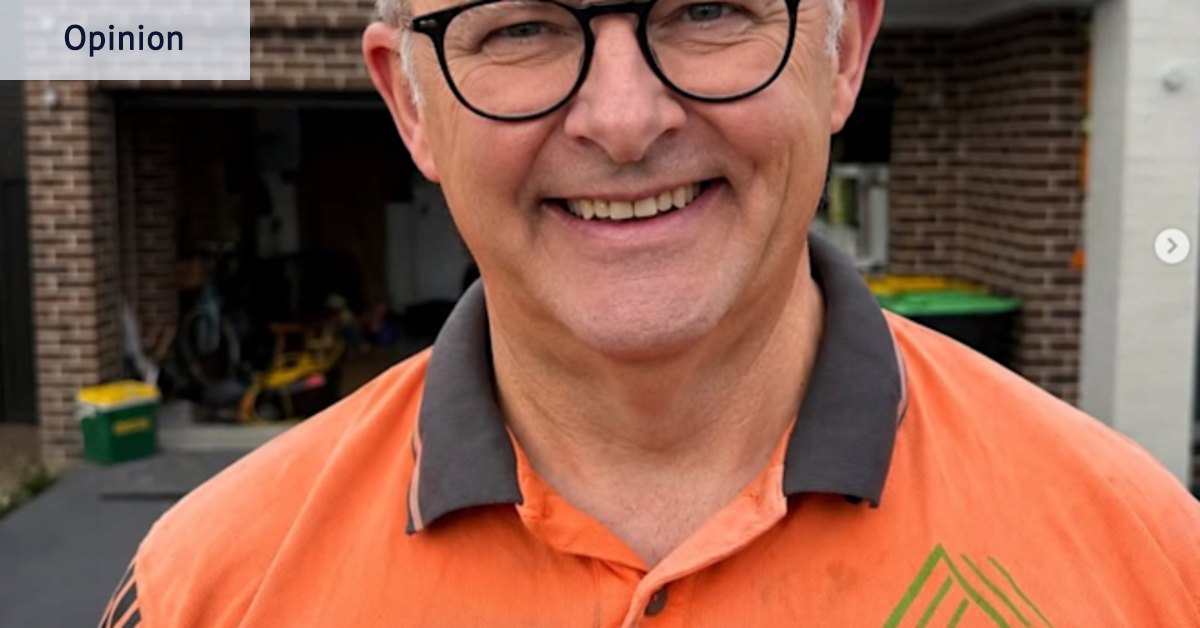
Prime Minister Anthony Albanese faces backlash from a meme campaign following Labor's budget proposal to roll back capital gains tax concessions. Business founder Frank Greeff initiated the campaign by posting an AI-altered image portraying Albanese as a co-owner of small businesses, distorting the government's tax policy. The memes suggest Albanese would take a 47% equity stake in businesses, referencing the top marginal tax rate rather than actual ownership. Greeff's campaign has led to further AI-generated images depicting Albanese in various humorous contexts, prompting discussions about the implications of misinformation in the digital age. The campaign highlights the challenges of communicating complex tax reforms in a meme-driven social media landscape. Albanese's attempts to clarify the policy have struggled against the viral nature of the memes. The situation underscores the intersection of politics, social media, and the potential for disinformation.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track X in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…