 Defsec.Nz
Airbus and Broadtech Collaborate on Next-Gen Communications for New Zealand
Article Content

- •Airbus and Broadtech signed an MoU to enhance New Zealand's communication services.
- •The partnership focuses on transitioning to high-availability broadband for public safety.
- •No specific cybersecurity threats or vulnerabilities were reported in the articles.
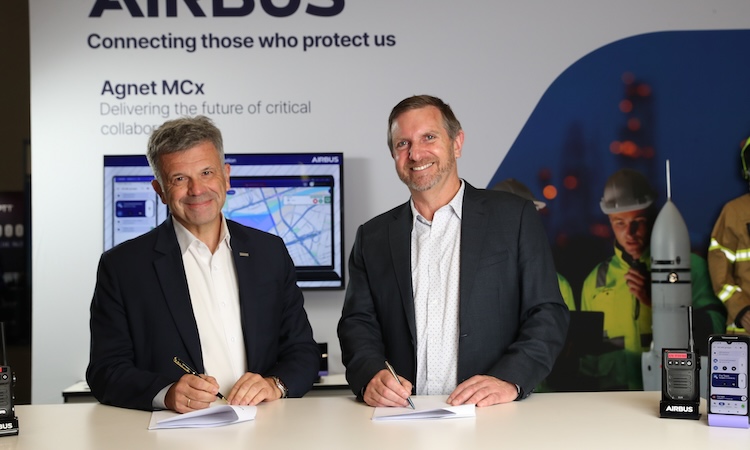
Airbus Defence and Space and Broadtech have signed a Memorandum of Understanding (MoU) to enhance New Zealand's communication infrastructure. The 12-month agreement aims to transition from legacy narrowband to high-availability broadband mission-critical services. The partnership will focus on delivering secure Push-to-Talk, Push-to-Video, and broadband data for public safety agencies, government entities, and critical infrastructure sectors. The MoU was signed at Comms Connect 2026 in Melbourne by Alain Ruinet of Airbus and Merv Taylor of Broadtech. This collaboration seeks to modernize communication networks for emergency services and improve resilience across the country. Airbus plans to leverage its global capabilities alongside Broadtech's local expertise. The initiative will also explore solutions for utilities, healthcare, and transport sectors. No specific cyber threats or vulnerabilities were reported in the articles.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Airbus Defence And Space in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What is the purpose of the MoU?
Who are the key players in this collaboration?
What sectors will benefit from this initiative?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 CISA Warns of Exploited Vulnerabilities in ProFTPD, ONLYOFFICE, Strapi, and More The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added five vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, including critical flaws in ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND. These vulnerabilities are being by Chinese actors for cyber espionage, targeting…