 Theneurondaily
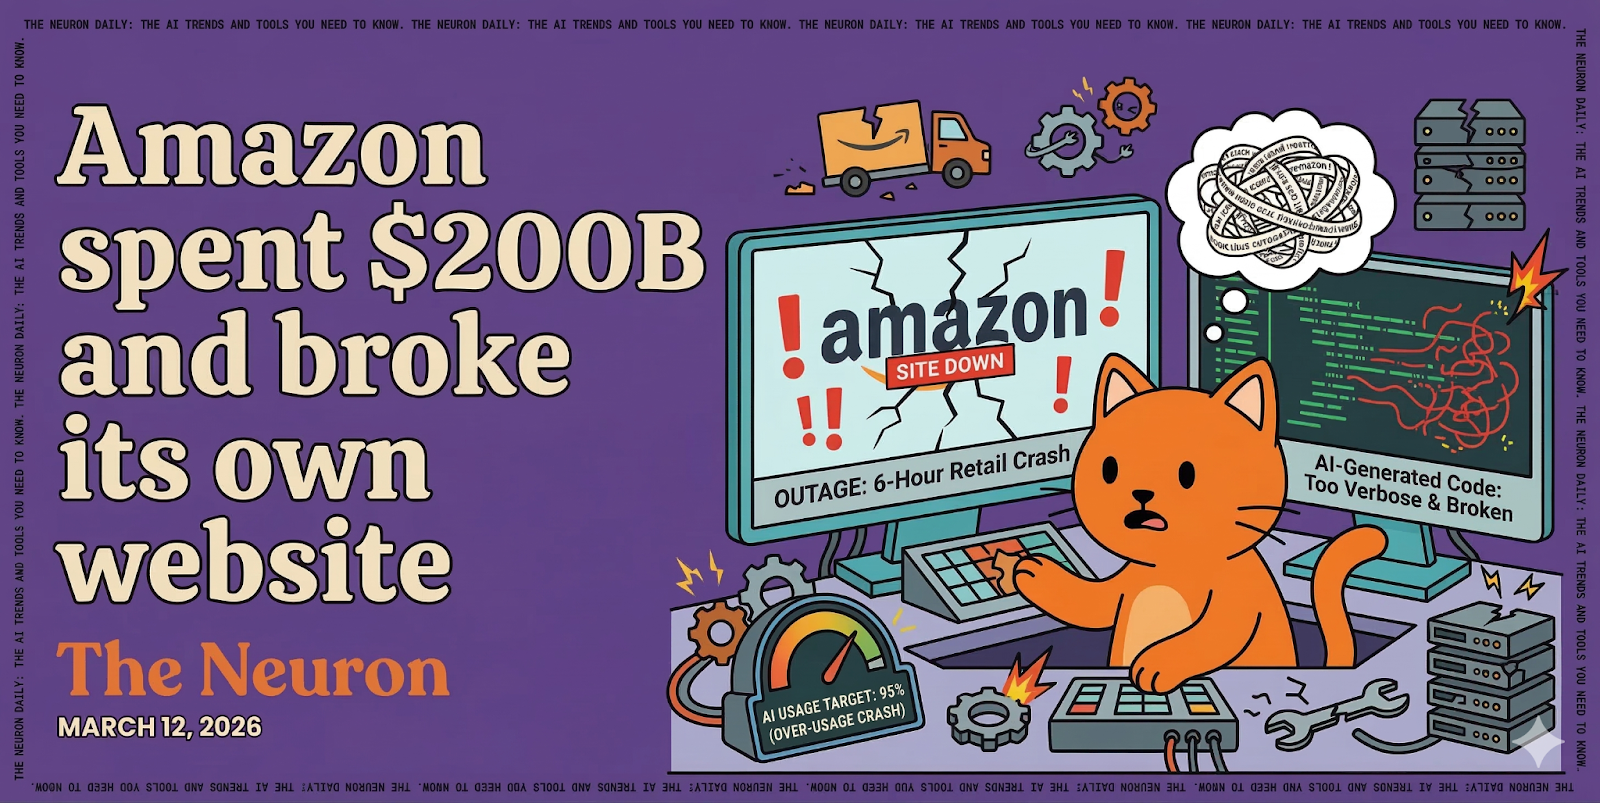
Amazon Faces Outages Linked to AI-Generated Code Changes
Article Content

- •Amazon's retail site suffered a six-hour outage due to AI-assisted code changes.
- •The company attributes the issues to user error rather than AI-generated code.
- •Mandatory senior sign-off for AI-assisted changes has been implemented following the incidents.
Amazon experienced significant outages affecting its retail website and app, including a six-hour crash that hindered customer transactions. The outages have been attributed to 'Gen-AI assisted changes' in code, leading to internal discussions about the fragility of their infrastructure. Despite these incidents, Amazon disputes that AI-generated code is to blame, citing user error and misconfigured access controls instead. The company has mandated that junior and mid-level engineers require senior sign-off for any AI-assisted code changes. AWS also faced a separate incident in December 2025, where its Kiro AI tool caused a 13-hour outage due to similar issues. Amazon's recent layoffs and push for AI tool usage have raised concerns about the effectiveness of their engineering practices. The situation has prompted a mandatory engineering meeting to address the outages and improve operational protocols.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Amazon in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…