 Aol
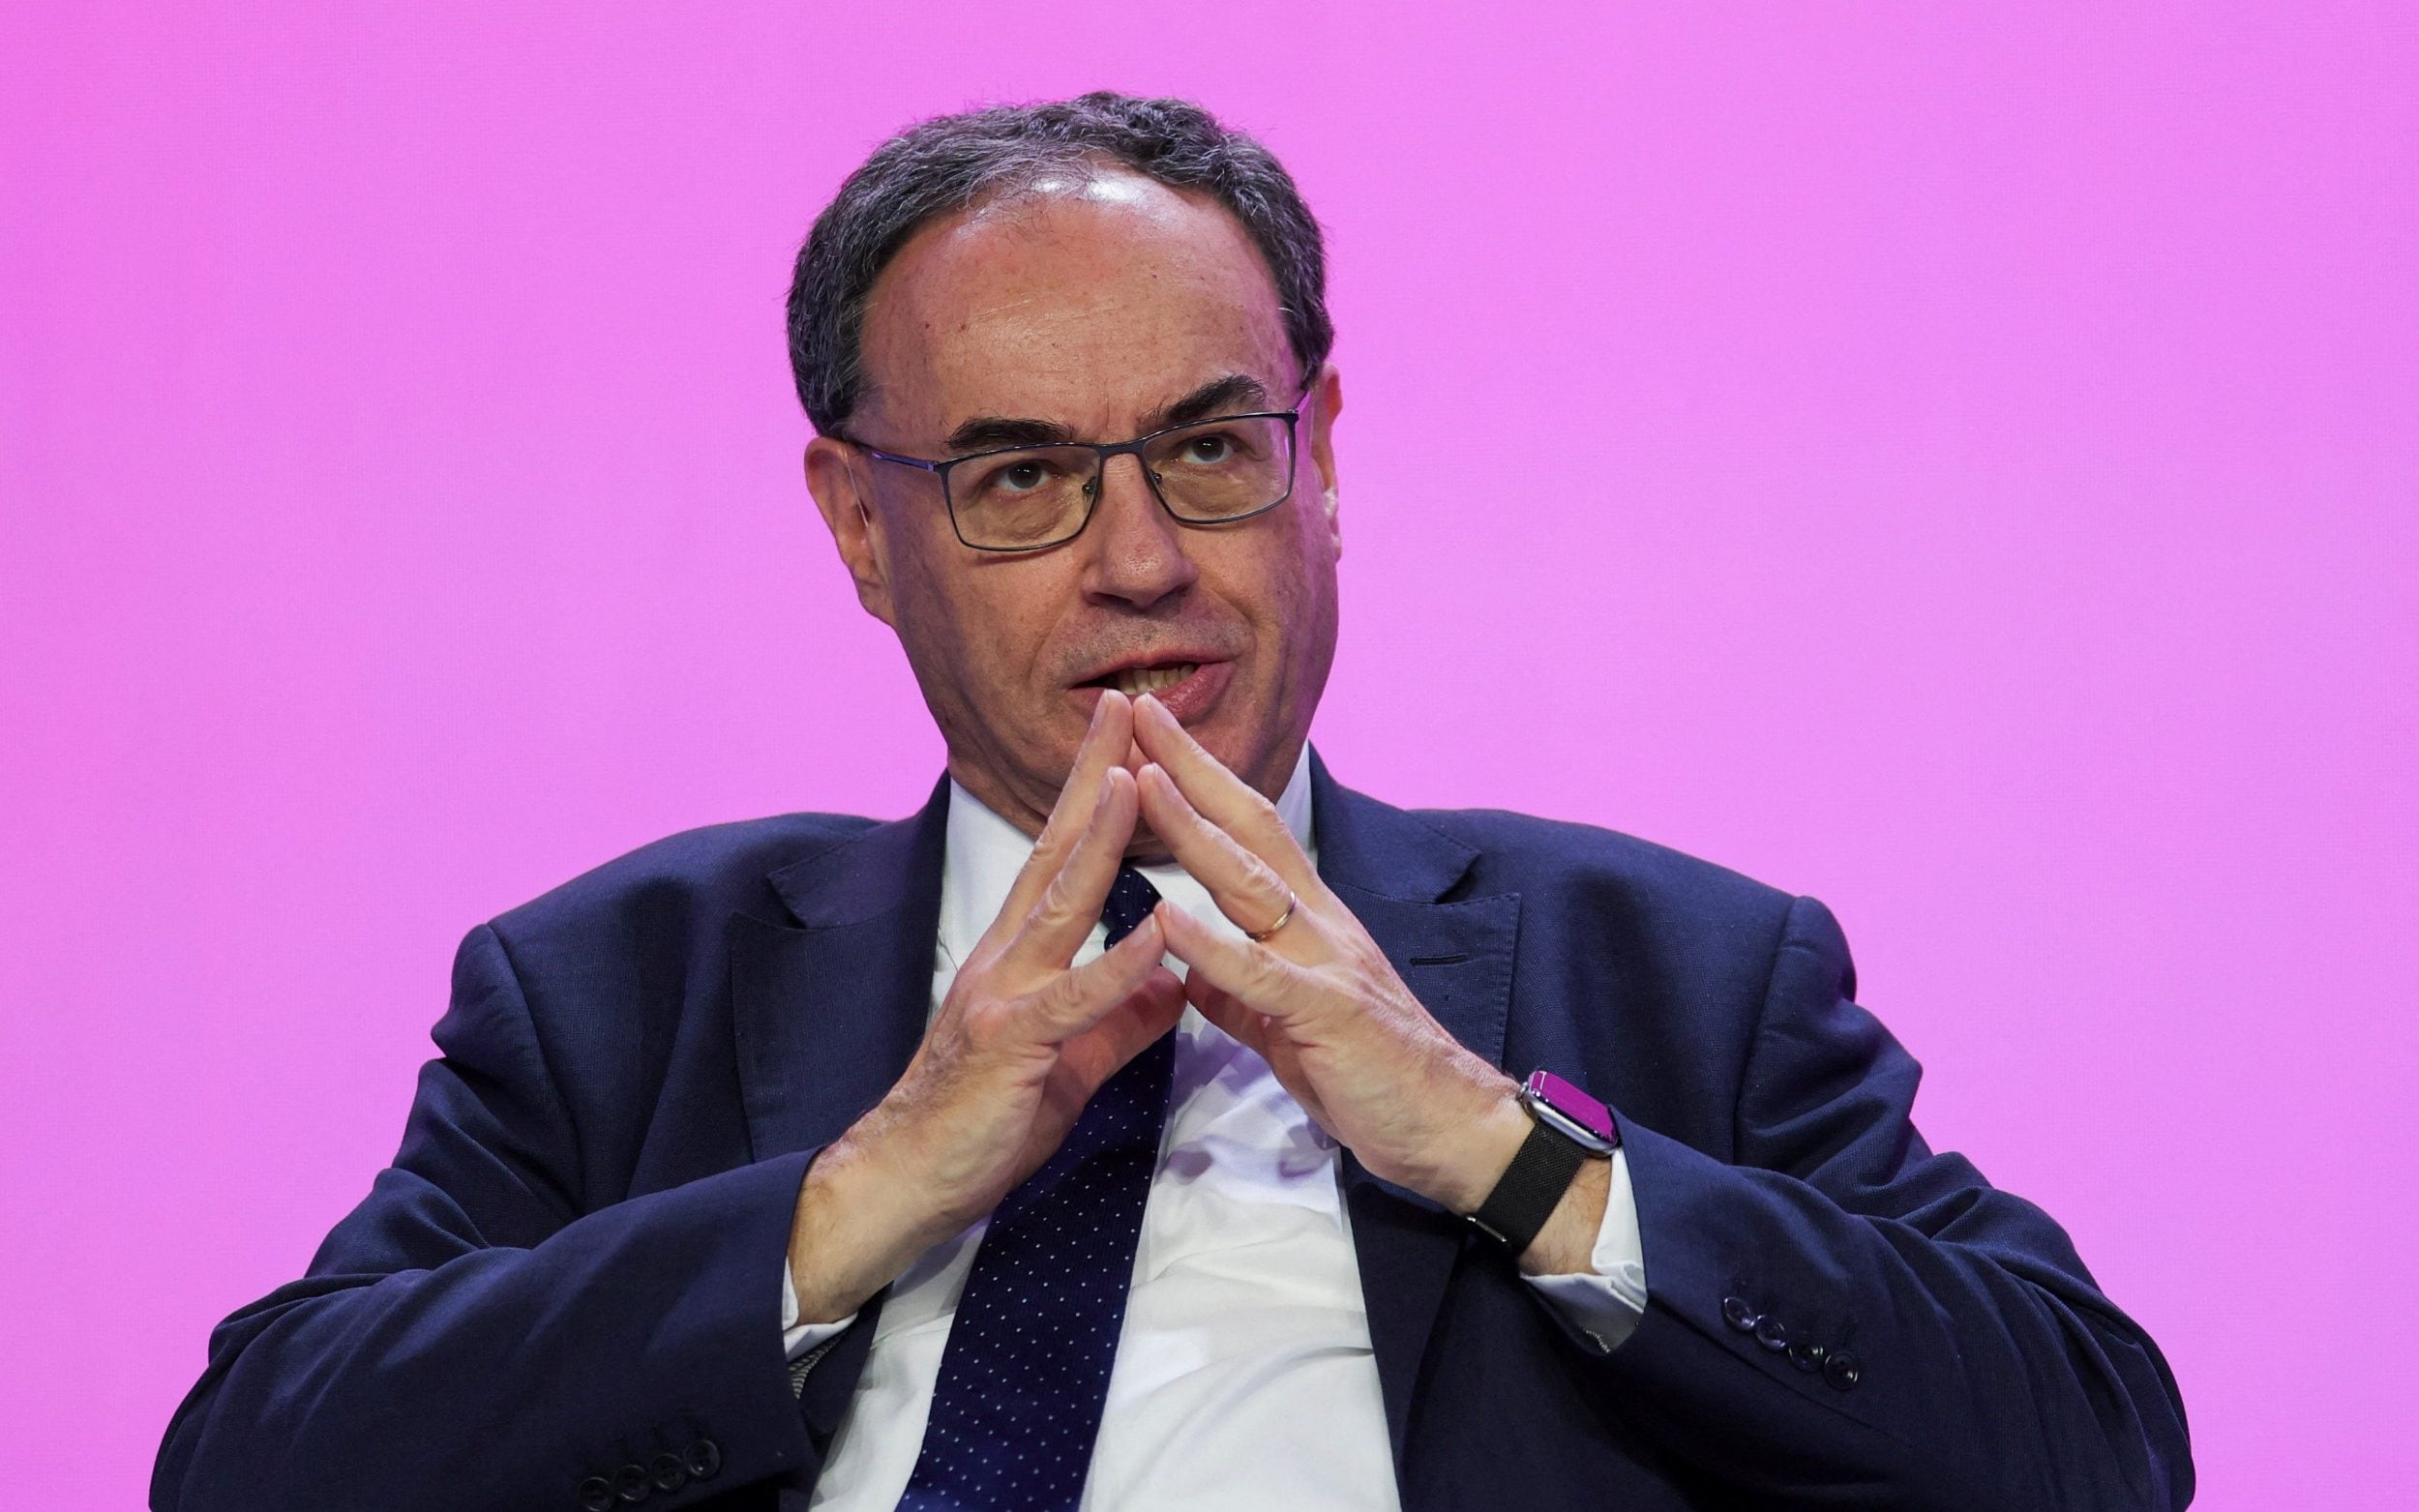
Andrew Bailey Criticizes Social Media for Fraud Amid Deepfake Incident
Article Content

- •Andrew Bailey demands accountability from social media platforms for online fraud.
- •Bailey was a victim of deepfake content involving him and Nigel Farage.
- •UK Finance reported £1.28 billion lost to payment fraud in 2025, emphasizing the scale of the issue.
Andrew Bailey, Governor of the Bank of England, criticized social media platforms for their lack of accountability regarding online fraud, particularly after he was depicted in deepfake videos. At an IMF event in Bangkok, he highlighted that these platforms host a mix of legitimate and fraudulent content, complicating public discernment. Bailey emphasized the need for tech companies to take responsibility, stating that traditional media faces legal accountability, unlike social media. He also warned against relying on a compensation culture, advocating for improved technology and systems to combat fraud. IMF chief Kristalina Georgieva echoed these sentiments, noting the potential for significant financial losses due to rising scams. In 2025, UK Finance reported £1.28 billion was lost to payment fraud, with a significant portion initiated online.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track X in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What specific actions are being proposed for tech companies?
How significant is the financial impact of online fraud?
What role does the IMF play in this issue?
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…