 www.diarioestrategia.cl
Android 17 Enhances Security with Advanced Protection Features
Article Content

- •Android 17 introduces 'Failed Authentication Lock' to enhance security against unauthorized access.
- •The AccessibilityService API is now restricted to verified tools, reducing malware exploitation risks.
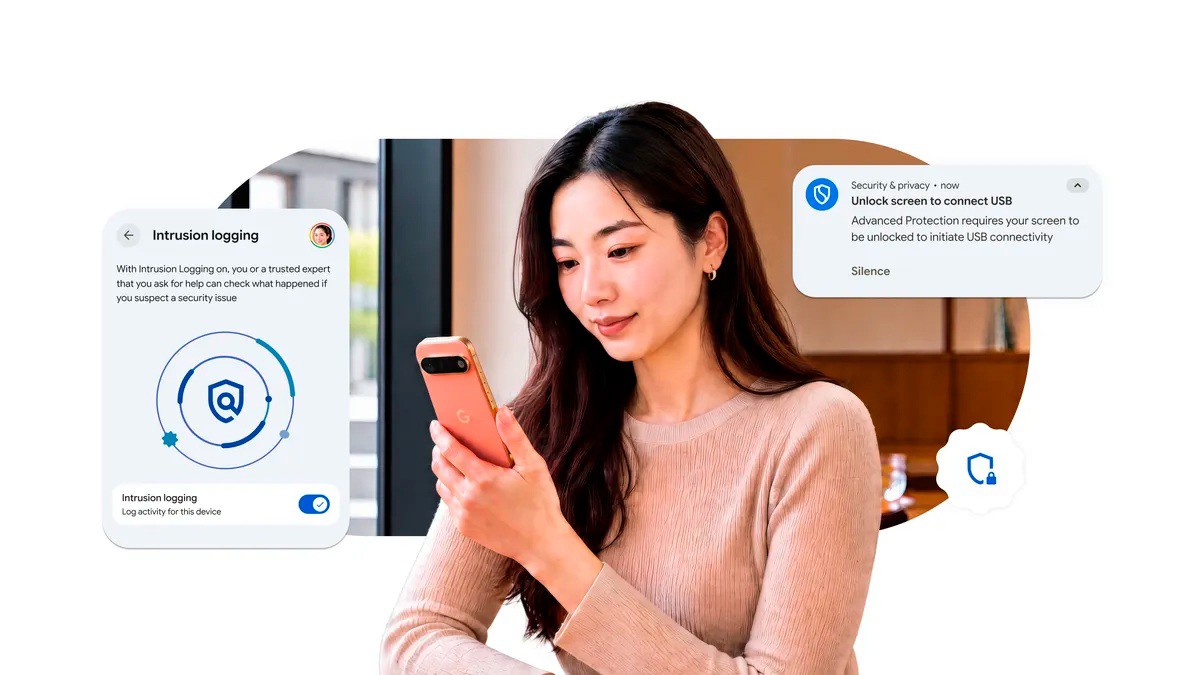
- •New defenses include protections against physical attacks and unauthorized USB access.
Google has introduced new security measures in Android 17 as part of its Advanced Protection initiative, which aims to mitigate risks associated with authentication failures and misuse of the AccessibilityService API. The 'Failed Authentication Lock' feature will lock devices after multiple failed authentication attempts in protected apps and system settings, preventing unauthorized access. Additionally, the update restricts the AccessibilityService API to verified accessibility tools, addressing vulnerabilities exploited by malware, particularly banking trojans. These changes enhance defenses against physical attacks, brute-force attempts, and unauthorized USB access, creating a more secure environment for Android users. The updates are designed to protect sensitive user data while maintaining accessibility for those who need it. The implementation of these features is for users of banking and private applications, as it directly addresses potential exploitation vectors.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Chameleon in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What is the 'Failed Authentication Lock'?
How does the AccessibilityService restriction work?
What types of attacks does the new security enhance against?
Continue Reading
 Citrix NetScaler Critical Vulnerabilities Exploited: Urgent Patching Required Citrix NetScaler ADC and Gateway products are affected by critical vulnerabilities CVE-2026-88771 and CVE-2026-88772, both assigned a CVSS score of 9.5. The Cybersecurity and Infrastructure Security Agency (CISA) added these CVEs to its Known Exploited Vulnerabilities catalog on September 27, 2026, and mandated…
 Critical Citrix NetScaler Zero-Day Vulnerabilities Exploited Citrix disclosed two critical zero-day vulnerabilities, CVE-2026-88771 and CVE-2026-88772, affecting NetScaler ADC and Gateway systems, which are being actively exploited. Both vulnerabilities have a CVSS score of 9.5 and allow unauthenticated attackers to execute arbitrary commands remotely. CVE-2026-88771 arises…