 Huntress
APT41 Cyber-Espionage Tactics Explored in Ransomware Emulations
Article Content
Browse articles 
The article discusses the fifth volume of AttackIQ’s Ransom Tales series, which simulates the tactics of ransomware families REvil, DarkSide, and BlackMatter. These emulations are designed to help organizations validate their detection and response workflows against the methodologies used by the APT41 group in cyber-espionage campaigns.
Ask AI about this cluster
Answers cite the sources they use
Updated 228d ago How this analysis works
More articles in this cluster (14)
Following this threat?
Track BlackMatter, APT41 and CVE-2017-17562 in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
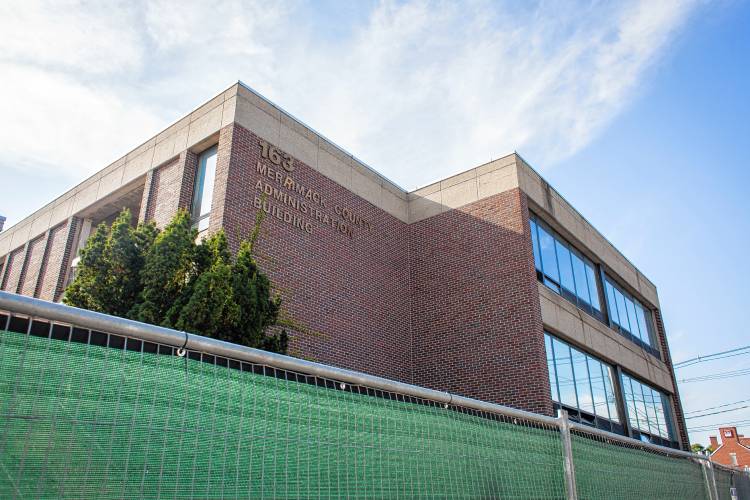 Ransomware Targets Backup Systems: Merrimack County Avoids Ransom Payment Merrimack County experienced a ransomware cyberattack in late August 2026 that disrupted services. County Administrator Ross Cunningham confirmed that their backup systems allowed them to restore operations without paying a ransom. The specific details of the attack remain limited, and there is no indication of AI or…
 New BlackX Bootkit Targets Central Asian Diplomats via Baton Drop Exploit In early 2026, a sophisticated APT campaign utilizing the BlackX UEFI bootkit was discovered targeting diplomatic agencies in Central Asia, specifically Tajikistan, Uzbekistan, and Turkmenistan. The BlackX bootkit exploits the Baton Drop vulnerability, allowing it to bypass Windows Secure Boot and maintain persistent…