 Ans
Argonne Study Assesses Flood Risks from Tropical Cyclones to Nuclear Plants
Article Content

- •Argonne's study projects a 78% increased risk of flooding for nuclear plants in the Bay of Bengal.
- •The research utilized advanced simulations to assess the impact of tropical cyclones on coastal infrastructure.
- •Recommendations include updating safety protocols and conducting detailed flood risk assessments for new infrastructure.
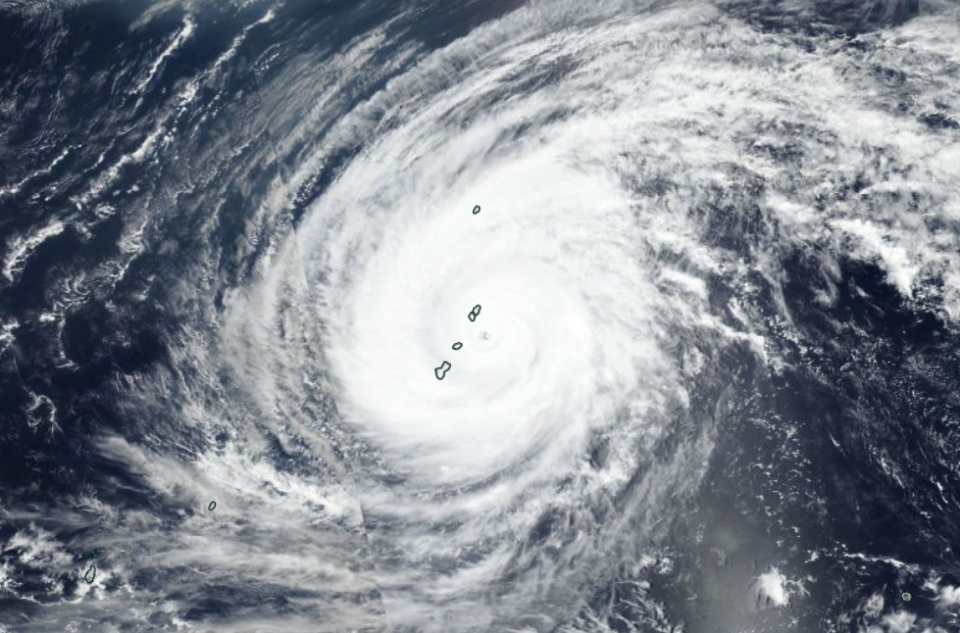
Researchers at Argonne National Laboratory have published a study evaluating the risk of flooding caused by tropical cyclones on coastal infrastructure, particularly nuclear power plants. The study utilized advanced computer simulations to project potential damage from extreme storm tides, with a focus on the Bay of Bengal. The findings indicate a 78% increased risk from low-frequency flooding events along India's eastern coast, where the Kovvada Atomic Power Project is located. The researchers recommend improving safety protocols for existing infrastructure and conducting detailed flood risk assessments for new projects. Their simulations were validated using historical cyclone data, highlighting the need for more resilient designs in the face of climate change. The study emphasizes the importance of thorough risk evaluations for nuclear facilities in hydrologically complex coastal areas. The research was published in the journal npj Natural Hazards.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…