 Nigerianobservernews
Army Chief Warns Misinformation as Major Security Threat
Article Content

- •Misinformation is now considered a major security threat by military leadership.
- •Public support for military operations is deemed a strategic necessity for success.
- •The military seeks stronger collaboration with media to counter disinformation.
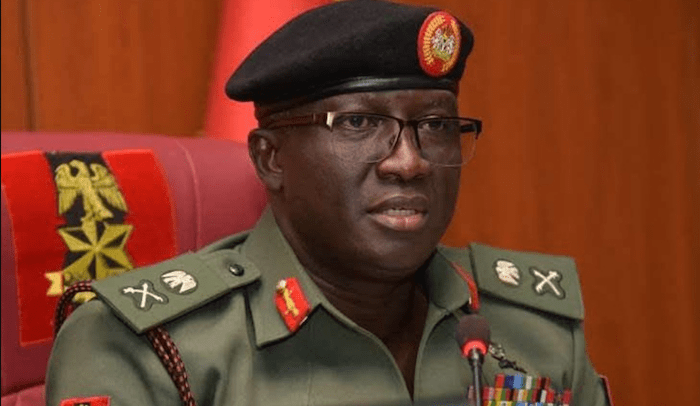
On June 9, 2026, Lt.-Gen. Waidi Shaibu, the Chief of Army Staff, addressed the Directorate of Army Public Relations workshop in Abuja, emphasizing that misinformation is now a significant security threat. He stated that adversaries exploit propaganda and information manipulation to undermine public confidence and national security efforts. Shaibu highlighted the necessity of public support for military operations, describing it as a strategic requirement for operational success. He called for stronger collaboration between the military and media to counter disinformation and enhance public awareness. The workshop aimed to develop strategies for effective media engagement in the context of modern security challenges. Shaibu reiterated the importance of accurate information dissemination to bolster troop morale and national resilience against misinformation. He urged media practitioners to actively support military communication objectives. The event reflects a growing recognition of the role of information warfare in contemporary security dynamics.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Continue Reading
 Critical Zero-Day Vulnerability in Cisco Secure Email Gateway Exploited On September 14, 2026, Cisco disclosed a critical SQL injection vulnerability (CVE-2026-76461) in its Secure Email Gateway, allowing unauthenticated remote attackers to execute arbitrary commands with root privileges. This vulnerability arises from insufficient validation in the email parsing logic. Cisco confirmed…
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…