 Dvidshub
Army Hosts AI Tabletop Exercise to Enhance Cyber Defense Against AI-Driven Attacks
Article Content

- •The Army's AI TTX 2.0 involved 14 cybersecurity executives from leading tech companies.
- •The exercise simulated AI-driven cyberattacks in a hypothetical Indo-Pacific crisis scenario.
- •Participants aimed to identify scalable AI tools to enhance Army cyber defense capabilities.
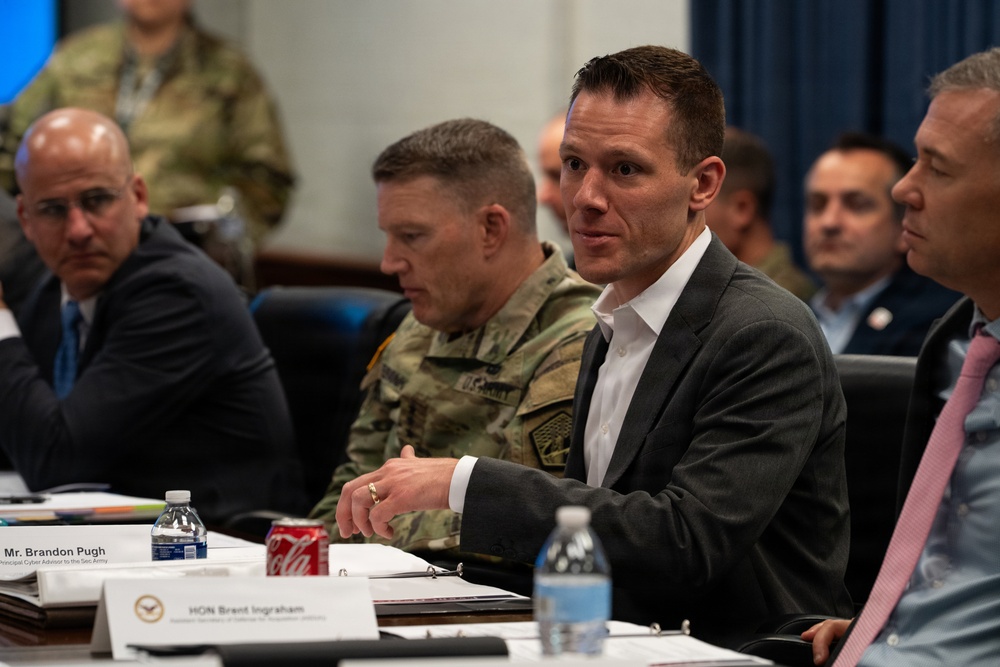
On April 27, 2026, the U.S. Army conducted the AI TTX 2.0 tabletop exercise at the Pentagon, gathering 14 senior cybersecurity executives from major tech firms to explore the use of artificial intelligence in cyber defense. The exercise simulated a future Indo-Pacific crisis where adversaries utilized AI to launch rapid, adaptive cyberattacks on Army networks. Participants included leaders from companies like Amazon Web Services, Google, and Microsoft, alongside Army officials. The focus was on identifying existing AI capabilities that could enhance cyber defense and address vulnerabilities in legacy systems. Secretary of the Army Dan Driscoll emphasized the need for faster delivery of capabilities through collaboration with industry. The exercise built on previous efforts, notably the inaugural AI TTX held in September 2025, which initiated Project ARIA aimed at implementing AI solutions across Army operations. Insights from the exercise highlighted the importance of balancing human and machine speeds in cyber defense.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…