 Scottishlegal
Arnold Clark Cyberattack: Long-lasting Impact and Calls for Legal Reform
Article Content

- •Arnold Clark was attacked by the Play ransomware gang in December 2022.
- •Sensitive customer data was leaked, leading to a potential group action lawsuit.
- •Calls for legal reforms aim to protect victims from ongoing exploitation of stolen data.
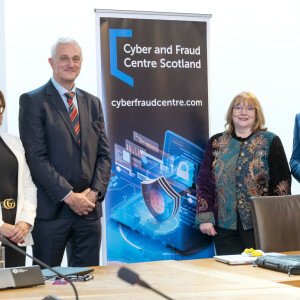
In December 2022, Arnold Clark, a major car retailer, suffered a cyberattack attributed to the Play ransomware gang, which resulted in the theft of sensitive customer data. The attack forced staff to revert to manual transaction recording as they were locked out of their systems. The stolen data, including personal identification and banking information, was leaked on the dark web, prompting a potential group action lawsuit from affected customers. Former CEO Eddie Hawthorne emphasized the ongoing repercussions of such attacks at a recent event, advocating for better support for businesses and legal reforms to protect victims. The Cyber and Fraud Centre - Scotland echoed these sentiments, highlighting the need for stronger protections against the exploitation of stolen data. The incident underscores the long-term risks associated with cybercrime, as stolen data can be traded and used for further fraudulent activities.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Play Ransomware Gang and Arnold Clark in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What data was stolen in the Arnold Clark attack?
What is the current status of the group action lawsuit?
What support is being called for post-attack?
Continue Reading
 Critical Zero-Day Exploits Target F5 and Check Point Products F5 Networks released emergency hotfixes for a critical zero-day vulnerability, CVE-2026-94127, in its BIG-IP Access Policy Manager on September 22, 2026, after confirming active exploitation. This flaw allows unauthenticated remote code execution (RCE) and has a CVSS score of 9.8. Concurrently, Check Point disclosed…
 Critical Citrix NetScaler Zero-Day Vulnerabilities Exploited Citrix disclosed two critical zero-day vulnerabilities, CVE-2026-88771 and CVE-2026-88772, affecting NetScaler ADC and Gateway systems, which are being actively exploited. Both vulnerabilities have a CVSS score of 9.5 and allow unauthenticated attackers to execute arbitrary commands remotely. CVE-2026-88771 arises…