 Ia.Acs.Au
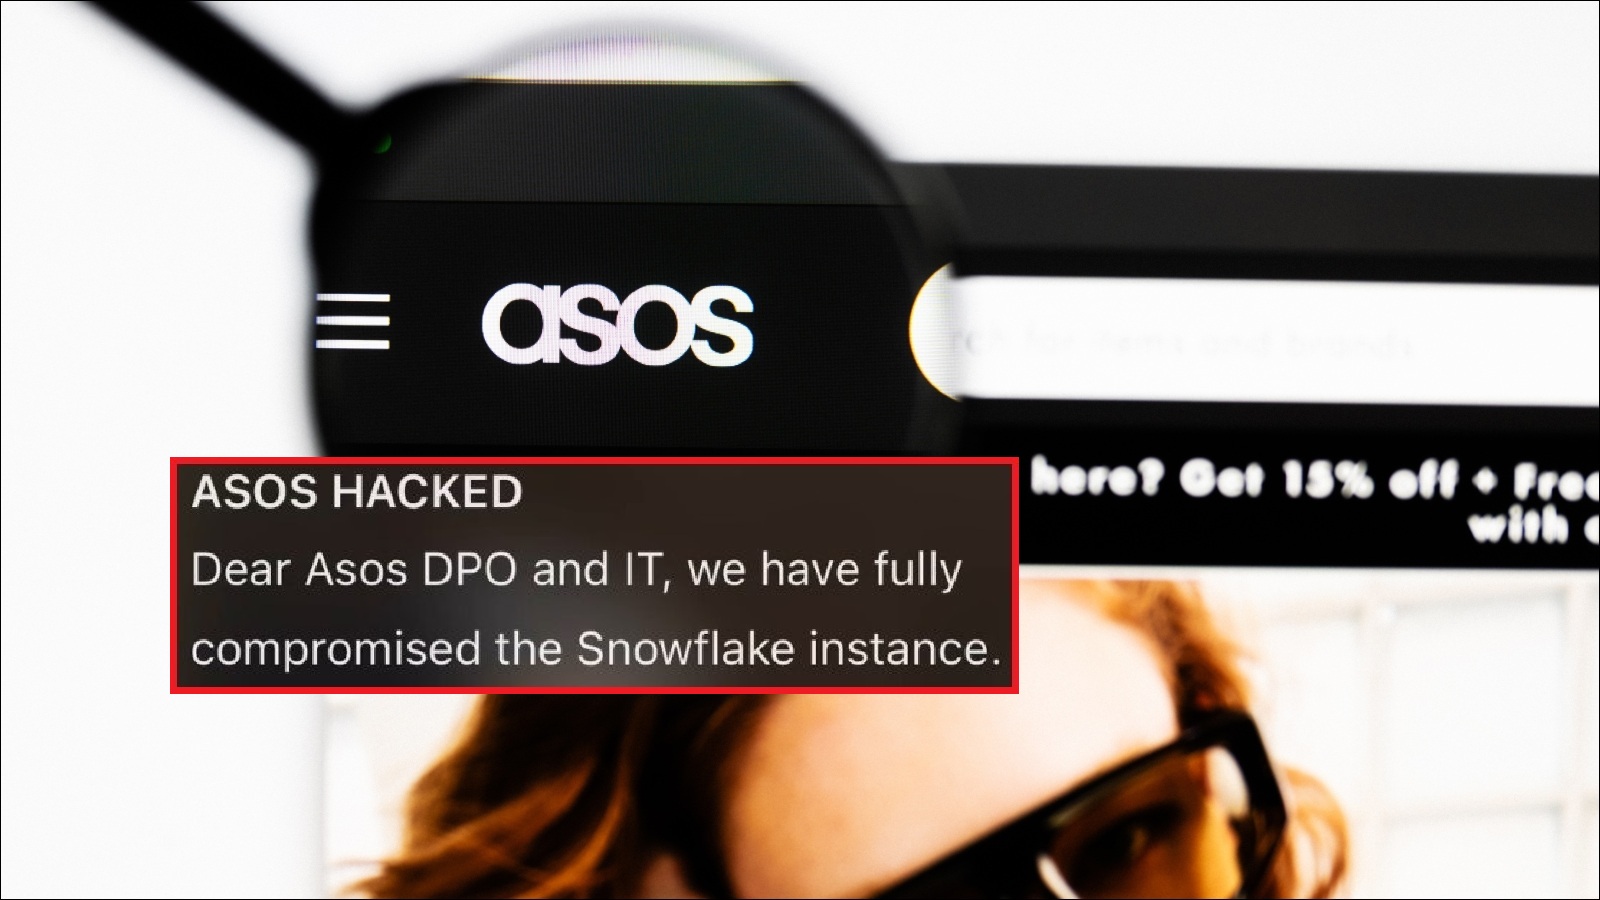
ASOS Hacked: Unauthorized Notification Sent to 17 Million Users
Article Content

- •ASOS was hacked, sending unauthorized notifications to 17 million users.
- •The breach involved basic personal information, but payment data was reportedly safe.
- •ASOS shares dropped 13% immediately following the incident.
On October 6, 2026, UK fashion retailer ASOS experienced a security breach when hackers exploited its notifications system, sending an alarming push notification to approximately 17 million users. The message claimed that the hackers had compromised ASOS's Snowflake instance and threatened to leak data unless the company engaged with them. ASOS's shares dropped by 13% following the incident, although the company stated that payment card data and passwords were not affected. Basic personal information may have been accessed, but the hackers reassured users that their data would remain safe for a designated period. The incident has raised concerns about ASOS's cybersecurity measures and its potential impact on customer trust and sales. ASOS is currently investigating the breach and has taken steps to restrict access to its notification platforms.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Following this threat?
Track ASOS in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What information was compromised?
How did the breach affect ASOS's stock?
What actions is ASOS taking in response?
Continue Reading
 Critical Citrix NetScaler Zero-Day Vulnerabilities Exploited In late September 2026, two critical zero-day vulnerabilities (CVE-2026-88771 and CVE-2026-88772) in Citrix NetScaler ADC and Gateway were actively exploited, allowing remote code execution. The Cybersecurity and Infrastructure Security Agency (CISA) added these CVEs to its Known Exploited Vulnerabilities catalog on…
 Critical Citrix NetScaler Vulnerabilities Actively Exploited in Finland The National Cyber Security Centre Finland (NCSC-FI) issued an alert regarding critical vulnerabilities in Citrix NetScaler ADC and Gateway products, specifically CVE-2026-88771 and CVE-2026-88772, which are being actively exploited in Finland. These vulnerabilities allow attackers to execute remote code without…