 www.theconstructionindex.co.uk
Aureos Acquires WhiteSpider to Enhance Cybersecurity for Critical Infrastructure
Article Content

- •Aureos has acquired WhiteSpider to enhance cybersecurity for critical infrastructure.
- •WhiteSpider brings expertise in AI, IT, and cyber security with over 40 specialists.
- •The integration aims to simplify compliance and operations for complex infrastructure projects.
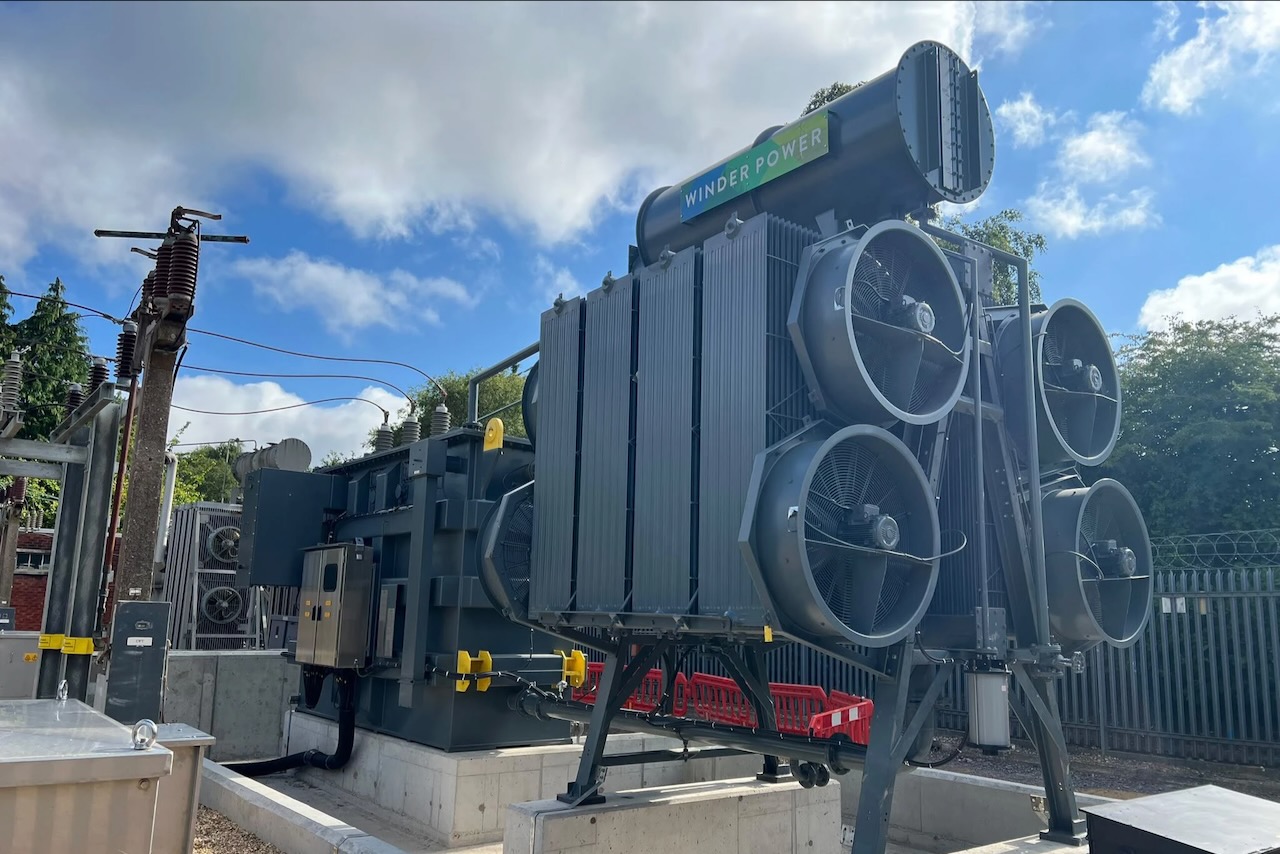
Aureos has acquired WhiteSpider, a specialist in AI and IT, to bolster cybersecurity and digital capabilities for critical infrastructure projects in the UK. The acquisition integrates WhiteSpider's expertise in enterprise networking, sovereign AI, and cloud solutions directly into Aureos's operations, simplifying contracts and compliance for infrastructure owners. WhiteSpider's team of over 40 professionals brings significant experience in cyber security, which is crucial for maintaining resilient operations in regulated environments. The deal aims to streamline operations for complex assets like substation transformer installations, where the integration of operational technology (OT) and information technology (IT) is vital. This move positions Aureos as a key player in the UK market for integrated civil-digital delivery, particularly in sectors like rail infrastructure. The acquisition is expected to enhance Aureos's existing contracts and capabilities in the UK rail sector, particularly with its involvement in the HS2 project.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 Critical Zero-Day Exploits Target F5 and Check Point Products F5 Networks released emergency hotfixes for a critical zero-day vulnerability, CVE-2026-94127, in its BIG-IP Access Policy Manager on September 22, 2026, after confirming active exploitation. This flaw allows unauthenticated remote code execution (RCE) and has a CVSS score of 9.8. Concurrently, Check Point disclosed…
 Critical Citrix NetScaler Zero-Day Vulnerabilities Exploited Citrix disclosed two critical zero-day vulnerabilities, CVE-2026-88771 and CVE-2026-88772, affecting NetScaler ADC and Gateway systems, which are being actively exploited. Both vulnerabilities have a CVSS score of 9.5 and allow unauthenticated attackers to execute arbitrary commands remotely. CVE-2026-88771 arises…