Article Content

- •A British Airways flight encountered a drone shortly after takeoff from Heathrow.
- •The drone was reported to be moving very fast and was classified as an unknown object.
- •The UK Airprox Board rated the incident as an A-grade risk, indicating a serious potential for collision.
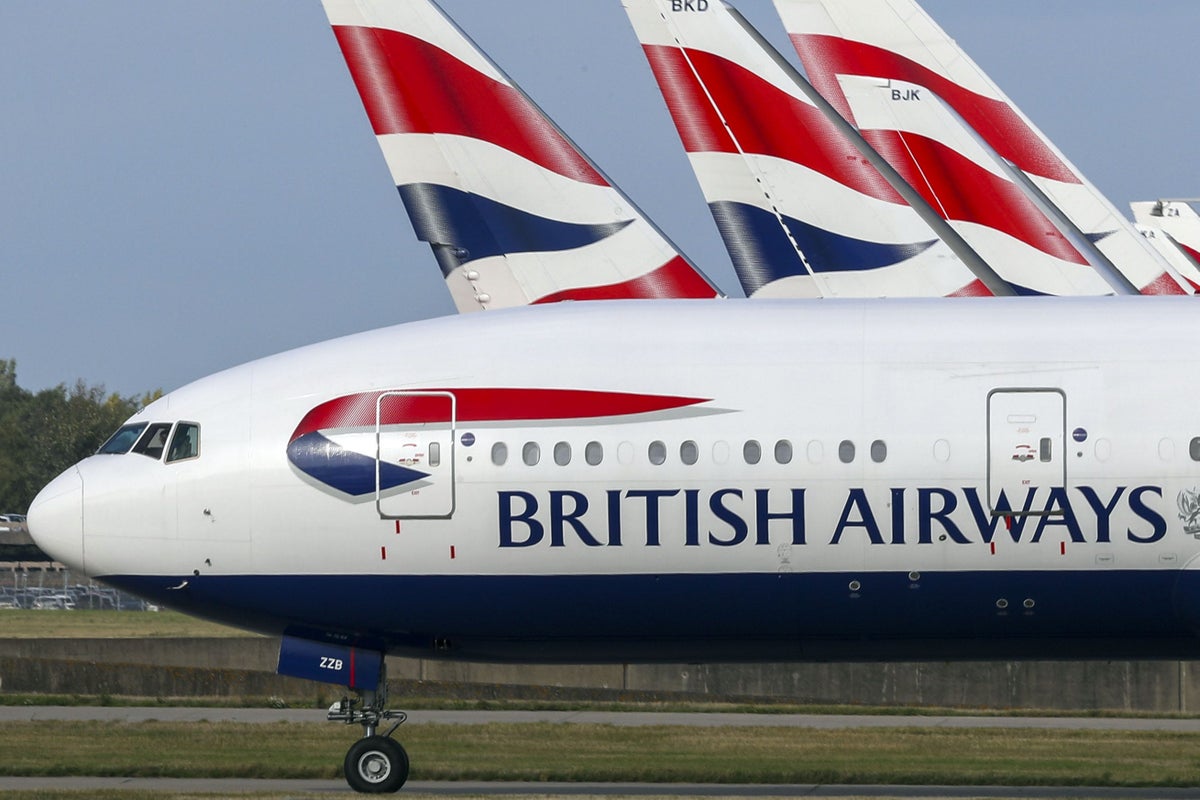
A British Airways flight narrowly avoided a drone described as 'the size of four toasters' shortly after takeoff from Heathrow Airport on June 24. The incident occurred at 12:08 PM when the drone flew 50 feet above the aircraft's right wing at an altitude of 6,000 feet. The pilot reported the encounter to air traffic control, but no evasive action was necessary, and the flight continued to its destination without incident. The UK Airprox Board classified the object as an unknown entity and rated the incident as an A-grade risk, indicating a potential for catastrophic outcomes. British Airways emphasized the seriousness of such incidents and the importance of reporting them to authorities for investigation. This year, nearly 90 UFO sightings have been recorded in the UK, with many attributed to misidentified objects. The Ministry of Defence previously operated a UFO desk, which was closed in 2009 due to budget cuts.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track British Airways in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What was the size of the drone?
Did the flight take any evasive action?
What is the significance of the A-grade risk classification?
Continue Reading
 .NET Vulnerability CVE-2026-111497 Requires Immediate Action On October 25, 2026, Microsoft released out-of-band security updates for.NET addressing CVE-2026-111497, a vulnerability in the Brotli decompression algorithm that allows unauthorized attackers to elevate privileges over a network. The flaw affects.NET versions 8, 9, 10, and 11, particularly in applications that…
 Critical BeyondTrust 9.3 Vulnerability Actively Exploited by Threat Actor A critical vulnerability (CVE-2026-102764) in BeyondTrust Remote Support has been discovered and is actively being exploited by the threat group ARMORY CASTLE, reportedly linked to China. The vulnerability, which has a CVSS score of 9.3, allows unauthenticated attackers to upload files and potentially compromise host…