 www.janes.com
Bahrain Joins US-Led Falcon Strike Drone Task Force
Article Content

- •Bahrain is the first regional nation to join Task Force Falcon Strike.
- •The task force focuses on one-way attack drones and is part of a broader US military strategy.
- •Bahrain's commitment includes purchasing additional US military equipment.
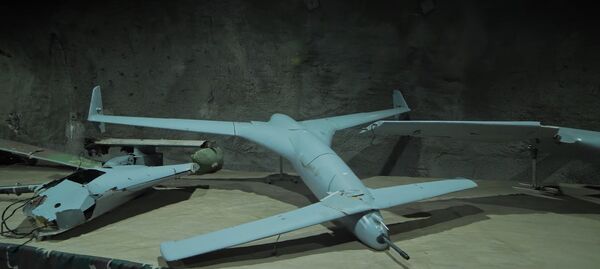
Bahrain has officially joined the US Central Command's Task Force Falcon Strike, the first multinational unit focused on one-way attack drones. This commitment was announced by the US Embassy in Manama on September 25, 2026, following discussions between US and Bahraini defense officials. Bahrain's participation includes plans to procure additional US munitions and air defense systems. The establishment of Falcon Strike was first announced by CENTCOM on August 14, 2026, aiming to enhance regional security amid increasing tensions with Iran. The task force will build on the capabilities of Task Force Scorpion Strike, which was created in December 2025. Bahrain's integration comes at a time of heightened US military presence in the region, particularly around Iran, where CENTCOM has reported significant naval operations. The US military's strategy emphasizes collaboration with regional partners to strengthen defense capabilities against potential threats.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What is Task Force Falcon Strike?
Why is Bahrain joining this task force?
What military equipment will Bahrain acquire?
Continue Reading
 Citrix NetScaler Critical Vulnerabilities Exploited: Urgent Patching Required Citrix NetScaler ADC and Gateway products are affected by critical vulnerabilities CVE-2026-88771 and CVE-2026-88772, both assigned a CVSS score of 9.5. The Cybersecurity and Infrastructure Security Agency (CISA) added these CVEs to its Known Exploited Vulnerabilities catalog on September 27, 2026, and mandated…
 Critical Zero-Day Exploits Target F5 and Check Point Products F5 Networks released emergency hotfixes for a critical zero-day vulnerability, CVE-2026-94127, in its BIG-IP Access Policy Manager on September 22, 2026, after confirming active exploitation. This flaw allows unauthenticated remote code execution (RCE) and has a CVSS score of 9.8. Concurrently, Check Point disclosed…