 Thefinancialexpress.Bd
Bangladesh and Singapore Enhance Cybersecurity Cooperation
Article Content

- •Bangladesh and Singapore committed to enhancing police reform and cybersecurity cooperation.
- •Singapore will provide technological support and training to Bangladesh's law enforcement agencies.
- •A proposal for a Mutual Legal Assistance agreement was sent from Bangladesh to Singapore in February 2024.
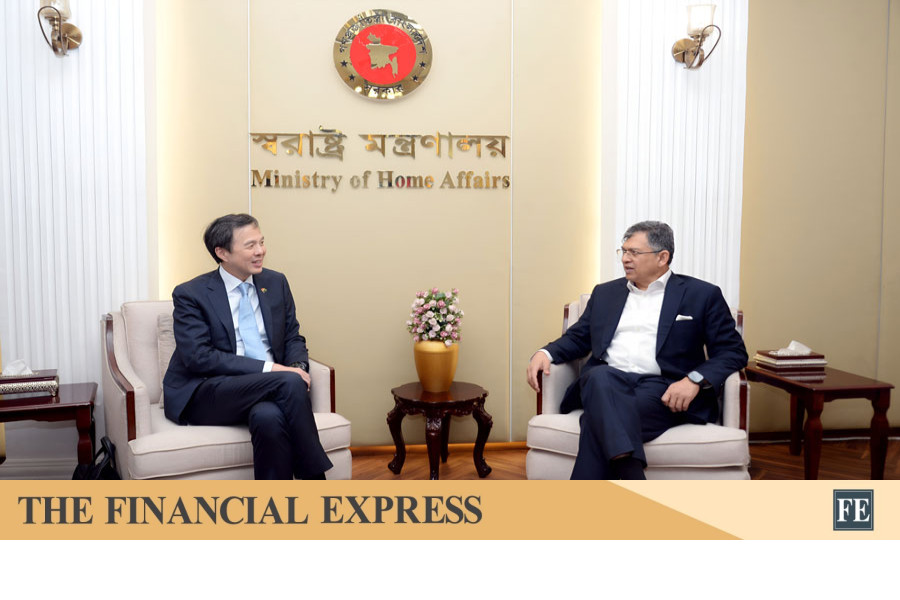
On May 18, 2026, Bangladesh and Singapore reaffirmed their commitment to strengthen cooperation in police reform and cybersecurity. During a meeting between Minister Salahuddin Ahmed and Singapore's Non-Resident High Commissioner Derek Loh, discussions focused on enhancing the professional training and capacity of the Bangladesh Police. The two nations emphasized the need for real-time information sharing to combat transnational terrorism and cyber threats, including online scams and phishing. Singapore is prepared to provide technological support and training, proposing to send a delegation of Bangladeshi police officers for specialized training. Bangladesh has also proposed a Mutual Legal Assistance agreement to facilitate legal cooperation in criminal matters. Both countries expressed a desire to expand trade and investment opportunities. The partnership aims to bolster law enforcement capabilities and address growing cybersecurity challenges.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (5)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…