 Newswav
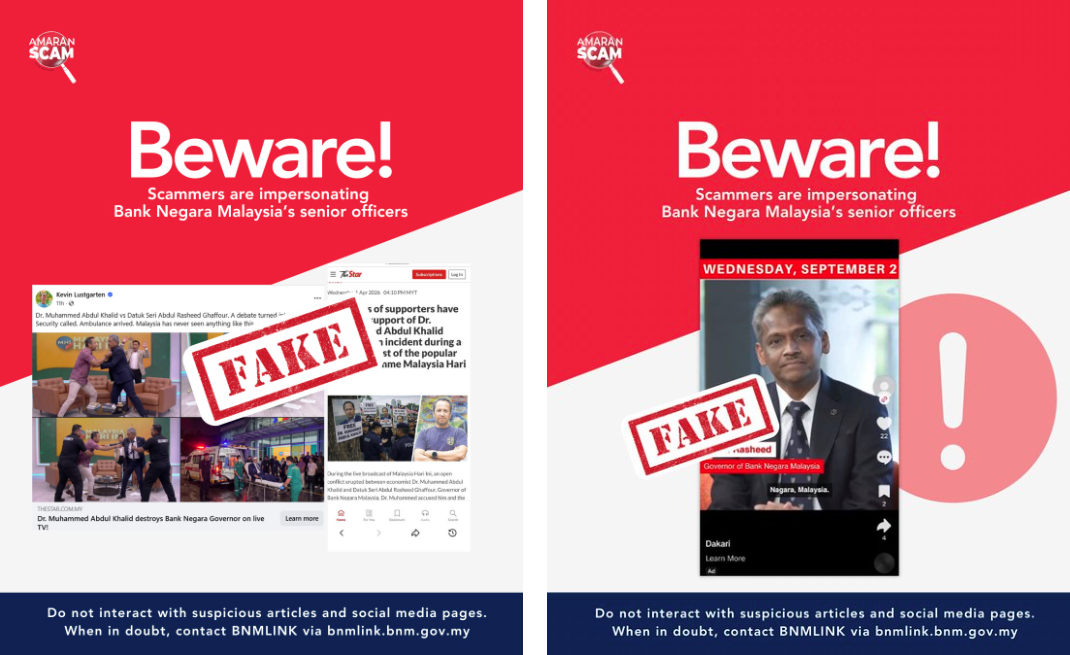
BNM and SC Warn Public of Deepfake Investment Scams
Article Content

- •BNM and SC warn against deepfake videos impersonating senior officials.
- •Public urged to verify investment schemes through official channels.
- •No endorsement of private investment schemes by BNM or SC.
Bank Negara Malaysia (BNM) and the Securities Commission Malaysia (SC) have issued a warning about deepfake videos impersonating senior officials to promote fraudulent investment schemes. The authorities emphasized that neither BNM nor SC endorses private investment schemes and urged the public to verify suspicious content through official channels. Individuals are advised to check BNM's Financial Consumer Alert List and SC's Investor Alert List for flagged entities. BNM has provided examples of deepfake content on its verification page and encouraged reporting of suspicious materials to relevant social media platforms. The warning aims to protect the public from falling victim to scams that exploit the identities of influential figures in finance. The situation is ongoing, with no specific incidents of exploitation reported in the articles.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (7)
Following this threat?
Track Bank Negara Malaysia in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
How can I verify if an investment scheme is legitimate?
What should I do if I encounter a suspicious video?
Are there any specific examples of deepfake scams?
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…