 www.bimco.org
BIMCO Discusses Cybersecurity Amid Regional Maritime Threats
Article Content

- •BIMCO addressed regional maritime security issues during recent committee meetings.
- •Cybersecurity is increasingly recognized as critical in maritime operations.
- •Discussions included implications of conflicts and attacks on shipping.
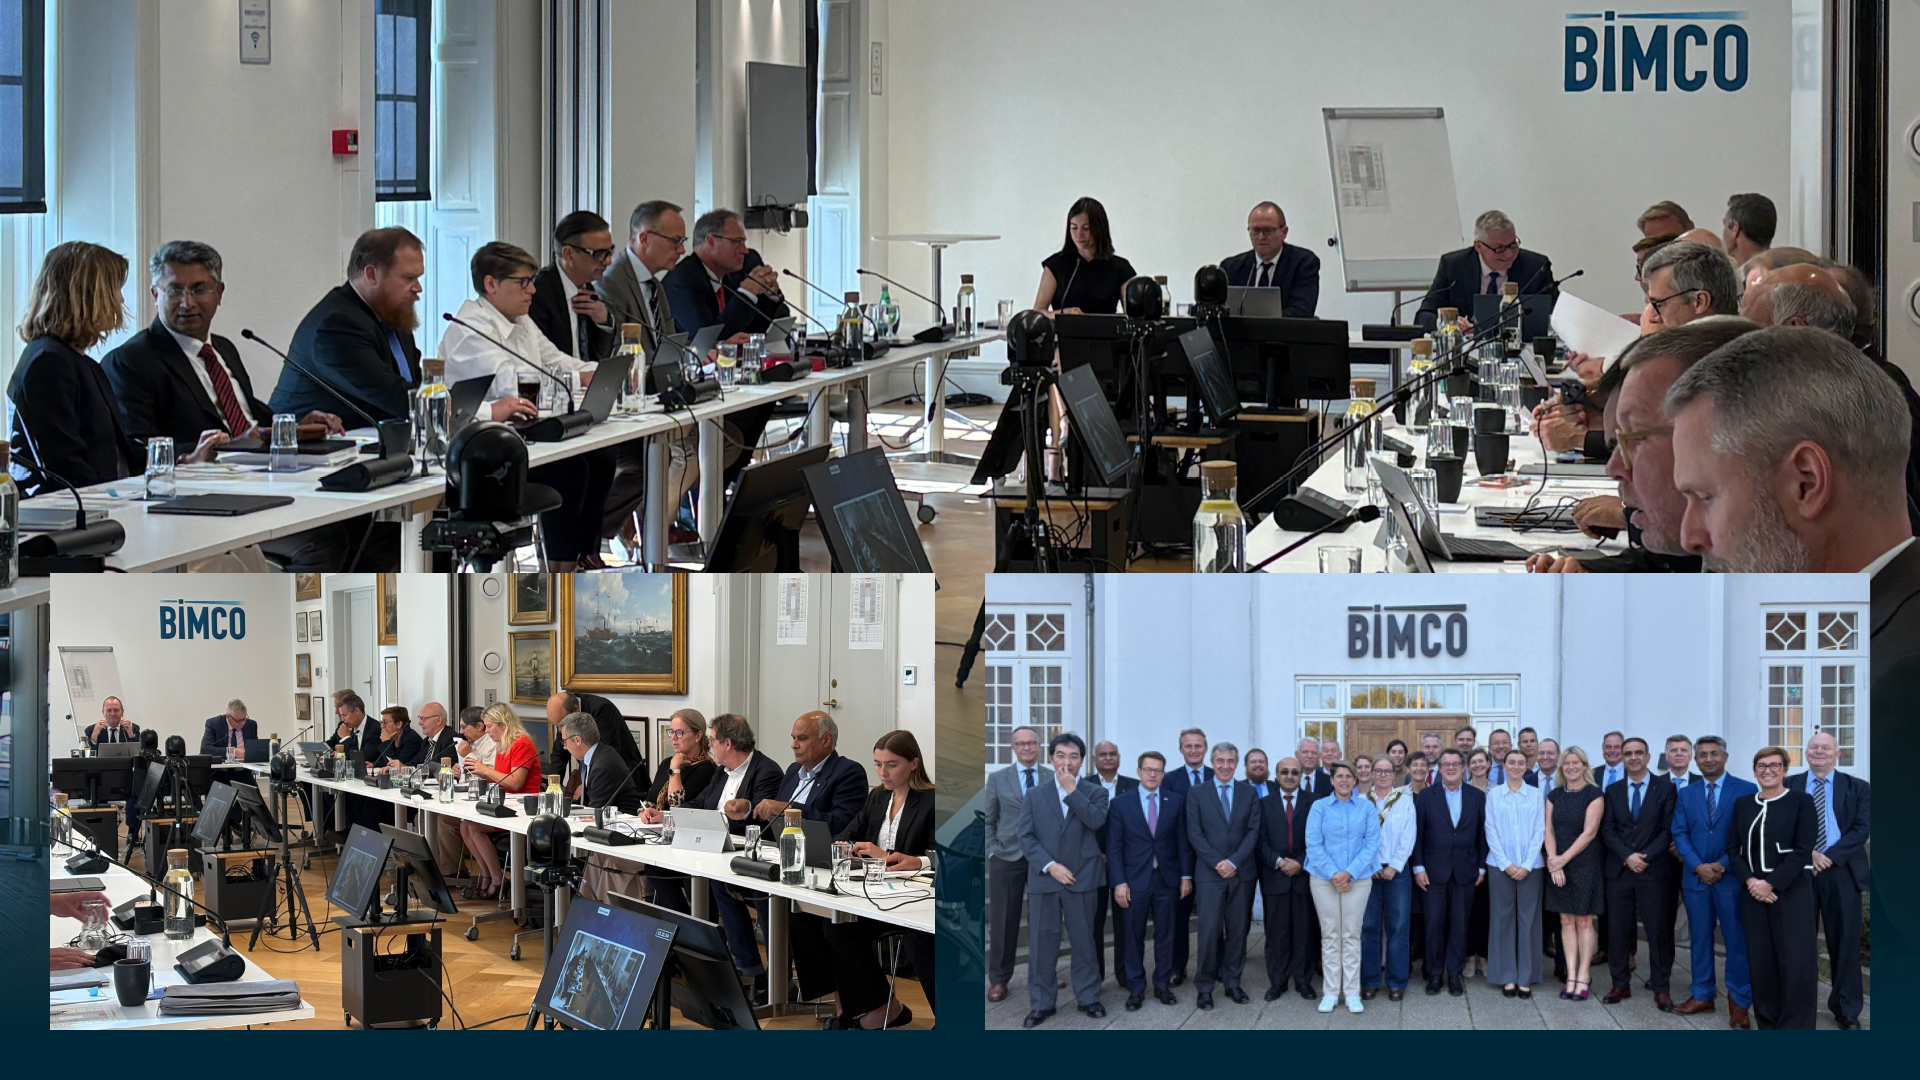
During meetings on September 30 and October 1, BIMCO's Maritime Safety & Security Committee and Marine Environment Committee addressed the security situation in the Strait of Hormuz and surrounding seas. They focused on implications of regional conflicts, attacks on shipping, and navigational disruptions. The discussions highlighted the growing importance of cybersecurity as digitalization in maritime operations increases. Other topics included the safe adoption of alternative fuels and environmental regulations affecting shipping operations. The committees aim to shape BIMCO's positions in discussions with the IMO and other regulatory bodies. No specific cyber incidents or vulnerabilities were reported in the articles, but the emphasis on cybersecurity indicates a recognition of potential threats in maritime operations.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What specific cybersecurity threats were discussed?
How does this affect shipping companies?
What actions should be taken regarding cybersecurity?
Continue Reading
 Citrix NetScaler Critical Vulnerabilities Exploited: Urgent Patching Required Citrix NetScaler ADC and Gateway products are affected by critical vulnerabilities CVE-2026-88771 and CVE-2026-88772, both assigned a CVSS score of 9.5. The Cybersecurity and Infrastructure Security Agency (CISA) added these CVEs to its Known Exploited Vulnerabilities catalog on September 27, 2026, and mandated…
 Critical Citrix NetScaler Zero-Day Vulnerabilities Exploited Citrix disclosed two critical zero-day vulnerabilities, CVE-2026-88771 and CVE-2026-88772, affecting NetScaler ADC and Gateway systems, which are being actively exploited. Both vulnerabilities have a CVSS score of 9.5 and allow unauthenticated attackers to execute arbitrary commands remotely. CVE-2026-88771 arises…