 App.Santiment
Coldcard Firmware Exploit Causes Historic Drop in Bitcoin Sentiment
Article Content

- •The Coldcard exploit drained approximately 1,082 BTC, valued at $70 million.
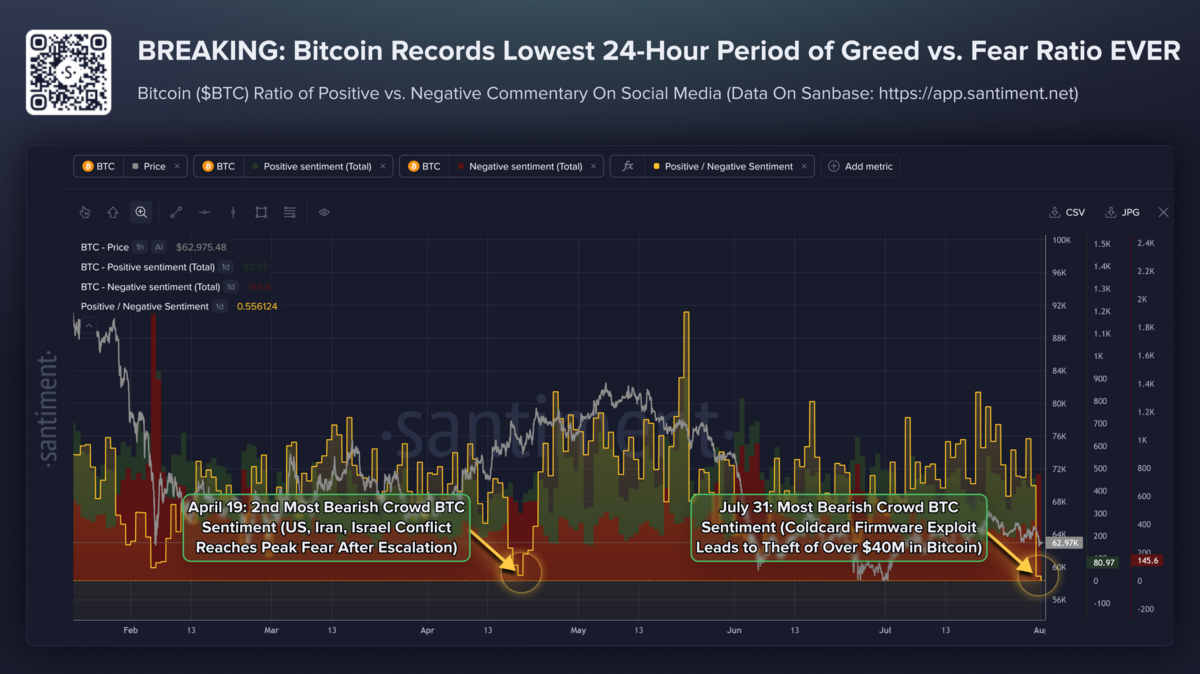
- •Bitcoin's positive-to-negative commentary ratio fell to 0.58 bullish for every 1.00 bearish remark.
- •The exploit raises concerns about the security of cold storage solutions for cryptocurrencies.
A Coldcard firmware exploit has led to a significant decline in Bitcoin's social sentiment, marking the lowest positive-to-negative commentary ratio since tracking began. The exploit drained approximately 1,082 BTC (around $70 million) from nearly 1,200 self-custody wallets. This incident challenges the long-held belief that cold storage is a secure option for cryptocurrency holders. The exploit was traced back to a firmware build error present since version 4.0.0, released in March 2021. Following the exploit, Bitcoin's positive commentary ratio fell to just 0.58 bullish remarks for every 1.00 bearish remark. Despite the exploit, Bitcoin's price has remained relatively stable around $63,000. The incident has sparked discussions about the vulnerabilities of hardware wallets and the need for increased scrutiny of self-custody solutions. Market reactions are being closely monitored, with potential shifts in on-chain activity expected in the coming days.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Following this threat?
Track Coinkite in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical RCE Vulnerability in Prefab UI Disclosed A critical remote code execution vulnerability, CVE-2026-120338, was disclosed on November 1, 2026, affecting Prefab UI's Generative UI sandbox. The flaw allows attackers to execute arbitrary Python code by exploiting Deno's permissions, enabling file read/write access on the host server. This vulnerability affects…
 Chinese Actor Compromises US Government Networks via PHP2Shell Exploit A suspected Chinese nation-state actor exploited vulnerabilities in Palo Alto Networks firewalls using a chained PHP2Shell exploit and a Linux kernel privilege escalation flaw. The attack, which began on October 23, targeted 25 servers across the US, Japan, Taiwan, and South Korea, with a focus on US…