 Coindesk
Bitget Hackers Transfer $3.9M in ZEC to Zcash's Shielded Pool
Article Content

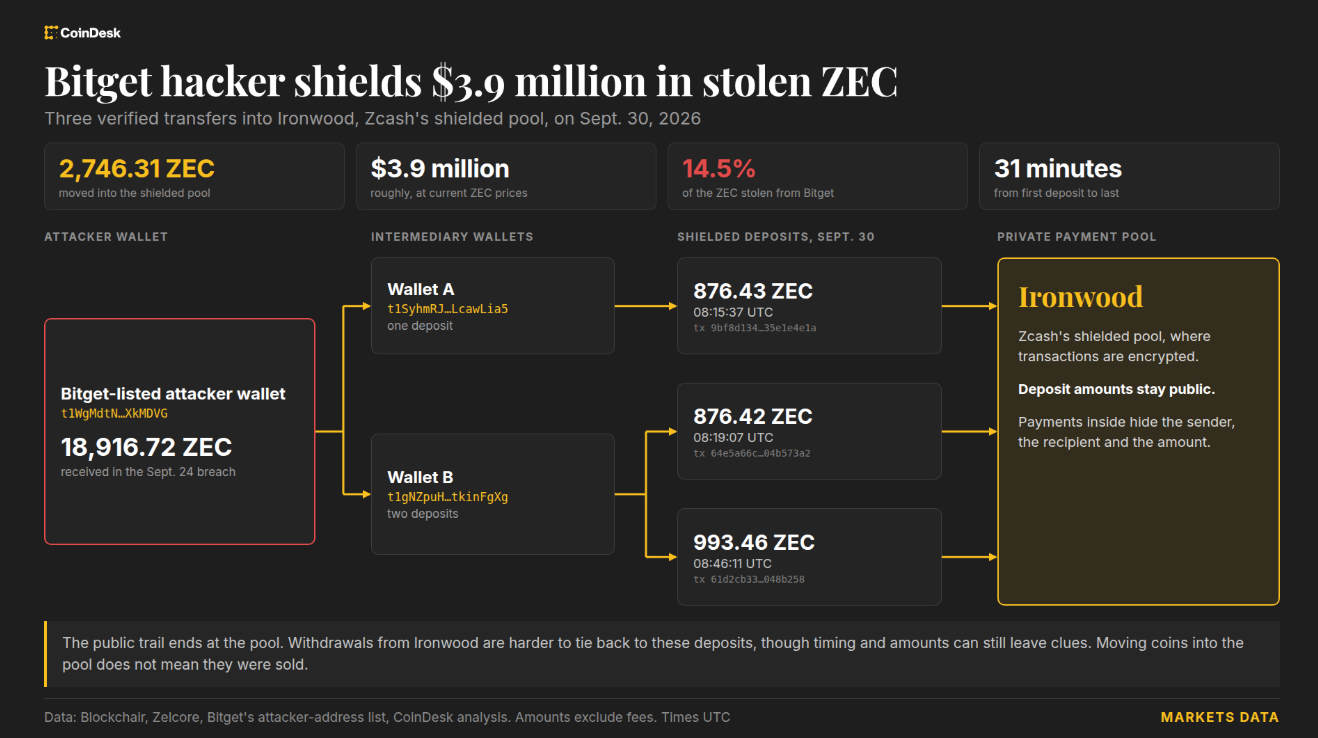
- •Hackers moved $3.9 million in ZEC into Zcash's Ironwood shielded pool.
- •The transfer obscures the trail of stolen funds from the Bitget breach.
- •Investigators can track entry and exit points but lack a complete transaction trail.
On September 30, 2026, wallets linked to the Bitget hack transferred $3.9 million in ZEC into Zcash's Ironwood shielded pool, obscuring the funds' trail. This movement represents 15% of the total ZEC stolen during a breach on September 24, which was initially reported as $387.5 million. The funds were sent in three transfers between 08:15 and 08:46 UTC, passing through two intermediary addresses tied to the attacker. While investigators can see the amounts entering Ironwood, the sender, recipient, and amounts are hidden within the shielded pool. If the funds later return to a public address, the outgoing amounts will become visible again, allowing for some tracking. The breach has raised concerns about the recovery of the stolen funds, as the shift to Zcash complicates the investigation. No official statements from Zcash, law enforcement, or Bitget's recovery team regarding the shielded transfers were reported.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Bitget in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
How much was stolen in the Bitget hack?
What is Zcash's Ironwood shielded pool?
Can investigators track the stolen funds?
Continue Reading
 Critical Zero-Day Exploits Target F5 and Check Point Products F5 Networks released emergency hotfixes for a critical zero-day vulnerability, CVE-2026-94127, in its BIG-IP Access Policy Manager on September 22, 2026, after confirming active exploitation. This flaw allows unauthenticated remote code execution (RCE) and has a CVSS score of 9.8. Concurrently, Check Point disclosed…
 Critical Citrix NetScaler Zero-Day Vulnerabilities Exploited Citrix disclosed two critical zero-day vulnerabilities, CVE-2026-88771 and CVE-2026-88772, affecting NetScaler ADC and Gateway systems, which are being actively exploited. Both vulnerabilities have a CVSS score of 9.5 and allow unauthenticated attackers to execute arbitrary commands remotely. CVE-2026-88771 arises…