 bitquery.io
Bloom Trading Bot Hack Results in $953K Theft in Under Two Minutes
Article Content

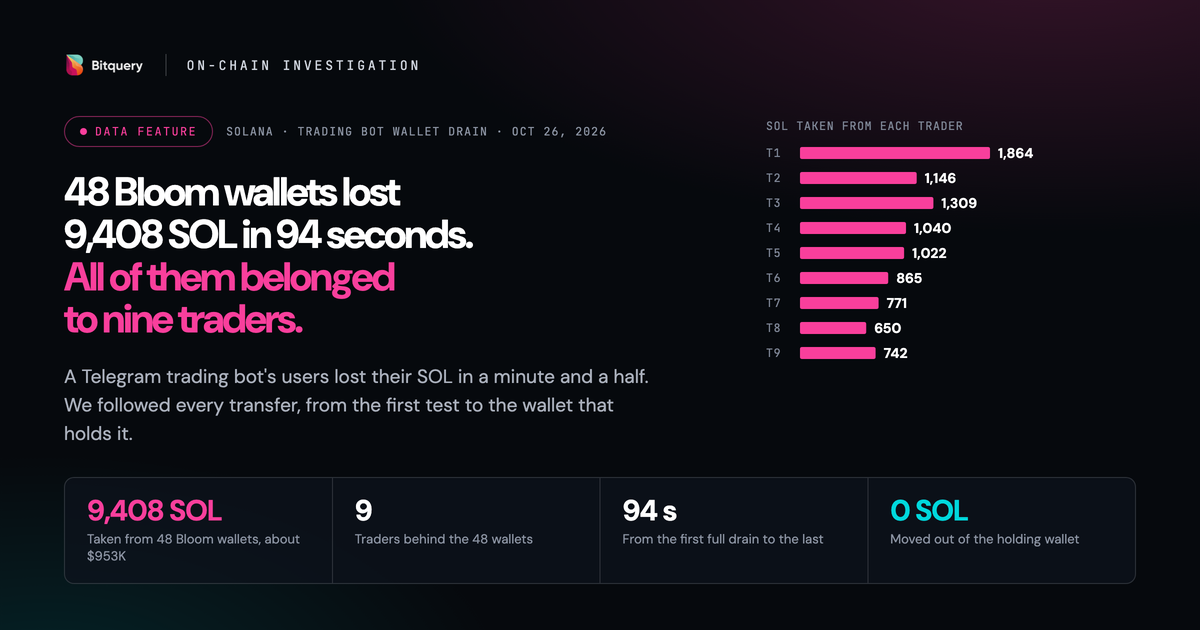
- •Hackers stole $953,000 from 48 wallets in 94 seconds using the Bloom trading bot.
- •The attack exploited a remote code execution vulnerability in a third-party module.
- •Bloom has committed to fully reimburse the affected traders.
Hackers drained $953,000 from 48 wallets linked to the Bloom Telegram trading bot in just 94 seconds on October 26, 2026. The attack targeted nine traders, with the hackers exploiting a remote code execution vulnerability in a third-party module. Each wallet's private key was used to authorize the transactions, indicating that the attacker had access to the keys. Notably, some of the drained wallets had been inactive for months. Bloom has pledged to reimburse all affected traders in full and stated that no private keys were compromised. This incident follows previous attacks on Telegram trading bot users, highlighting ongoing security risks in the sector.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Following this threat?
Track Bloom in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
How did the hackers access the wallets?
What steps is Bloom taking after the hack?
Have the stolen funds been recovered?
Continue Reading
 PHP2Shell Vulnerabilities Exploited by AI-Driven Attackers Threat actors have exploited PHP2Shell vulnerabilities (CVE-2026-109618 and CVE-2026-109619) to target a government entity in Europe, gaining access to sensitive data within two hours of the initial breach. The attackers utilized AI tools for reconnaissance and post-exploitation activities, including accessing…
 Lazarus APT Launches Operation FlashHole Using AI and Post-Quantum Cryptography Kaspersky has identified a cyberespionage campaign, dubbed Operation FlashHole, attributed to the Lazarus APT group, active since July 2025. The campaign has targeted at least three organizations in South Korea's construction, software, and wire-communication sectors. Attack methods include spear-phishing emails…