 Recordedfuture
BlueDelta Espionage Campaign Using HOOKEDGE Targets European Governments
Article Content

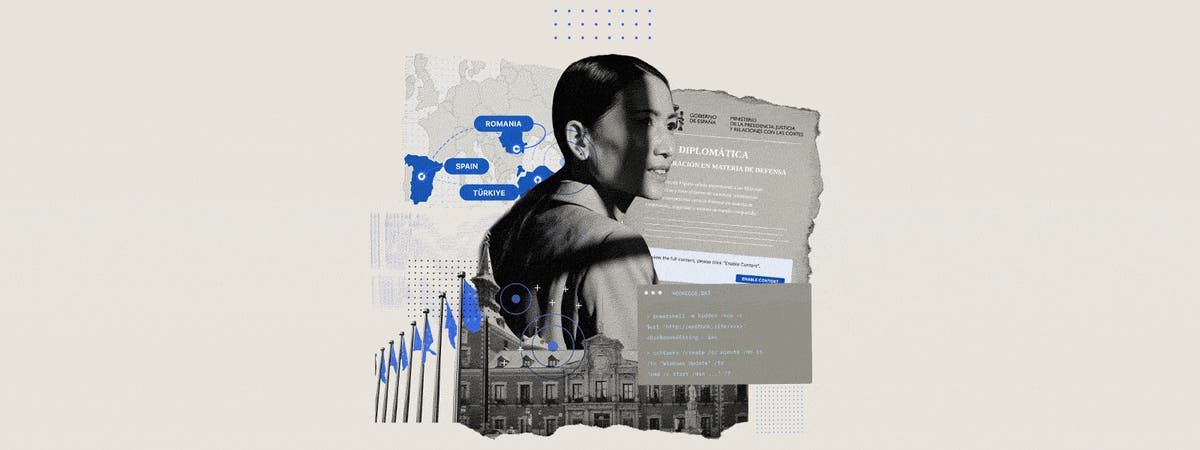
- •BlueDelta targets government and diplomatic sectors in Romania, Spain, and Türkiye.
- •HOOKEDGE backdoor is delivered via macro-enabled Word documents using legitimate lures.
- •Organizations should block macros from internet documents and enhance detection measures.
BlueDelta, a Russian state-linked threat actor, has conducted a series of espionage campaigns targeting government and diplomatic organizations in Romania, Spain, and Türkiye from late September 2025 to early April 2026. The campaigns utilized a lightweight Windows backdoor named HOOKEDGE, delivered through macro-enabled Microsoft Word documents that impersonated legitimate diplomatic communications. The backdoor exploits legitimate webhook services for command-and-control operations, allowing it to blend in with normal network traffic. The attacks are characterized by continuous refinement of the HOOKEDGE implant to evade detection and adapt to changes in defensive measures. BlueDelta has a history of targeting defense and policy-related organizations, reinforcing its focus on intelligence collection against European entities. Organizations are advised to block macro execution from internet-originated documents and enhance detection capabilities for specific behaviors associated with the malware. The current status indicates ongoing activity from BlueDelta with no signs of cessation.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (5)
Following this threat?
Track APT28 and Headlace in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Cyber Espionage Escalates in Europe Amid Geopolitical Tensions Cyberattacks on the public sector have surged by 114% in Europe over the past 30 months, with an average of 2,563 attacks per week per organization. This increase is attributed to rising geopolitical tensions, particularly related to the ongoing conflict between Russia and Ukraine. Check Point Research reports that…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…