 www.eurointegration.com.ua
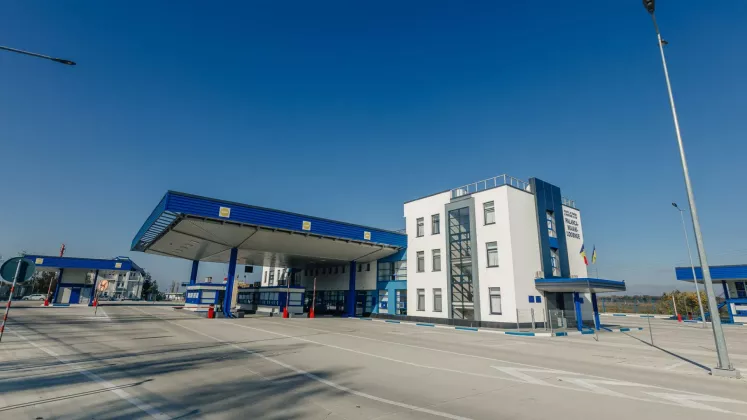
Border Crossing Operations Halted After Projectile Strikes Bus
Article Content

- •A projectile struck a bus and border booth at the Palanca–Maiaky–Udobne crossing.
- •Traffic is redirected to the Tudora border crossing due to the incident.
- •Authorities advise the public to avoid the area and take shelter during explosions.
Operations at the Palanca–Maiaky–Udobne border crossing between Ukraine and Moldova were suspended following an incident where a projectile, fired during Russian attacks on Ukrainian infrastructure, ricocheted and struck a passenger bus and a border control booth. The bus was damaged, and a border guard sustained minor injuries. Traffic from the junction of the R-30 and R-31 roads in the Ștefan Vodă district towards Palanca is temporarily suspended while an investigation is conducted. Patrol officers are redirecting traffic to the Tudora border crossing, and drivers are advised to avoid the area. Moldova's Border Police reported that the incident occurred at approximately 09:38 on 5 October. Authorities are monitoring the situation and have urged people to refrain from traveling to the area, advising them to take shelter indoors if they hear drones or explosions. Additionally, they warned against approaching debris from aircraft or ammunition and instructed to call emergency services if found. The national airspace monitoring system detected several unmanned aerial vehicles on 3 October.
Ask AI about this cluster
Answers cite the sources they use
More articles in this cluster (2)
Common questions
What caused the border crossing suspension?
What should travelers do now?
Are there any injuries reported?
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…