 www.pcrisk.com
Browser Guardian Adware: Privacy Risks and Removal Guidance
Article Content

- •Browser Guardian is categorized as adware and potentially unwanted software.
- •It tracks user browsing activity, posing privacy risks and potential identity theft.
- •Removal is advised due to its deceptive installation methods and ad injection.
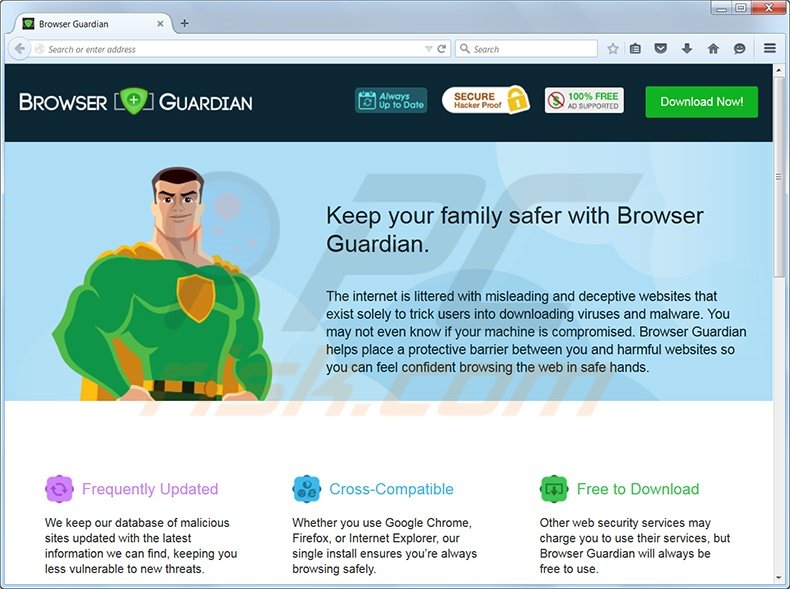
Browser Guardian is identified as adware that misleads users by claiming to protect against harmful sites while instead injecting ads into web pages. It is categorized as a potentially unwanted application and is often installed without user consent through deceptive software bundling. The adware tracks users' browsing activities, which can lead to privacy issues and identity theft. Users are advised to remove it from browsers like Chrome, Edge, and Firefox. The adware is distributed via freeware downloads and fake software updates. Current samples of Browser Guardian were first recorded in 2014, but there is no active distribution confirmed as of October 2026. The absence of a dedicated website or domain complicates the verification of its current status.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (5)
Common questions
How does Browser Guardian install on my system?
What are the privacy risks associated with Browser Guardian?
How can I remove Browser Guardian?
Continue Reading
 China-Linked Hackers Exploit PHP2Shell to Root 25 Servers Cybersecurity firm Dream reported that a China-linked threat actor exploited PHP2Shell vulnerabilities (CVE-2026-109618 and CVE-2026-109619) and a Linux kernel privilege escalation flaw (CVE-2026-46300) to gain root access to 25 servers, including three in a U.S. government-affiliated environment. The attackers used…
 Brotli Decoder Vulnerability Patched Across Multiple Linux Distributions A vulnerability, CVE-2026-111497, affecting the Brotli decoder has been patched in various Linux distributions, including Fedora 44 and Oracle Linux 10. The flaw allows for an out-of-bounds write, which could potentially enable attackers to execute arbitrary code. The vulnerability was published on October 22, 2026…