 Markets.Businessinsider
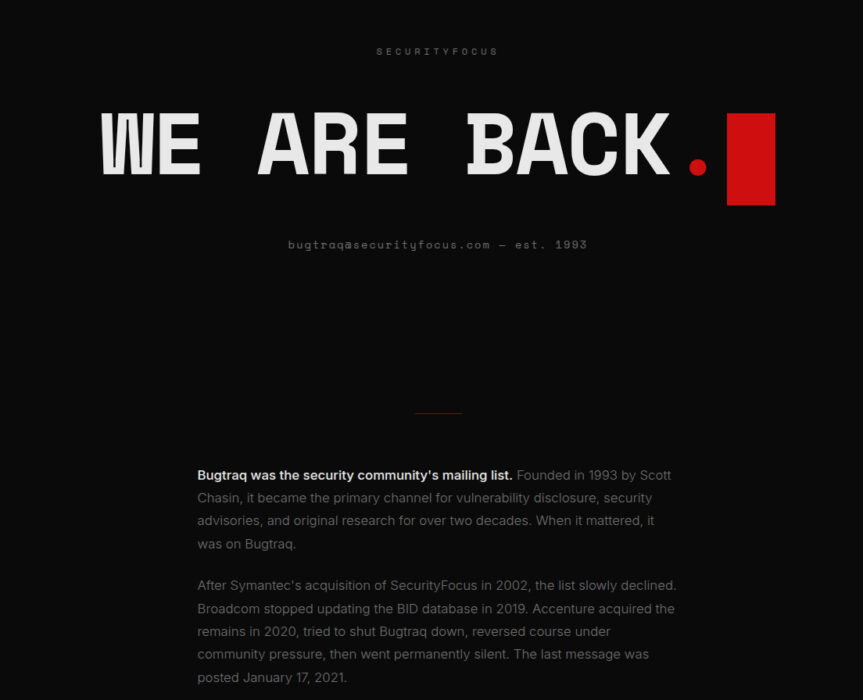
Bugtraq Mailing List Relaunches to Support Cybersecurity Community
Article Content

- •Bugtraq, a key cybersecurity mailing list, has been relaunched for community use.
- •The list aims to provide a free, moderated platform for vulnerability discussions.
- •Security researcher Jonathan Brossard encourages community involvement in shaping Bugtraq's future.
On August 7, 2026, at DEF CON 34 in Las Vegas, security researcher Jonathan Brossard announced the relaunch of the Bugtraq mailing list, originally established in 1993. This list serves as a platform for discussing cybersecurity vulnerabilities and techniques, with over 120,000 references in the NVD/CVE database. Bugtraq aims to counteract the decline of quality cybersecurity information amidst social media and paywalls. It is open to all security researchers without any commercial agenda. The relaunch includes two lists: the original Bugtraq mailing list and a new list focused on AI research. Brossard emphasized the community's role in shaping the platform's future. DEF CON founder Jeff Moss expressed support for the initiative, highlighting the importance of vulnerability ownership. The list is independently operated and hosted at securityfocus.com.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…