 bnrnews.bg
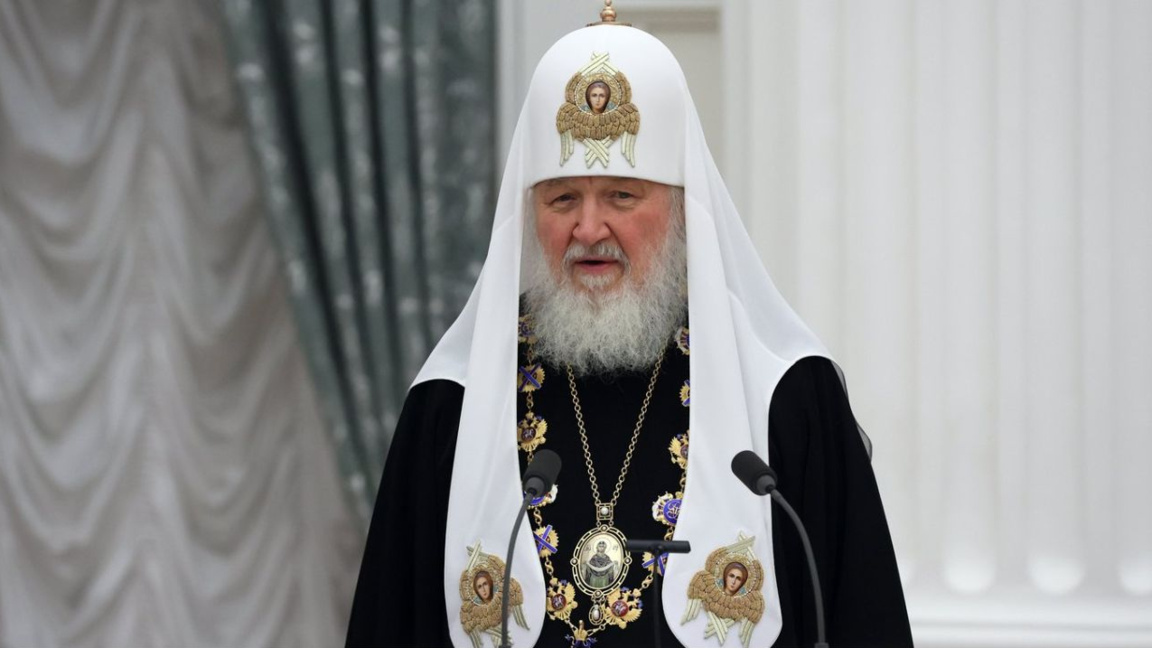
Bulgaria Opposes EU Sanctions Targeting Patriarch Kirill Amid Ongoing Tensions
Article Content

- •Bulgaria opposes EU sanctions against Patriarch Kirill, viewing it as religious interference.
- •The EU's 21st sanctions package was proposed on June 9, 2026, and targets Kirill due to his support for the war in Ukraine.
- •Only one Bulgarian metropolitan has publicly condemned Russian actions, highlighting internal divisions.
Bulgaria has expressed opposition to the European Union's proposed 21st sanctions package against Russia, specifically regarding the inclusion of Russian Orthodox Patriarch Kirill on the sanctions list. This decision, reported on June 17, 2026, stems from Bulgaria's view that such sanctions interfere with religious affairs. The European Commission proposed these sanctions on June 9, citing Kirill's vocal support for the war in Ukraine as the primary reason for his inclusion. The sanctions package is expected to be adopted by the end of July 2026. Bulgarian religious leaders are divided on this issue, with only Metropolitan Naum of Ruse publicly supporting the condemnation of Russian aggression. Kirill has framed dissent against state policies as treasonous, further complicating the geopolitical landscape. The situation reflects broader tensions within the EU regarding how to handle Russia and its religious leaders amidst the ongoing conflict in Ukraine.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (5)
Following this threat?
Track Lukoil Neftohim Burgas in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical Zero-Day Vulnerability in Cisco Secure Email Gateway Exploited On September 14, 2026, Cisco disclosed a critical SQL injection vulnerability (CVE-2026-76461) in its Secure Email Gateway, allowing unauthenticated remote attackers to execute arbitrary commands with root privileges. This vulnerability arises from insufficient validation in the email parsing logic. Cisco confirmed…
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…