Article Content

- •APT attacks are increasingly targeting financial institutions in 2026.
- •Organizations must shift from passive to proactive defense strategies.
- •Effective incident response requires coordination among IT and business teams.
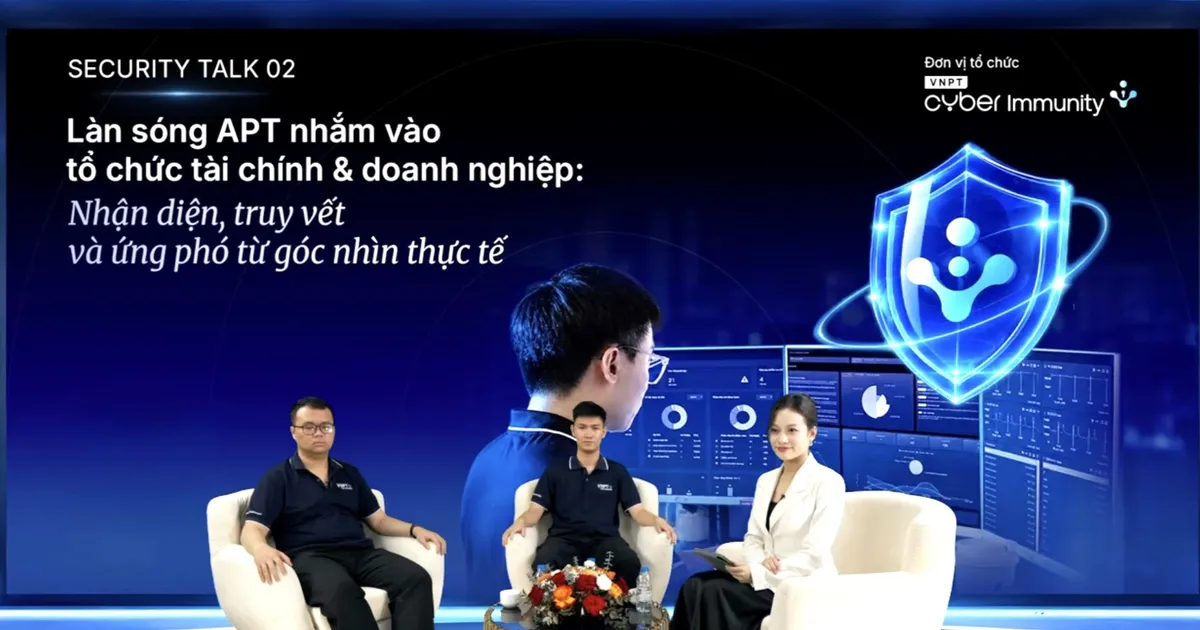
In 2026, advanced persistent threat (APT) attacks are increasingly targeting financial institutions and businesses in Vietnam and the Asian region. Cybersecurity experts from VNPT Cyber Immunity emphasize the need for organizations to adopt a proactive defense strategy against these stealthy and prolonged attacks. They recommend mastering three core layers of intelligence data: Indicators of Compromise (IoC), Indicators of Attack (IoA), and Tactics, Techniques, and Procedures (TTPs) to effectively identify and counter APT campaigns. The experts highlight the importance of continuous monitoring and coordination among IT and business operations teams to minimize damage. The incident response process includes detecting anomalies, gathering evidence, identifying the campaign, assessing the impact, and containing the attack. Businesses are advised to avoid focusing solely on immediate problem resolution and instead seek to understand the attack chain to prevent future incidents.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What are APTs targeting in 2026?
What should businesses do to prepare?
How can organizations respond to APT incidents?
Continue Reading
 Critical Authentication Bypass in Cisco Catalyst SD-WAN Manager Exploited On September 30, 2026, Cisco disclosed a critical vulnerability (CVE-2026-76504) in the Catalyst SD-WAN Manager that allows unauthenticated remote attackers to bypass authentication and gain admin-level access to the system. This flaw stems from improper handling of URI encoding in HTTP requests, enabling attackers to…
 Critical Authentication Bypass in Rejetto HFS Exploited Within 24 Hours Anthropic's Mythos model identified a critical authentication bypass in Rejetto HTTP File Server (HFS), tracked as CVE-2026-61500, allowing remote code execution. Discovered by Horizon3 researcher Zach Hanley, the flaw was revealed on September 27, 2026, and exploitation began within 24 hours, with attacks traced to…