 Powermag
BWXT Seeks NRC License for New HEU Enrichment Facility in Tennessee
Article Content

- •BWXT is applying for a uranium enrichment license for a new facility in Erwin, Tennessee.
- •The facility aims to restore domestic HEU production for naval nuclear propulsion.
- •Operations are expected to begin around 2035, creating approximately 100 high-skill jobs.
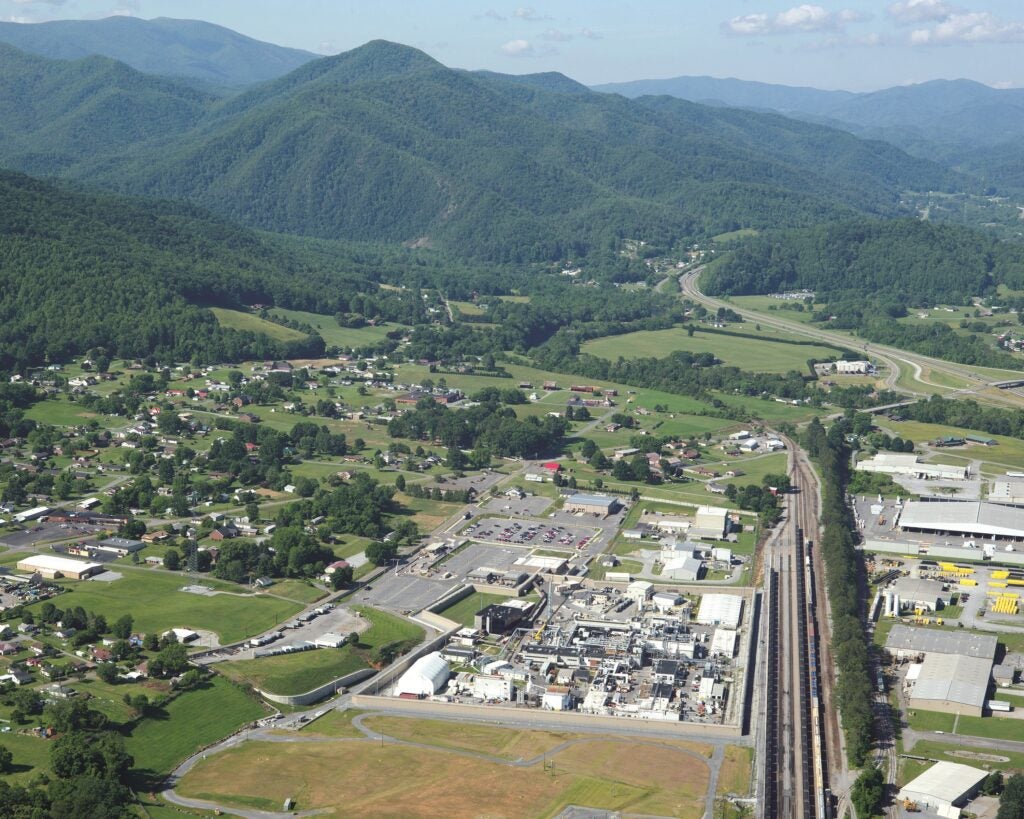
BWX Technologies (BWXT) has notified the U.S. Nuclear Regulatory Commission (NRC) of its intent to apply for a uranium enrichment license for a new facility in Erwin, Tennessee. This facility is part of a $1.5 billion contract with the Department of Energy’s National Nuclear Security Administration (NNSA) aimed at restoring domestic production of highly enriched uranium (HEU) for naval nuclear propulsion. The Erwin facility will be adjacent to BWXT's existing Nuclear Fuel Services (NFS) site and is expected to create approximately 100 high-skill jobs. The facility will utilize advanced centrifuge technology developed through the Domestic Uranium Enrichment Centrifuge Experiment (DUECE) at Oak Ridge National Laboratory. BWXT plans to submit the formal license application in the first quarter of 2027, with operations anticipated to begin around 2035. This initiative is critical for ensuring a reliable U.S. supply of enriched uranium for national defense and security needs.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…