 donjon.ledger.com
Critical Flaw in Tangem Crypto Cards Exposed by Ledger Researchers
Article Content

- •A critical vulnerability allows password resets on Tangem cards via laser attacks.
- •The attack requires specialized equipment costing approximately $250,000 and physical access.
- •The vulnerability is unpatchable due to the lack of firmware updates for Tangem cards.
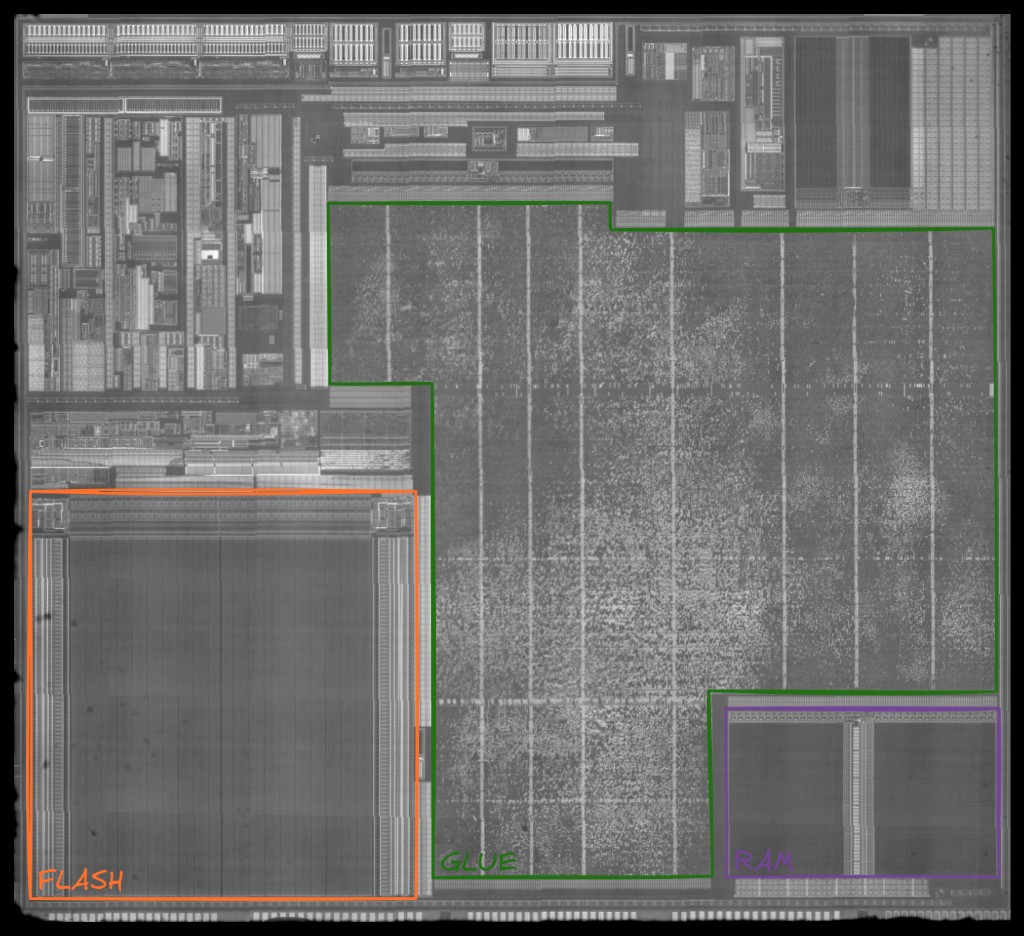
Ledger Donjon researchers disclosed a critical vulnerability in Tangem hardware wallet cards that allows an attacker to reset the card’s password through a laser fault injection attack. This exploit requires physical access to the card and specialized equipment costing around $250,000. The vulnerability affects all Tangem cards currently in circulation and cannot be patched due to the lack of a firmware update mechanism. The attack bypasses the firmware check that verifies the card's recovery state, allowing unauthorized password resets. Although the attack requires significant resources and expertise, it poses a risk if a card is lost or stolen. Tangem has disputed the practical significance of the findings, claiming the risk to everyday users is virtually non-existent. The vulnerability was disclosed to Tangem in February 2026, prior to public announcement.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (5)
Common questions
What is the nature of the vulnerability?
Can this vulnerability be patched?
What should users do to protect themselves?
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…